
data + ai + infosec engineering. @squirrelscan_ @opennem. at https://nitter.gq/t.co/yOGtW7uHIA and https://nitter.gq/t.co/kvkcg5TrG9
Australia
Joined March 2007
- Tweets1.7K
- Following763
- Followers459
- Likes4.4K
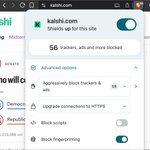


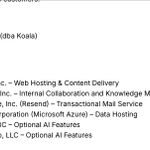


If you want to do the same Polymarket style hack to Kalshi you have 2-3x the surface area to attack - they embed and execute Javascript from 37 different third parties.


We've identified & fixed an issue impacting our international platform, Polymarket.com. One of our 3rd party providers was compromised, and we have referred this to relevant law enforcement.
Anyone who has been impacted will be made whole.
Out of an abundance of caution, we have temporarily halted trading & are working to bring the platform back online.
had no idea things were this bad ... F


Nik Cubrilovic retweeted

We audited 3 months worth of Product Hunt launches with squirrelscan (~20k sites)
69 sites were leaking real credentials or user data to every visitor. A live Stripe secret key. Supabase service_role keys. A dump of user records with password hashes.
🧵


Apple sensitive content warning uses on-device image detection models - a privacy respecting way of filtering content. It's described here (you can disable it):
support.apple.com/en-au/1050…


Phone numbers aren’t authenticated and can be spoofed.
We can’t be far away from banks and other critical apps abandoning phone support for in-app support only


How do you write an entire book about teenage hackers hijacking the internet and not know what PHP is? It would be the main character ..


BYO iPhone as a diplomat is a security nightmare - they all know that. It's a choice between having a secure gov device + network but having to comply with records retention + preservation, or going in raw into a hostile environment but being able to remain freelance

The GRU hacked into Jared Kushner's iPhone. Dutch military intelligence (MIVD) then recruited a GRU spy who gave them access to the hacked phone. What MIVD discovered was that Kushner had access to two bank accounts --one Azerbaijani, the other Israeli --where Saudi Crown Prince Mohammed bin Salman and Emirati ruler Mohammed bin Zayed deposited money. It sounds like a slightly far-fetched episode of "Slow Horses," but it's real. And it proves just how eye-poppingly corrupt this administration was and continues to be as its "special envoy" decides the fate of tens of millions in Europe in the Middle East. Simply incredible reporting by Matthew Cole, drawn from his new book on Kushner. vanityfair.com/story/jared-k…

Seemingly launched with support for every agent out there except OpenClaw and Hermes - both starting to feel a bit dead in the discourse

Today we announce 1Password for Agents platform, building with companies @Muse, SpaceX Super Intelligence Grok @Bot, @AnthropicAI’s @Claudeai, @OpenAI, @TownAI, @Browserbase, @Browser_use, @heydana_ai, Instinct, @usekernel, @Perplexity_ai, @tryramp, @Tomo, and @wajo_ai, with more integrations on the way. 🎉
We've heard from so many of our customers who want to use these new personal AI agents to help them get more done, but want more control over what the agent can access with the same trust and ease of use they get when using 1Password directly.
1Password for Agents gives your agents access without giving up your passwords. When an agent reaches a sign-in form, it requests a credential from your vault. If you approve the request, 1Password directly auto-fills the credential in the destination site so the agent can’t see or take possession of the credentials.
The agent gets the task done, but it doesn’t get your passwords..
You stay in control. 1Password for Agents free and optional for personal and family accounts. Unless you opt-in to an agent connector, agents cannot touch your vault.
➡️Learn more: bit.ly/487da6J

Reminder that ad blockers are absolutely an essential part of staying safe and secure on the internet

Israeli firm used online ads to run vast spy operation, researchers say reut.rs/4jofeOF reut.rs/4jofeOF


Digger is seeing this viral / word-of-mouth awakening in its third week of release. My local theatre pulled it - I got to catch the final session on a weekday morning this week - it was half full after every prior session selling < 10 tickets.

The previews and media tour and initial reviews didn't help - but this is starting to feel like Blade Runner, Donnie Darko, Fight Club et al where it becomes a cult hit and critics then re-evaluate.
Nik Cubrilovic retweeted

Your coding agent can write the fix. It still needs to find the website problem.
squirrelscan is an open-source CLI website QA tool for builders using coding agents.
It helps you audit a site and give your agent specific fixes by crawling it against 300+ rules across SEO, performance, security, accessibility, and agent experience.
Key features:
• Broad audit coverage – 300+ rules across 21 categories cover website QA in one CLI
• Agent experience checks – tests whether agents can discover, read, and act on your site
• MCP and skills support – connect the tool to coding agents and run audit-and-fix workflows
• Incremental crawling – uses ETag, Last-Modified, and content hashing, with checkpoints for resuming
• Flexible reports – export findings to console, JSON, HTML, Markdown, text, LLM, or XML formats
It’s open-source (MIT license).
Link in the reply 👇

Great way to publish benchmarks :)

Evals?!?!?!
As you all know, I dislike public benchmarks, but we do have to measure intelligence somehow.
We are trying an experiment in communicating our internal measure of intelligence.
See the blog for more details, but don’t treat it like it’s absolutely gospel, and you don’t even have to believe it fully, and it’s likely biased to our models so feel free to only pay attention to the relative ranking of open models. Shout outs to the Kev guy!
(We did not include hosted models because of what they do with their data and we want to keep our validation set very secure…)


