

Expert bug bounty and crowdsourced security marketplace · 400+ programs · $ 26M + paid in bounties · 85k+ ethical hackers
Start bug bounty journey →
Joined May 2018
- Tweets7.2K
- Following2.2K
- Followers39.9K
- Likes11.3K





Pinned Tweet
9+ years of experience in crowdsourced security.
Over the years, HackenProof has built a global security community and helped organizations strengthen their security through:
▪︎ 500+ secured programs
▪︎ 85,000+ vulnerability reports
▪︎ 1,100+ Critical vulnerabilities identified
▪︎ $95B+ assets connected to secured systems
For businesses, security is ultimately about managing risk. Our experience helps organizations make vulnerability discovery a continuous part of that process.
Secure Your Product with HackenProof→ hackenproof.com/contacts
#Cybersecurity #BugBounty #ApplicationSecurity #HackenProof

Should you choose a pentest or a bug bounty?
It depends on what you need from security testing.
A pentest is fixed-scope and time-boxed, making it useful for launches, major changes, compliance, and formal security reporting.
A bug bounty is continuous and crowdsourced, giving independent researchers more time and different perspectives to test a live product.
For many teams, the strongest approach is to use both. A pentest can establish the baseline, while a bug bounty can continue looking for vulnerabilities as the product changes and new issues emerge.
Not sure which you need? Let’s talk → hackenproof.com/contacts

8
856

HackenProof retweeted

🔔 Don't forget, tomorrow is our Zypto X Spaces!
🤖 How Much of a Threat Is AI to Crypto?
Don't forget another great space with amazing guests from
@HackenProof, @BiconomyCom, @hiveblocks, @Dashpay
🎁 Giveaway sponsored by @Zypto_Token for live listeners!
🔹 Host: @VoiceofDefi
🔹 Co-host: @ZyptoApp
Wednesday, November 11 at 15:30 CET (14:30 UTC) 👇

This Wednesday we're back with another Zypto X Space and a topic that is on everyone's mind right now 🎙️
🤖 How Much of a Threat Is AI to Crypto?
Hacks are getting more frequent, scams are getting smarter and AI is making both easier to pull off. But the same technology is also helping builders ship faster and security teams catch threats earlier. This Wednesday we ask how big the threat really is, and whether AI could also turn out to be our best defence.
Wednesday, November 11 at 15:30 CET (14:30 UTC)
🎁 Giveaway sponsored by @Zypto_Token for live listeners!
🔹 Host: @VoiceofDefi
🔹 Co-host: @ZyptoApp
Set your reminder 👇
nitter.gq/i/spaces/1kEvVmrWZNLqA…
✅ HackenProof has completed a Curated Smart Contract Audit for @DarkSwapApp!
DarkSwap is a privacy-focused platform built on NEAR Intents, enabling private cross-chain swaps.
The audit covered DarkSwap's Solidity and Rust-based ZK pool implementations for EVM and Solana, focusing on transaction logic, protocol fees, deposits, withdrawals, and access controls.
Great to support DarkSwap as it develops privacy-focused DeFi infrastructure.
📄 Read the full audit report: hackenproof.com/audit-portfo…

How much of a threat is AI to crypto?
Join us today as we discuss this with @ZyptoApp and fellow industry experts!
nitter.gq/i/spaces/1kEvVmrWZNLqA…
🔔 Don't forget, tomorrow is our Zypto X Spaces!
🤖 How Much of a Threat Is AI to Crypto?
Don't forget another great space with amazing guests from
@HackenProof, @BiconomyCom, @hiveblocks, @Dashpay
🎁 Giveaway sponsored by @Zypto_Token for live listeners!
🔹 Host: @VoiceofDefi
🔹 Co-host: @ZyptoApp
Wednesday, November 11 at 15:30 CET (14:30 UTC) 👇
The HackenProof Halloween Quest has officially come to an end!
Thank you to everyone who joined the challenge, solved puzzles, and made their way through our haunted cybersecurity lab.
🏆 Our Top 3 Security Researchers:
🥇 @Cutiapreta
🥈 @styphoiz
🥉 @weap0nlord
Congratulations on making it to the top of the leaderboard!
Thanks to everyone who took part in #HackenProofEscape. We hope you enjoyed the challenge!

1
27
1,500
HackenProof retweeted

Wow, what an intense 7 days in Mumbai! 🇮🇳🔥
- The week started with DeFi Security Summit @summit_defi, and what a great way to kick things off! So many security researchers, important discussions, and a really engaged audience. Huge thanks to @SagivMooly 🤝 and everyone who joined my talk. I really enjoyed the interaction!
- Then came @EFDevcon 8, which was definitely my most active Devcon ever!
- I spent two days as an Emcee, gave a talk on the Lightning Stage, and participated in the Legal Hub. And I absolutely loved every minute of it. This is my element!
- What I especially appreciate about Devcon is that people don't come here to sell or buy things. They come to share knowledge, challenge ideas, and learn from each other. And you can feel it everywhere. The rooms were packed!
- My personal discovery of the week was Ross @_rossstephenson, our MC Lead! I think I received more messages from Ross this week than from my entire family combined 😅! Ross, fantastic job!
- Being an MC also gave me the chance to get to know and work with 30+ incredible people on the MC team. And here's what made that experience special: nobody cares whether you're a Dev, CTO, Founder, or anything else. We all have one mission — to help speakers and audiences connect and make every session a great experience. I loved being part of this team!
- A big thank you to the Meerkat team for the support! Already looking forward to seeing what new features you'll bring to the app next year.
-And of course, it was wonderful to meet so many people from the @HackenProof security community. We talked, took photos, shared stories, and simply enjoyed seeing each other in person. These moments mean a lot!
A few topics that really caught my attention this week:
▪︎ Formal verification is going to be a major topic in 2027. I expect we'll see many new projects in this space.
▪︎ AI agent identity, policies, and agent-to-agent interactions are becoming incredibly interesting areas. There's huge potential, but also a lot of work ahead.
▪︎ Post-quantum cryptography received less attention than I expected, but the interesting part is that people no longer treat it as a distant problem.
▪︎ Security Hub by @thedaofund had some excellent talks, and the room seemed to be packed all the time!
▪︎ Ethereum Improvement Proposals brought some interesting discussions, especially around EIP-7906.
▪︎ AI-powered security report validation is gaining momentum. I even met students working on their theses in this area!
▪︎ And one big question that still doesn't have a clear answer for many teams: How do we fix vulnerabilities faster when the pipeline of security findings keeps growing?
Finally, a few words about Mumbai.
It's a city full of contrasts, energy, diversity, and constant development. A huge thank you to everyone in India who welcomed us so warmly, supported us throughout the week, and even saw us off at the airport. ❤️
And one last thing...
I'm not going to brag, but I actually guessed where the next Devcon would be! 😎
See you at Devcon IX in Lisbon! 🇵🇹


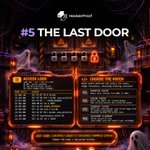
🎃 #5 The Last Door
You've reached the final exit.
But the door remains locked.
You know where the security system fails. Now you need to prove what happened.
Your final mission: Examine the access logs, identify the first unauthorized access, and choose the patch that enforces the security policy for every badge revocation.
Use the clues you've collected to reconstruct the exit code.
Submit your exit code and two log events that prove the unauthorized access.
Can you finally make it out?
🔍 Find all five puzzles under #HackenProofEscape

3
9
1,466
Top 3 researchers this week:
🥇 @keterka
🥈 Otter11
🥉 @anchabadze
Nicely done!
Want your handle here? Join active programs: hackenproof.com/programs

HackenProof retweeted
How’s your @EFDevcon going so far ?)
The closing ceremony is coming up soon! Everyone's trying to guess where the next Devcon will be hosted.

Looks like we’re almost packed for Web Summit 2026!
The HackenProof team is getting ready for Lisbon – and yes, the merch is coming with us 👀
From November 9–12, you’ll find us at @WebSummit.
See you in Lisbon!
#WebSummit #WebSummit2026 #Cybersecurity #HackenProof

1
24
1,341
✨ New HackenProof Pages Are Live
We’ve redesigned key public pages across HackenProof to make navigation clearer and the overall experience more consistent.
What’s new:
✔︎ Bug Bounty Program pages
✔︎ Audit Program pages
✔︎ Public Reports
✔︎ Public Company Profiles
✔︎ Blockchain Auditors directory
✔︎ Public Blockchain Auditor Profiles
We’ve also added search within program scope, allowing researchers to find specific targets directly on the program page.
Explore the updated HackenProof experience 👇
hackenproof.com/
🚨 Cost per successful breach: ~$50 in AI tokens.
According to a recent Reuters report, a cybersecurity researcher tracked an operation where AI agents were used to target more than 1,200 websites linked to over 100 companies. Successful intrusions took around 23 hours on average, while the estimated cost of AI usage for the campaign was roughly $5,000.
The important part isn’t just the numbers.
One operator can now orchestrate AI agents to work across hundreds of targets, continuously probing for weaknesses with limited human involvement.
If attackers can test at this scale, security testing can’t remain periodic.
As attack capabilities scale, organizations may need to rethink how often and how broadly they test their security.
Secure Your Product with HackenProof → hackenproof.com/contacts

Some things aren't new to us. 👀
Over 7 months ago, HackenProof became the first bug bounty platform to introduce paid submissions with refunds for duplicate reports built in from day one.
Here’s what we’ve achieved so far:
▪︎ $5,679 refunded to security researchers
▪︎ 1,000+ reports covered by refunds
▪︎ $1–$5 submission fees, among the lowest in the market
The goal was never to profit from submission fees. It was to reduce spam, improve the signal-to-noise ratio, and make bug bounty more effective for both researchers and security teams.
And that hasn't changed.
