

Designed by TokenPocket for security and ease of use. MCU+SE dual-chip Offline storage & signing Supports millions of assets.
Joined July 2021
- Tweets665
- Following99
- Followers5.6K
- Likes634




KeyPal Announces a 15-Day Personal Data Cleanup Policy to Strengthen User Privacy and Data Security
Recent incidents involving user information leaks and supply chain security risks in the hardware wallet industry have once again highlighted the importance of personal privacy protection and data security management.
As TokenPocket’s hardware wallet brand, KeyPal’s commitment to user security extends beyond devices and private keys to the protection of personal information generated throughout the purchasing, delivery, and service process.
The security boundary of a hardware wallet should not be limited to private key storage and transaction signing. Personal information generated during device purchases, logistics delivery, and after-sales services is also an essential part of the overall security framework. If such data is unlawfully obtained, it may be used for targeted phishing, identity impersonation, and other forms of social engineering attacks.
As of the date of this announcement, KeyPal has not identified any exploited security vulnerabilities in its systems or any incidents involving customer data leakage. These adjustments are part of a proactive security governance initiative in response to evolving industry risks and are not remedial measures taken in response to any specific security incident.
KeyPal has long maintained internal data security management standards covering customer information protection, access control, and data deletion. As the industry security environment continues to evolve, we have decided to further strengthen our data governance standards, conduct a dedicated review of our existing systems and third-party services, and implement the following measures.
Comprehensive Review of Historical Data and Access Permissions
We will reassess historical order data stored in Shopify and related business systems, reviewing the storage status of personal information, deletion records, and access permissions.
We will also examine third-party applications, exported data files, and other locations where redundant customer data may exist.
For customer information that no longer has a reasonable need to be retained, we will proceed with deletion in accordance with applicable regulations and system capabilities, reducing potential security risks associated with the unnecessary accumulation of historical data.
Reducing the Retention Period for Non-Essential Personal Information to 15 Days
For orders where delivery has been confirmed, fulfillment has been completed, and there are no unresolved after-sales disputes or other lawful retention requirements, KeyPal will aim to delete or de-identify non-essential customer personal information within 15 days after order completion.
To better balance user privacy with after-sales service rights, we will also explore more independent warranty and device verification mechanisms. Service eligibility may be verified through information such as order numbers or device serial numbers, reducing reliance on complete historical customer records.
For financial, transaction, and after-sales records that must be retained by law, we will implement appropriate access restrictions and security protections and delete such information promptly once the applicable retention requirement no longer exists.
Tightening Data Access Boundaries for Third-Party Services
We will continue reviewing data interaction mechanisms across e-commerce, payment, logistics, and related service systems.
Following the principle of data minimization, we will limit unnecessary information sharing and promptly revoke system permissions that are no longer required.
It should be noted that logistics carriers and other independent service providers may retain certain information in accordance with their own business policies and legal obligations. Their data retention periods are not fully under KeyPal’s control.
Therefore, the 15-day deletion target primarily applies to personal information that falls within KeyPal’s direct control and meets the conditions for deletion.
For third-party services, we will continue to promote stronger data protection practices, but we cannot guarantee that all service providers will adopt identical retention periods.
Separating Subscription Information from Transaction Data
For users who voluntarily subscribe to official KeyPal communications, we may retain necessary email address information separately, subject to appropriate user authorization.
Where possible, this information will be separated from historical order data, shipping addresses, and other identifying information.
It will only be used for communications that users have agreed to receive, including product updates, firmware upgrades, security fixes, and important service notifications. Users will also retain the ability to unsubscribe.
Continuing to Improve Control Over Our Data Infrastructure
At present, part of KeyPal’s e-commerce operations rely on third-party platforms such as Shopify.
We will continue evaluating the capabilities of our existing architecture in areas including data lifecycle management, access control, and security auditing, while exploring technical solutions that provide greater levels of independent control.
Any architectural changes will be implemented with security, regulatory compliance, and business continuity as core considerations.
We will also take into account practical requirements such as payment processing, order fulfillment, after-sales services, and fraud prevention to ensure that privacy protection measures remain balanced with the quality and reliability of user services.
For KeyPal, user privacy is not an additional issue separate from product security. It is an important component of the broader digital asset security framework.
Our long-term direction is to reduce the unnecessary generation and movement of personal data, shorten the period during which sensitive information remains exposed, and reduce potential risks through clearly defined data management boundaries.
No system can provide an absolute guarantee of security. KeyPal will continue improving its user privacy protection framework through ongoing review, prudent governance, and practical, enforceable security measures.
KeyPal — Your Secure Crypto Hardware Wallet.
keypal.pro

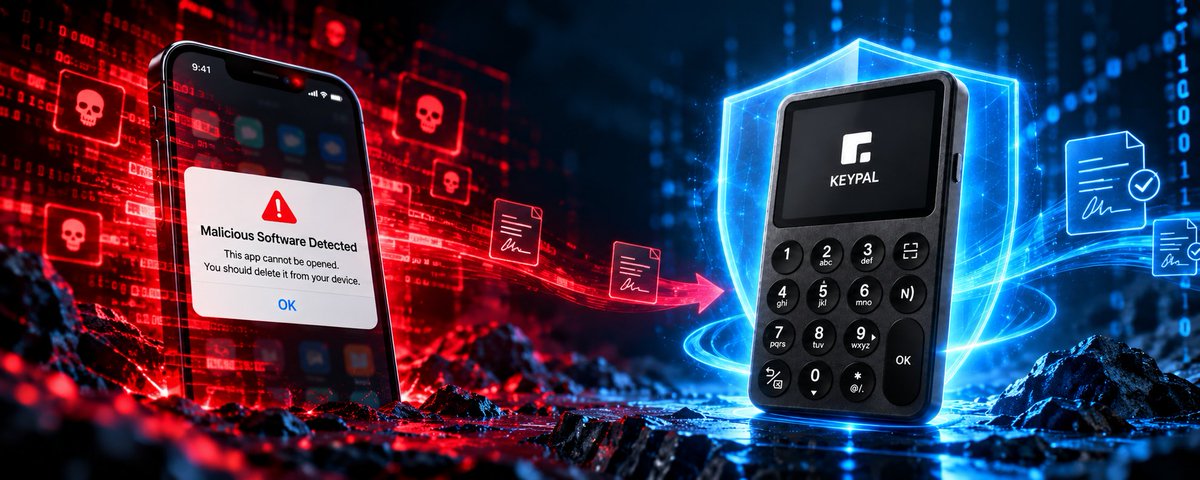
Switch to #KeyPal 2 and get 50% off for a limited time.
Pair it with TokenPocket’s @TokenPocket_TP native multisig and cold wallet for layered protection.
👉 keypal.pro

KeyPal Hardware Wallet retweeted

The right move. 👀
Switch to KeyPal 2 and get 50% off for a limited time. @KeyPalWallet
Pair it with TokenPocket’s native multisig and cold wallet for layered protection.
👉 keypal.pro/

KeyPal Hardware Wallet retweeted
Exclusive for Ledger & Trezor users:
Switch to KeyPal 2 and get 50% off 🔐 @KeyPalWallet
Incubated by TokenPocket, built for secure self-custody:
• Military-grade dual-chip security
• Passphrase support
• QR code & Bluetooth connectivity
• Quick NFC backup
🛡️Pro tip: Take your security further by pairing KeyPal 2 with TokenPocket’s native multisig wallet and cold wallets for layered protection.
Order now: keypal.pro/

KeyPal Hardware Wallet retweeted

. @KeyPalWallet (the hardware wallet incubated by @TokenPocket_TP) is launching a 50% off promotion for hardware wallet users impacted by the CryptoBilis incident, helping them complete a secure migration.


KeyPal Hardware Wallet retweeted

上午拆了个 @KeyPalWallet 结合官方给的硬件结构对比:
keypal.gitbook.io/zh-cn/user…
很清晰,一目了然。硬件钱包这种利于验证的机制越全面越好!


【KeyPal Official Purchase Reminder】
When purchasing a hardware wallet, use official channels and carefully verify the seller’s identity and the product’s source to help protect your assets.
KeyPal has no partnership with the reseller mentioned in the recent incident. To purchase KeyPal products, please visit our official website: keypal.pro
Thank you for your trust and support.


🎉 Giveaway Winners Are Here!
Thank you so much for joining our giveaway! 💙
Congratulations to all the lucky winners! 🎁
🎉 Winners:
@Ajmeer181565 @EluuPaul84179 @ounbear
📧 Coupons have been sent to the email addresses provided by the winners.
Please check your inbox to make sure you don't miss your coupon.
⏰ Coupon Validity: September 25 – October 8, 2026
Coupons will automatically expire after the validity period, so please make sure to use them before the deadline.
⚠️ Important Eligibility Notice:
To be eligible for this giveaway, participants must follow @KeyPalWallet and provide a valid X (Twitter) username in the giveaway entry form.
The following cases will be considered invalid entries:
· Providing an email address but not actually following @KeyPalWallet
· Failing to provide an X (Twitter) username in the giveaway entry form
· Providing an X (Twitter) username that cannot be verified
Didn't win this time? Don't worry! 👀
More exciting events and rewards are on the way. Stay tuned!
Follow KeyPal — you could be our next lucky winner! 🎃✨


KeyPal Hardware Wallet retweeted

🎁 2 EXTRA KeyPal Hardware Wallets worth $200 each are up for grabs! Don’t miss out!
⛽ Pay gas with $USDD on @TokenPocket_TP and enjoy a 50% gas subsidy!
🎁 Double the rewards:
🔹 5,000 USDD + KeyPal Hardware Wallets up for grabs!
🔹 2 lucky users who complete a qualifying transfer using USDD for gas and submit the form will each win a KeyPal Wallet!
🏆 Complete quests & climb the leaderboard: zealy.io/cw/tokenpocket/lead…
📝 Try USDD for gas & submit your entry: forms.gle/vEcebVGja5mabCrY8
📅 Ends Sep 28. Don't miss your chance! 💚


⛽ TokenPocket ✖️ USDD Gas Boost Season!
🎁 5,000 ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a + KeyPal Hardware Wallets Up for Grabs!
→ zealy.io/cw/tokenpocket/lead…
Use ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a. Save on Gas. Complete Quests. Earn Rewards.
Pay gas with ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a on TokenPocket and enjoy a 50% gas subsidy while completing onchain quests.
Climb the leaderboard and claim your share of the rewards.
📅 Sep 15 – Sep 28
Powered by @USDDecentralize × @TokenPocket_TP × @KeyPalWallet
#USDDonTP #USDDForGas #TokenPocket

I don’t need to convince you to buy #KeyPal 2. It just happens to match everything you need.

👍 CC EAL6+ secure chip.
👍 Passphrase protection.
👍 QR + Bluetooth signing.
👍 NFC backup and seed phrase import.
A hardware wallet built for people who already know what self-custody means.
#KeyPal 2 — your assets, your control.
keypal.pro

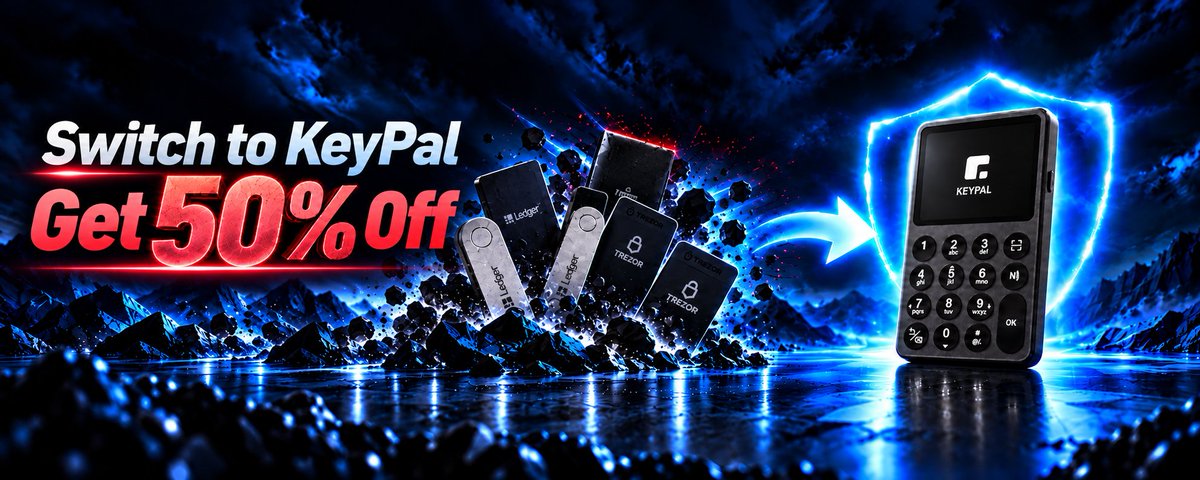
Smartphone Vulnerabilities Surface Every Year. How Can Onchain Assets Avoid a Single Point of Failure?
Recently, SlowMist and the OKX security team issued a risk alert concerning versions 1.1–1.2 of FomoPeek.
According to their disclosure, the app contained malicious modules unrelated to its stated functions, including an iOS kernel exploitation framework. If successfully exploited, the malicious code could potentially break out of the iOS sandbox and access Keychain data, Notes, and files belonging to other apps—putting private keys, recovery phrases, login credentials, and chat records stored on the phone at risk.
The most important lesson from this incident goes beyond one malicious app:
When internet access, app downloads, web browsing, communication, and private-key storage all depend on the same smartphone, a compromise of the operating system may expose multiple apps and data sources that were previously isolated from one another.
Why Do Smartphone Vulnerabilities Appear Every Year?
Modern mobile operating systems simultaneously support browsers, cameras, Bluetooth, cloud synchronization, payments, and a vast range of third-party apps. The more complex the system becomes, the larger its potential attack surface.
Under normal conditions, iOS and Android use sandboxing, permission controls, and encryption to isolate apps and their data. However, attackers may combine multiple vulnerabilities into an exploit chain:
Malicious app execution
→ Permission bypass
→ Sandbox escape
→ Elevated system privileges
→ Access to other apps or system data
→ Exfiltration of sensitive information
This is why system updates do more than introduce new features—they also patch known security weaknesses.
Apple’s iOS 27 security advisory includes issues such as sandboxed apps potentially executing code with kernel privileges and apps potentially accessing sensitive user data.
However, this does not mean Apple has confirmed that these vulnerabilities correspond directly to the FomoPeek exploit chain. The precise scope of the incident should be assessed based on further disclosures from Apple and the security teams involved.
Why Do Software Wallets Depend More Heavily on Smartphone Security?
Reputable mobile wallets typically use passwords, biometric authentication, and local encryption to protect private keys. However, the storage, decryption, and signing processes still operate within the smartphone environment.
If malicious software gains elevated system privileges, it may attempt to access wallet data, monitor user input, inspect memory, or locate recovery phrases stored in Notes, photos, the clipboard, or messaging apps.
A device password, fingerprint, or Face ID can prevent an ordinary person from opening the phone, but it may not stop malicious code that is already exploiting an operating-system vulnerability.
This does not mean mobile wallets should not be used. It means assets should be managed in layers:
Mobile wallets can be used for daily interactions and smaller balances.
Long-term holdings and higher-value assets should have an independent security boundary for private keys.
What Does a Hardware Wallet Change?
The core value of a hardware wallet is not simply the addition of another device. It separates private-key generation, storage, and transaction signing from an everyday internet-connected smartphone.
Using KeyPal 2 as an example:
• It uses a dual-chip architecture consisting of an SE secure element and an MCU. The SE is certified to CC EAL6+, while private keys are generated using true hardware randomness.
• It supports QR code, Bluetooth, and USB connections. The phone constructs and broadcasts transactions, while the private key does not need to leave the hardware wallet during normal operation.
• It features an independent LCD screen and physical buttons, allowing users to verify transaction details and confirm signatures directly on the device.
• It supports the recognition and display of PSBT, EIP-712, EIP-7702, Approve, Permit, Permit2, and other transaction or authorization types.
• It supports Passphrase protection, TokenPocket multisig, and encrypted NFC recovery-phrase backups using a KeyPal Card with its own secure element.
This architecture means that even if the smartphone is compromised, an attacker cannot obtain the private key stored inside KeyPal 2 simply by reading the phone’s storage.
The smartphone remains responsible for connectivity, while the private key that determines asset ownership remains inside a dedicated device.
A Hardware Wallet Does Not Mean “Absolute Security”
A hardware wallet is not antivirus software, nor can it repair a smartphone that has already been compromised.
If a phone is under an attacker’s control, the attacker may still attempt to replace a recipient address, construct a malicious authorization request, imitate a DApp interface, or trick the user into signing a high-risk Approve, Permit, or Permit2 transaction.
The hardware wallet’s independent screen is therefore not a decorative feature. It is the final verification layer before a transaction is signed.
When using a hardware wallet, users should follow several essential principles:
Treat the information displayed on the hardware wallet as authoritative. Verify the address, amount, network, and authorization target.
Do not approve transactions or messages you do not understand—especially unlimited approvals and complex message signatures.
Never enter a recovery phrase into a smartphone, website, or chat window, and never store it in Notes, photos, email, or cloud storage.
If a recovery phrase may have been exposed before being imported into a hardware wallet, generate a completely new one and transfer the assets to new addresses.
For higher-value assets, consider combining Passphrase protection with multisig to reduce the risks associated with the compromise of a single device or key.
Keep the smartphone operating system, wallet app, and hardware-wallet firmware updated, and download software only from official sources.
Real security does not come from assuming that one device will never have a vulnerability.
It comes from ensuring that a single smartphone compromise does not automatically become a private-key compromise.
Let your phone connect to the world.
Let your private keys remain within an independent security boundary.
KeyPal 2
Secure · Easy to Use · Portable
keypal.pro
Apple iOS 27 security advisory:
support.apple.com/en-hk/1490…
#KeyPal #KeyPal2 #HardwareWallet #CryptoSecurity #Web3Security

KeyPal Hardware Wallet retweeted
⛽ TokenPocket ✖️ USDD Gas Boost Season!
🎁 5,000 ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a + KeyPal Hardware Wallets Up for Grabs!
→ zealy.io/cw/tokenpocket/lead…
Use ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a. Save on Gas. Complete Quests. Earn Rewards.
Pay gas with ethereum:0x4f8e5de400de08b164e7421b3ee387f461becd1a on TokenPocket and enjoy a 50% gas subsidy while completing onchain quests.
Climb the leaderboard and claim your share of the rewards.
📅 Sep 15 – Sep 28
Powered by @USDDecentralize × @TokenPocket_TP × @KeyPalWallet
#USDDonTP #USDDForGas #TokenPocket