

Official account of MalwareMustDie, NPO & public account @unixfreaxjp Info: https://nitter.gq/t.co/131r5UW4bF Blog: https://nitter.gq/t.co/lUnpKnXOqV
Joined September 2018
- Tweets714
- Following144
- Followers5.8K
- Likes326






A lot of improvements in Iaito (radare2)
Now it is as sharp as my katana irl :)
Thank you @radareorg @trufae <3
#MalwareMustDie!

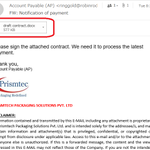
Okay.. this #malware actor's efforts continues. New #email malvertisement w/domain robinrodriguez[.]info via spambot at 161[.]248.238.122 at same AS150895/EZ TECHNOLOGY in #Vietnam, w/same payload "Protected .py" saved in #sendspace camouflaged in a zipped python windows pkg. The evil docx is now using new obfusctated JS loader to exec encoded powershell downloader, triggered by same cve #EQUEDIT exploit. It aims signature evasion, with same infection #backdoor motivation.
See attached pictures for better understanding. Block that sendspace url & final #stager hashes.
docx: virustotal.com/gui/file/fc04…
js: virustotal.com/gui/file/4062…
#MalwareMustDie!


Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!


Thank you @freebsd & @cperciva for the great news. I've been waiting for this. Will test in on my Vortex86DX3 & Raspberry PiZero2W box before production.
Memo: time for #pkbase switching, fixes: userland package (libc stuff), old OpenZFS bug, more info at #freebsd announce: freebsd.org/releases/14.4R/a… & notes: freebsd.org/releases/14.4R/r…
Update/upgrade, red this 1st: docs.freebsd.org/en/books/ha…

2
834
Okay, listen up. THIS (see prev thread) #malware campaign is on-going, even now. Adversaries are in control of these .INFO domains:
crystalogletree[.]info, coraliereinger[.]info and kevinsaad[.]info, Which they are spreading infection campaign relayed from various IP MTA located in this subnet 160[.]250.128.0/23 at AS150895/EZ TECHNOLOGY CO LTD, I attached. email they used for the infection.
Chains infection:
docx -> rtf -> xml obj #cve-2017-118822 load shellcode to decrypt & load another shellcode to execute malicious script in rtf (there are license.vbs/.js/Client.vbs) that downloads python312x86()zip contains evil Protected(py) to be persistence installed & executed, or execute a DLL binary of "license(.)ini" to be injected to into process.
That evil python is lastly served at sendspace(.)com/pro/dl/5qcr3i
So all of scripts used & binary will be heavily obfuscated. They tried hard to evade all checks and aiming unpatched #EQEDIT on older #msoffice app.
The above #IOC and #CTI info should be their #TTP so use information above to #block ur network in anyway you can.
Just saying, in a glimpse, it seems like adaptation of previously known as #hancitor docx campaign added w/ AI steroid. No, this isn't emotet, and no this is not Heodo/Geodo but could be the copycat.
#MalwareMustDie!!
Well, the adventure continues.. w/same bad-actors (pivoted attackers spambot: 160[.]250.128.165/VN) who's very eager to do more #malware CTF with me.
But.. the endgame is now different...an AI generated hash-obfuscated DLL loader..
See the pics of details & links (it has my hint to crack the hash), below is chain of infections:
docx: virustotal.com/gui/file/467f…
rtf: virustotal.com/gui/file/4289…
DLL loader: virustotal.com/gui/file/1a11…
#MalwareMustDie!


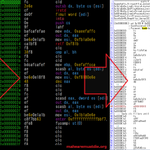
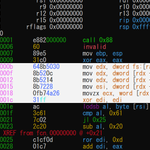
These are stagers used by adversaries embedded in (docx/rtf/xml) to exploit cve-2017-118822 w/overflowing buffer for font at EQEDIT, stuff that they don't change easily, so use this info to recognize this #malware threat & campaign in the future. I attached here my static analysis for stager 1 and stager2 #shellcode they use. #MalwareMustDie!
thanks @trufae for r2shell I use for this case! <3


Well, the adventure continues.. w/same bad-actors (pivoted attackers spambot: 160[.]250.128.165/VN) who's very eager to do more #malware CTF with me.
But.. the endgame is now different...an AI generated hash-obfuscated DLL loader..
See the pics of details & links (it has my hint to crack the hash), below is chain of infections:
docx: virustotal.com/gui/file/467f…
rtf: virustotal.com/gui/file/4289…
DLL loader: virustotal.com/gui/file/1a11…
#MalwareMustDie!
(smile) Someone at 160[.]250.128.122 spammed me w/docx email attachment..(downloader), it downloaded Protected.py (a persistent installer),then runs classic shed api shellcode with reversed shell injected to SndVol..(snipped part sc)..
to bad..no reg+SndVol in #BSD

(smile) Someone at 160[.]250.128.122 spammed me w/docx email attachment..(downloader), it downloaded Protected.py (a persistent installer),then runs classic shed api shellcode with reversed shell injected to SndVol..(snipped part sc)..
to bad..no reg+SndVol in #BSD
the whole #malware infection chain:
virustotal.com/gui/file/16da…
virustotal.com/gui/file/0d5d…
virustotal.com/gui/file/0d06…
virustotal.com/gui/file/7857…
to these bad actors, just make sure to exclude me from your spamlist ;-)

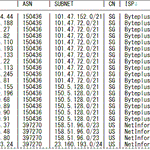
There are a lot of spear phishing originated fr infra at:
AS150436 Byteplus Pte. Ltd.
AS397270 Netinformatik
101[.]47.73.0/24
101[.]47.74.0/24
101[.]47.75.0/24
101[.]47.76.0/24
101[.]47.77.0/24
101[.]47.78.0/24
150[.]5.128.0/24
150[.]5.129.0/24
150[.]5.130.0/24
158[.]51.96.0/24
For AJCCBC Malware Analysis class members feel free to DM me started with stated your full name and country first. Let’s keep in touch, we had a great week together!
2
833

Just wondering how many of us are actually rebooting (turning off and on again) our mobile phone devices everyday?
#MalwareMustDie #Poll
19%I do
71%I don’t
10%I don’t know..
42 votes • Final resultsU.S. Commerce Department Prohibits Russian Kaspersky Software for U.S. Customers
bis.gov/press-release/commer…
Our comment: Completely AGREED.
1
2
881
#Blog: Back in 2015, where #Linux #Ransomware was started to came up to the surface, I posted an analysis that I forgot to post it in #MMD blog in English until just now..
So, I am sorry, better late than never. Here it is:
blog.malwaremustdie.org/2024…
#MalwareMustDie!
#Blog: I re-posted my older #APT #PoisonIvy analysis in #MMD blog before it becomes /dev/null :)
blog.malwaremustdie.org/2024…
#MalwareMustDie!
On behalf of #MalwareMustDie team, I, @unixfreaxjp of #MMD would like to congratulate @virustotal (@virustotalnews) for the 20th Anniversary!!
Congratulations friends, internet cyber security will not be the same if you are not around! Please keep up the great work for 20y more!
Serious matter.

CISA and review board torches Microsoft internal response and how bad the 2023 compromise actually was.
It was way worse than what was communicated from Microsoft - way way way worse and avoidable.
This is a good read and something folks really need to equate in their own threat models and risks in cloud - especially one as high profile as Microsoft/Azure.
Extremely alarming imo. Key highlights below is scary AF.
Also bang up job on this report from @CISAgov - grade A disclosure and documentation and analysis. Also, this isn’t me bashing the amazing folks that work at Microsoft.
Some of the most brilliant folks out there. What is clear is that there needs to be some serious and concerted effort on monitoring and massive momentum on additional security controls (esp keys to kingdom ?!) to protect their cloud infrastructure that other cloud providers already have that Microsoft is seriously lagging behind in.
Excerpt below:
“Given Microsoft’s inability to determine how and when the adversary was able to steal its signing key, all CSPs should review and revise as appropriate their logging and overall forensics capabilities around their identity systems and other systems that enable environment-level compromise, such as root key material.
1. the cascade of Microsoft’s avoidable errors that allowed this intrusion to succeed;
2. Microsoft’s failure to detect the compromise of its cryptographic crown jewels on its own, relying instead on a customer to reach out to identify anomalies the customer had observed;
3. the Board’s assessment of security practices at other cloud service providers, which maintained security controls that Microsoft did not;
4. Microsoft’s failure to detect a compromise of an employee's laptop from a recently acquired company prior to allowing it to connect to Microsoft’s corporate network in 2021;
5. Microsoft’s decision not to correct, in a timely manner, its inaccurate public statements about this incident, including a corporate statement that Microsoft believed it had determined the likely root cause of the intrusion when in fact, it still has not; even though Microsoft acknowledged to the Board in November 2023 that its September 6, 2023 blog post about the root cause was inaccurate, it did not update that post until March 12, 2024, as the Board was concluding its review and only after the Board’s repeated questioning about Microsoft’s plans to issue a correction.”
cisa.gov/sites/default/files…
2
1,092
To #Malwaremustdie friends in Cyber Threat Intelligence field, there is still a chance to publish your research in next year's April at #FIRSTCTI24, please see the detail in the re-posted context. You can contact @FIRSTdotOrg for more info.
Thanks! @unixfreaxjp
#cti #ctisig #mmd

Interested in speaking at #FIRSTCTI24? The #CallforPapers for this Berlin conference closes next week, December 13th. Get your submissions in now! For all #CFP details please see: ow.ly/GuxC50PWCPn

2
1,051
Thank you for all of friends for the amazing support along these 11years+.
If you are following our #malwaremustdie/#MMD's twitter/x account @malwaremustdie up to now & got disconnected please follow this official account to keep in touch. -- MMD
We have executed the #TsurugiLinux basic training for Japan security community in #hackfes23 #Tokyo w/ @unixfreaxjp of #malwaremustdie as instructor.
Wishing speedy recovery to @Sug4r7 & greets to @tsurugi_linux's dev friends @blackmoon105 @therebus from #Japan #dfir folks!
