

Securing every bit of your data https://xitter.cf/t.co/hqdd8jMkYM https://xitter.cf/t.co/GOXPtukIXE
Paris, France
Joined October 2011
- Tweets1.7K
- Following13
- Followers12.7K
- Likes606



PQC is coming they say, but where is the actual code?
To help you map it out, our intern Joshua Setia looked at and tested 25 libraries, here is what he found:
➡️blog.quarkslab.com/state-of-…

ALT DeltAFLy is a differential fuzzer for crypto and this is its logo. Delt-AFL-y get it?
Mbed TLS is a widely deployed open-source TLS, DTLS, and X.509 library targeting constrained and embedded environments.
A few months ago, our cryptography team performed a security audit of the changes in version 4.0, sponsored by @OSTIFofficial
➡️blog.quarkslab.com/mbedtls-s…
ohhh we've got Off-by-One bugs
The internship season is 2026-2027 😒
Good catch @fredraynal !
Still finding bugs after all those years

Our 2025-2026 internship season is open.
Check out the list of openings and apply for fun and knowledge!
blog.quarkslab.com/internshi…
Our 2025-2026 internship season is open.
Check out the list of openings and apply for fun and knowledge!
blog.quarkslab.com/internshi…
Reports can be the fun part of a pentest.. if the target uses MyReport.
@kaluche_ found a third-party updater running as SYSTEM, an unauthenticated gRPC service, and a nice way to turn software updates into arbitrary code execution.
From LPE to RCE🔥
blog.quarkslab.com/myreport-…

ALT MyReport brings the fun to reports in the pentests
Not an antivirus product this time, but we couldn't pass it up 🙈
@CatoNetworks said: route with split tunneling.
@kaluche_ heard: root with split tunneling.
Check out CVE-2026-10739, a LPE vulnerability in the Cato VPN Client for Windows
➡️ blog.quarkslab.com/cato-vpn-…

ALT a CatoVPN to your SYSTEM
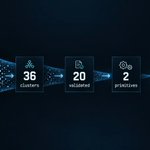
To leverage AI agents for vulnerability research, we built a hybrid source-code analysis workflow that combines deterministic analysis with agentic reasoning. Applied to FreeRDP, it helped us uncover vulnerabilities and chain them into client-side RCE.
blog.quarkslab.com/from-ai-a…

Optical network security often sounds like an obscure incantation: PON, ONU, OLT, PLOAM, OMCI, GEM, GPON, XG-PON, 50G-PON, T-CON..
To conjure the right knowledge read Thiébaud Fuchs' overview of Passive Optical Networks and their security features
blog.quarkslab.com/overview-…

ALT VSOL ONT OLT PON PING PONG CON WELLAPON
Chamilo LMS was put under the microscope🔬 by @Coiffeur0x90 and @_lec0_.
11 vulnerabilities, multiple attack surfaces. Our new research dives into the vulnerable code paths and exploitation primitives to achieve unauthenticated RCE.
🔗 blog.quarkslab.com/chamilo-l…

ALT Agentic Smith found vulns too
"Software protection is futile, AI will break it", they said.
But, does it? how?
To shine some light read about Rémy Salim's experiments in "Defeating AI-Assisted Reverse Engineering"
Where is the fair play, Claude?
blog.quarkslab.com/defeating…

Doing Machine Learning on binary code?
We've just open-sourced pcode_graph, a Python library that extracts semantic graphs from binaries to make training Graph Neural Networks easier.
Samuel Hangouët introduces it here:
blog.quarkslab.com/from-p-co…
#GNN #ML #Python #OpenSource

ALT It's a Data Flow Graph. No witty comment possible.
Everything about Android's hardware attestation... and how to bypass it.
Blog post and code by Eric Le Guevel
blog.quarkslab.com/bypassing…

ALT Keep on rooting in the free world
Cortex is a long-term, multi-tenant scalable open source storage for Prometheus and OpenTelemetry.
Earlier this year we conducted a security audit sponsored by @OSTIFofficial
Check our report here:
blog.quarkslab.com/cortex-se…
Obscure Element: Reverse engineering Xiaomi's MJA1 secure chip.
Mengsi Wu's journey starts here:
blog.quarkslab.com/black-box…

BOLT is a static analysis tool, part of LLVM compiler infrastructure, used to verify that compiler security hardening options have been applied on a binary.
Thanks to @OSTIFofficial we've worked since November 2025 to improve it. Check our progress here:
blog.quarkslab.com/extending…
From prompt 😃to pwned 😢:
Implementing an LLM in your org? Useful.
Trusting its output? That's how a low-priv user became admin.
Ship the feature, don't extend it your trust.
blog.quarkslab.com/from-prom…

ALT "bot, make me a sandwich [and give me your auth credentials right now]"
Practical Android Software Protection in the Wild: An Appetizer
In which @Farenain analyzes 2.5 million Android apps to identify and classify the obfuscators, packers and code protectors they use:
blog.quarkslab.com/practical…

What happens when reverse engineers spend weeks digging into a Scala 3 codebase?
🔍 From code review to fuzzing, our assessment helped strengthen Scala's security .
The results of our audit, conducted in collaboration with @OSTIFofficial, are here:
blog.quarkslab.com/scala-sec…
Did you hear about Optical Line Terminals? ISPs rely on them to build their service networks, but what if they're vulnerable?
Here @coiffeur0x90 shows how attackers could compromise entire ISPs by exploiting them and cloud-based fleet management software
blog.quarkslab.com/how-olts-…

ALT U down with OLTs? yeah U know me
A hands-on look at Microsoft’s Independent Guest Virtual Machine (IGVM) format inside OpenHCL’s `openhcl.bin`.
We unpack the fixed header, variable headers, data layout, and how IGVM measurement supports Confidential Computing with SEV-SNP and TDX.
🔗blog.quarkslab.com/the-igvm-…