Experts in Secure microchip/IC Reverse Engineering - IC security Evaluation - Embedded Data Recovery - Supply Chain Verification - IC Obsolescence Management
Sophia Antipolis
Joined July 2015
- Tweets856
- Following383
- Followers1.7K
- Likes606




I’ll happily sink dozens of hours into atmospheric, story-driven single-player titles like Ghost of Tsushima or endure the high-tension survival horror of Resident Evil. But recently, I realized my favorite game isn't running on a console—it's running on my lab bench. 😎
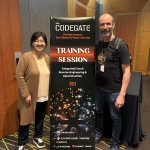
Our IC Reverse Engineering & Data Extraction training at @CODEGATE_KR has just wrapped up in Seoul! 🇰🇷
Three days of learning, hands-on practice and great discussions.
Here are a few highlights from the event 📸
Thank you to everyone who joined us! 🙌


🇰🇷 A first for Texplained—and a new step in our expansion across Asia!
Today, we are kicking off our very first training session in Seoul, hosted at @CODEGATE_KR 2026.
📍 Seoul
🔬 “Integrated Circuit Reverse-Engineering & Data Extraction”
🗓️ 3-day session

Meet Giuseppe👋
He is giving you a quick look at one of ChipJuice's features: the Logical Tracer. In just a few clicks, look how you can follow the logic, explore connections, and move through a circuit more efficiently.
A demo, straight from a person developing this tool😎
Smartphone forensics means analyzing some of the most advanced ICs on the market.
Smaller nodes. Higher density. More complexity. 🔬
This 3 nm GAA sample shows what an aggressive node really means—and why Texplained’s analysis capabilities evolve with technology. 😎
#hardware

After @hardwear_io and @reconmtl, Texplained is heading to Seoul for @CODEGATE_KR 2026 🇰🇷
Olivier THOMAS will deliver a 3-day training on IC Reverse Engineering & Data Extraction, from chip anatomy to ROM/Flash extraction and hardware attacks.
📍 Seoul
📅 July 21–23

🔬 What can a single optical image of a chip reveal?
Much more than just a picture.
This first step helps us size the project, define the analysis strategy, and even spot light sensors protecting the IC against LFI.
#ReverseEngineering #HardwareSecurity #Semiconductors #ICRE

D-4 before our talk at REcon on "FAME".
Meanwhile, day 2 of our Advanced IC Reverse Engineering & Data Extraction training is underway. Great discussions, knowledge sharing, and new connections.
See you in Montreal 🇨🇦
#REcon #ReverseEngineering

Do you remember Pierre?
He shares his journey at Texplained.
From coding algorithms for ChipJuice to discovering chip analysis, one lesson stood out:
"Don't ignore the hardware."
Read his story 👇
texplained.com/from-software…
#ReverseEngineering #HardwareSecurity #Software

Texplained retweeted

Combine this with the fact we can extract schematics and masks of the target IC and you will understand the concept of RE based attacks. Analyze the circuitry, plan a fault you like, go to the laser station, aim at the target and have fun :))

🔬 A new Hardware Attacks room is taking shape at Texplained.
⚡ Laser Fault Injection (LFI)
📡 Electromagnetic Fault Injection (EMFI)
🎯 Microprobing
More details on capabilities, use cases, and behind-the-scenes insights coming soon.
#HardwareSecurity #FaultInjection #ICRE

🔬 A new Hardware Attacks room is taking shape at Texplained.
⚡ Laser Fault Injection (LFI)
📡 Electromagnetic Fault Injection (EMFI)
🎯 Microprobing
More details on capabilities, use cases, and behind-the-scenes insights coming soon.
#HardwareSecurity #FaultInjection #ICRE
2 weeks before @reconmtl starts!
⚡From June 15–18 in Montreal, @reivilo_t will deliver the training “Advanced IC Reverse Engineering & Data Extraction” at REcon 2026.
+ Olivier's Talk on “ROM Dump, Descrambling and Decryption using RE Only: the Fully Analytical MEthod (FAME)”

Wrapping up @hardwear_io training “IC RE: ROM is your primary target”
Interested in analytical ROM extraction techniques? 👇@reivilo_t gives a Talk at @reconmtl (June 20) “ROM Dump, Descrambling and Decryption using RE Only: the Fully Analytical MEthod (FAME), no FIB, no Guesses”

🚀 We’re kicking off at @hardwear_io !
Texplained starts its training: “IC RE: ROM is your primary target”. Until Thu 28th, participants will explore ICs and why ROM is a key entry point for firmware analysis, digital forensics & security research.
Next stops: REcon & Codegate

Florine joined Texplained with a business background — and quickly realized that understanding the technical side of IC Reverse Engineering was key to integrate a team of Hackers. 😎
Follow her journey ⬇️
Texplained retweeted

How do you actually extract data from a chip?
At Hardwear.io USA 2026, this training focuses on ROM often the primary target in transistor-level security analysis and how it can be used as a starting point for integrated circuit reverse engineering.


Texplained is flying to Seoul ✈️
Join Olivier Thomas at @CODEGATE_KR 2026 for a 3-day training on "IC reverse engineering & data extraction".
📍 Seoul
📅 July 21–23, 2026
Ready to set off on your quest?
#HardwareSecurity #reverseengineering #CODEGATE

Attackers don’t always hack systems.
Sometimes they just read what people leave behind. 👀
OSINT turns photos, metadata, weak passwords & oversharing into access.
In hardware security, silence is part of defense.
Here are the basics too many still forget ↓
#OSINT #CyberSecurity
One month to go before @hardwear_io
Secure your seat for @reivilo_t 's training:
“IC Reverse Engineering: ROM is your primary target”
📅 Dates: 26–30 May 2026
📍 Location: Santa Clara Marriott, USA
➡️ hardwear.io/integrated-circu…

Interview with Olivier THOMAS 👇
⚡ Wild lab moments — including a chlorine leak
🔐 Awkward client stories — when security was “not important”
🧠 Hard-earned lessons — what really matters to start in hardware reverse engineering
Click here to read: texplained.com/oliviers-best…
