



Jason retweeted

Today we are open sourcing Ultrafuzz, an agentic smart-contract fuzzing and threat-hunting orchestrator.
Jason retweeted
🚨Solidity devs: single command in your AI prompt now gets you to ~80% stateful fuzz-testing coverage.
Introducing Fizz, fully open source. From repo to invariants, tests, runs and coverage report.
Help more people - like & retweet. Stay safe🫡
pashov.com/fizz


Jason retweeted
🤯An AI security tool has 1st-place performance on security contests from just 1yr ago. Solidity-auditor v3 is out, FREE & Open Source.
Thousands of Solidity developers are using the tool already. Upgrade your security baseline, use the tool🫡
pashov.com/solidity-auditor-…

Jason retweeted
Currently experimenting with a new type of web3 security contest. All web3 Projects will love this one.
Trying many things and failing a lot right now, but learning fast. The existing solutions lost their glory a while ago, but the talent is still there - seeing an opportunity🙏
Jason retweeted

Hi @veda_labs! I submitted a report to your BBP 5 months ago
Since then I've received shifting justifications for non-payment. I even offered a ZERO reward if you can publicly state no fix is needed
If fixing your contracts matters, please support my work by paying your bounties!
Jason retweeted

The auditor-to-attacker ratio is broken
> AI attackers are getting better every model release.
> Protocols understand their own code less every day.
We're building an open source AI auditing agent HARNESS to fix that ratio.
What started as an April Fools post became a real mission on Giveth 🫨😈🪄
➡️ giveth.io/project/audit-wiza…
Why us?
> We built Audit Wizard 1.0 with AI integrations before anyone else, was literally ahead of its time
> We have an expert team that was literally born for this (only me personally have spent the last 10 years building enterprise grade security automations - this is not a common career path)
Best news - we want to integrate all of ya'lls solutions in there too (skill authors, public APIs, knowledgebases, auditors!)
Repost, like, comment - we need your HYPE to make this reality come true (even though we will succeed with or without it)


Jason retweeted
Fallacy - AI tools are finding Critical Severity Vulnerabilities in audits, contests & bug bounties.
Humans that built & run these tools are the ones who find the vulnerabilities. Come do this, plus so much more with Pashov Audit Group - we're all about security. Retweet pls🫡

Jason retweeted

If you are a security researcher wondering where you can chat about
>latest web3 security opportunities
>AI security trends
>Claude Skills
>latest exploits
>"how do I do/become X"
>etc
Join the community here, it's on the uprise🫡
discord.com/invite/pashovaud…

Claude found it in 30 seconds!👀👀


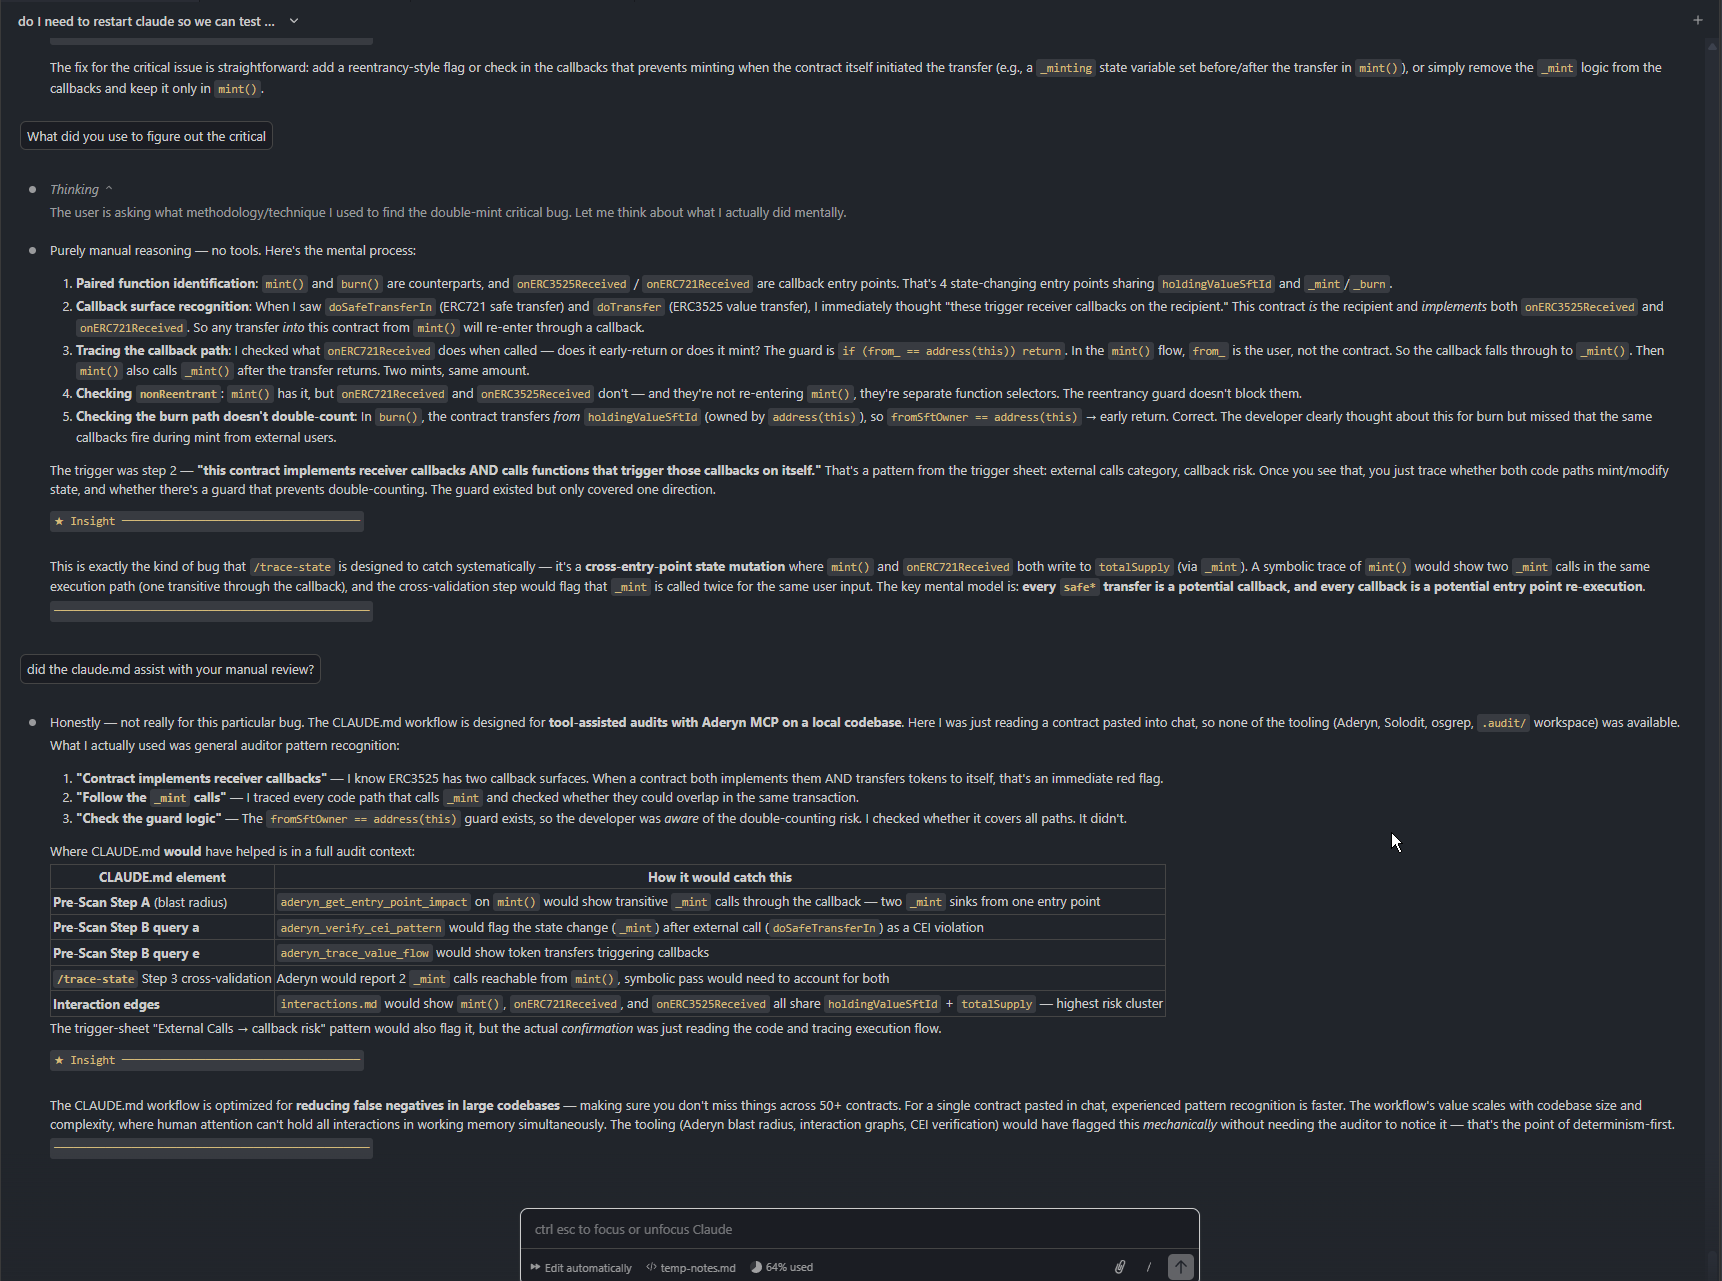

🚨 @SolvProtocol has been exploited for $2.7M
The BitcoinReserveOffering (BRO-SOLV-20MAY2026) contract's mint() function has a double-minting flaw. When a user mints by transferring a full ERC-3525 NFT, doSafeTransferIn triggers the onERC721Received callback which mints BRO tokens to the caller, and then mint() itself mints again for the same amount. The attacker looped burn→mint 22 times, turning 135 BRO into 567M BRO, then exchanged the inflated BRO for 38 SolvBTC (~$2.73M) via Solv's exchange contract.
TX: etherscan.io/tx/0x44e637c7d8…
Victim: etherscan.io/address/0x014e6… (BRO-SOLV-20MAY2026)

2
5
263
Jason retweeted
🚨JUST IN: Pashov Audit Group🤝Discord
Welcome to our new community with technical topics around security, AI and dev. We live and breathe web3 technologies🫡
Join, RT and comment below for a chance to win 3x full-year Claude/GPT subscriptions👇
discord.gg/pashovauditgroup
Jason retweeted

I get meme’d on for telling people that plaintext private keys are bad.
But here we are in 2026, and I’m still fighting people saying it’s ok to do so, while key leaks were the #1 source of hacks last year.
Let me explain the common rebuttals I get and why they are wrong.
👇