


Neptune retweeted

If your Ledger didn’t come from ledger.com, check the exact seller on your order. Tampered units with hidden implants have been resold, capturing the recovery phrase at setup. A passing Genuine Check doesn’t rule it out.
How it works and what to do are in the brief below.

Neptune retweeted
Nine wallets were drained of $2.96 million on a DeFi protocol’s real web address, but nobody had mistyped a thing.
In this particular case attackers took control of the protocol’s DNS and pointed the genuine domain address at a phishing site. Anyone who visited, even from a bookmark, was asked to sign what looked like a routine transaction that handed over their funds. Wallets were drained even after the protocol had already posted a warning to their users on their socials.
When we analyzed the malicious code and traced the money, every theft ran through the same Drainer As a Service (DaaS). That fingerprint led us to four more victims of the same operator, from separate attacks that had nothing to do with this one.
In this case a socially engineered domain provider was the weak link. If someone took your domain today how would you prevent loss?

Neptune retweeted

Several clients have sent me this post asking whether AI has made online anonymity impossible. The research is worth understanding, but the headline leaves out crucial details about who the researchers tested and what they actually demonstrated. A short thread: 🧵

Neptune retweeted
The Coldcard hack is now $88.6M across three waves, and a lot of people believe the entropy bug was "fixed in 2022."
It wasn't. Here is what was actually fixed, when, and why wave 1 took the easy targets.
Infrastructure is only part of the equation.
Attackers don't just target systems. They target the people connected to them.

Today we're launching Reaper. Your company can be doing everything right, SSO, MFA, endpoint protection, security training, and still have your employees' names sitting on the dark web next to old passwords, phone numbers and home addresses. Reaper shows you that exposure before someone uses it.
1
66



Neptune retweeted
Friendly reminder that audits don't catch everything.
Cetus had three. Ronin had been audited. Bybit's Safe contracts were fine. Combined losses still cleared $1.6 B.
An audit tells you what your code looked like on the day someone read it. Everything that happened after is on you.
You don't know what you don't know.

Neptune retweeted

Given the recent TanStack-related supply chain compromise activity, I put together a read-only detection script to help identify currently known indicators of compromise and suspicious artifacts tied to the “Mini Shai-Hulud” npm worm activity.
The script performs local IOC checks against lockfiles, node_modules, GitHub Actions workflows, known dropper filenames, malicious package versions, credential staging artifacts, and related persistence indicators. No network calls are made.
If your environment uses affected TanStack packages, would strongly recommend running it to verify you are clean and review findings manually.
github.com/GLPMC/Tanstack-Wo…


‼️🚨 BREAKING: A new npm supply-chain attack uses a dead-man's switch. The payload plants a watcher on your machine that nukes your home directory the second you revoke the GitHub token it stole from you.
The compromise happened today, across 42 official tanstack npm packages, 84 malicious versions in total. tanstack/react-router alone pulls more than 12 million weekly downloads.
The attacker forked TanStack's repository and pushed a single hidden commit. From there, they tricked TanStack's own release system into signing the malicious packages as if they were the real thing. To npm, and to anyone checking the cryptographic proof of origin (SLSA provenance), the poisoned versions looked 100% legitimate.
Maintainer Tanner Linsley confirmed the whole team had 2FA enabled. It didn't matter. This is the first documented npm worm in history that ships with a valid, signed certificate of authenticity, the same one defenders rely on to know a package wasn't tampered with.

Neptune retweeted

Had an interview with a “crypto” recruiter. We talked for about 40 minutes, and then they asked me to look at some code.
Their first instruction was to clone the repo. I didn’t. They seemed surprised, so I told them I wanted a moment to check whether it was safe first.
I ran a quick analysis with Claude.
Turns out the code had a backdoor. It would copy my environment variables and send them to a remote server.
The recruiter went speechless and ended the call pretty quickly.
Be careful who you talk to. Scammers are real.
Neptune retweeted
100,000 North Korean operatives. Deepfake video interviews. AI-generated identities. Stealing millions in IP and crypto while funding nuclear weapons.
The hiring process is broken. Companies are unknowingly employing state-sponsored hackers. FBI confirms: $600 million+ siphoned to the regime annually.
Your next hire might be working from Pyongyang
Neptune retweeted
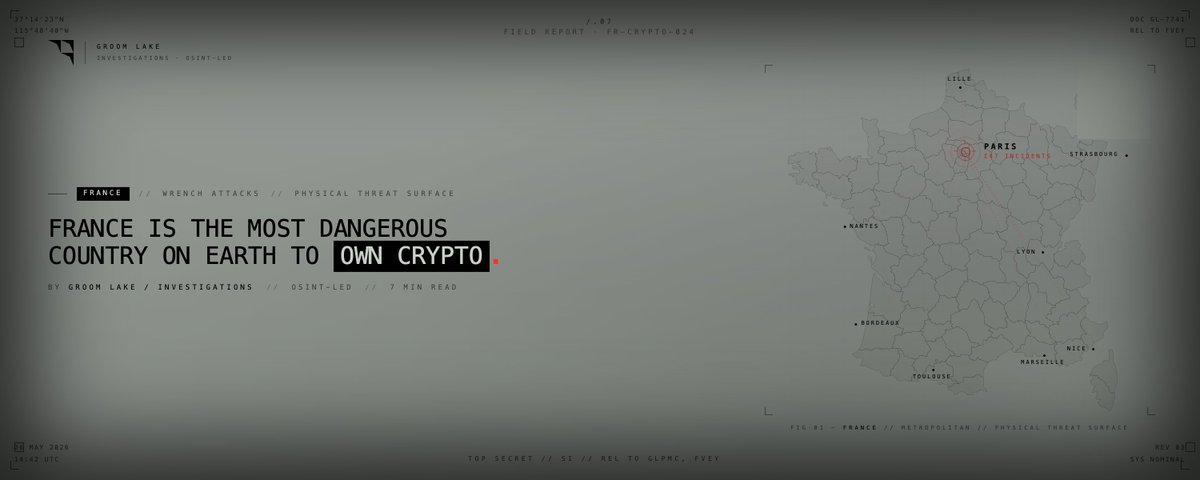
Wrench attacks are still climbing in 2026 and they have nothing to do with your keys.
Criminals skip the technical side entirely and go straight for the person, with threats, coercion, physical force until you hand over access yourself. Analysts found roughly 45% of reported attack frequency tracks directly with market cap, so as prices rise, so does the violence.
Reduce your exposure: keep your public identity separate from your holdings, split day-to-day funds from long-term storage, and audit what's out there with your name attached to it.
Neptune retweeted

Following the recent DNS hijacking incident, the Neutrl domain has been successfully migrated to neutrl.finance and is now secured on a new DNS provider.
Neutrl smart contracts have been unpaused and are fully operational.
ALL USER FUNDS ARE SAFE.
Protocol NAV, including reserves and user funds, remains secure within Neutrl’s custodial wallets, supported by a custody framework and off-exchange settlement (OES) that isolates funds from front-end and infrastructure risks.
Users should no longer interact with neutrl[.]fi under any circumstances and should only use the new domain moving forward. The .fi domain will be sunset.
As an added precaution, users who interacted with the compromised domain are advised to review and revoke permissions via revoke[.]cash, including any Permit2 approvals associated with the following malicious addresses:
0x23f2741EaA0045038e9b52100CdcC890163dE53F
0xa0Adf074056E41dfB892aFC69881E15073b384b9
Please also revoke any approvals associated with addresses you do not recognize.
We extend our sincere gratitude to the teams at @0xGroomLake and @SEAL_911, whose support and expertise were instrumental in our response. Their work in strengthening security across the ecosystem is invaluable.
Additional updates will be shared as they become available, along with a full post-mortem.

Neptune retweeted
Watch how Reaper spiders a digital footprint.
Start with one data point.
Map every connected exposure.

Neptune retweeted
You can’t defend what you can’t see.
Reaper AI continuously maps exposed identities, leaked data, and reconnaissance signals across your organization.
Early access → reaper.groomla.ke/