

Noob/Script kiddie/Smart Contract Security Enthusiast
address(0)
Joined August 2016
- Tweets175
- Following986
- Followers396
- Likes466



Spent a lot of time finally solving the BRIDGE TAKEOVER challenge🥲

I haven't written code for almost half a year. @onlypwner is a great resource to help me with my review. I'm currently stuck on BRIDGE TAKEOVER and need to refresh my knowledge of the EVM.

1
820
I haven't written code for almost half a year. @onlypwner is a great resource to help me with my review. I'm currently stuck on BRIDGE TAKEOVER and need to refresh my knowledge of the EVM.


Obviously, it seems like the dev is saying "Give me your fucking money".

3/ Later, the USDC-WETH pool (0x82cf66e9a45Df1CD3837cF623F7E73C1Ae6DFf1e) was deployed through the factory contract, and the pool’s USDC and WETH has max approval to the Feeto address of the contract factory at initialization, which has an obvious risk of centralization.

1
1,123
too many details🧐, interesting
Detailed analysis of the Yearn Finance @iearnfinance $11M hack.
The root cause is the misconfiguration of yUSDT Token contract. When performing a rebalance to reselect pools, only USDT is used as the add amount, and USDC cannot add to the pool.


1
1,085
Dexible has been exploited, with the core being that attacker can input a token as the router and the routerData constructs a function call of transferFrom(address, address, uint256), a quick read of the code on the phone, there may be some details to overlook
This quoted post is unavailable.
1
4
2,262


The purpose of the contract is unclear, it can make arbitrarily fucntion call, with the only check being user-controllable input. Funds approved to the contract have been stolen
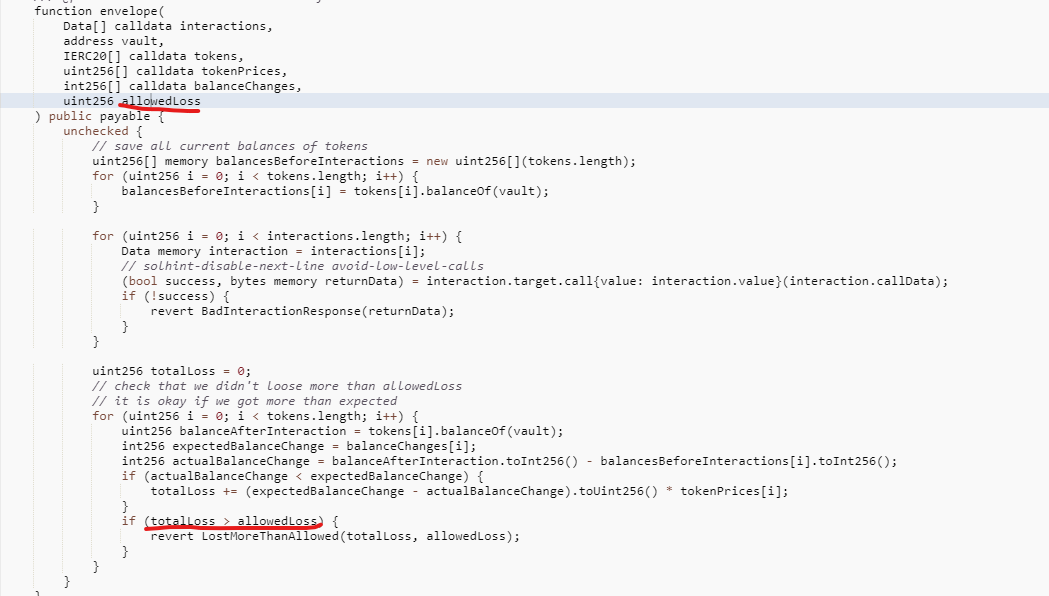

@CoWSwap your funds appear to be moooving away ...
etherscan.io/tx/0x90b468608f…

2
1,272
My friend told me that his USDC was mysteriously transferred, and I looked into it. It seems that the problem came from a vulnerability in the @Polynomial deposit on optimism contract.

Ankr 被黑,私钥泄露?
首先 proxy contract 升级替换 implementation 为攻击者构造的恶意合约
升级 tx:
bscscan.com/tx/0xcbc5ff4a6c9…
恶意新的实现合约里 0x3b3a5522() 函数签名 public 任何人都可以调用获取传入的 aBNBc 数量


以其中一笔攻 tx 为例子:
bscscan.com/tx/0x620344ae2a5…
function selector: 0x3b3a5522
address: 0x66b62446cca33d7eaddd9839d7e65a580bb10b32
amount: 7e37be2022c0914b268 hex-> dec 10000000000000e18
获得:10,000,000,000,000 aBNBc

1
五小时前,@OlympusDAO was exploited?
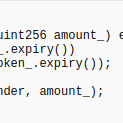
调用redeem() 函数 token 传入攻击者自己部署的地址, 函数内的 expiry() burn()函数都走攻击者恶意构造的逻辑保证正常执行,而 underlying() 返回 OHM 地址进行transfer(),从合约里燃烧空气提取 30,437 OHM,但是目前并没有售出,也许是白帽行为?


nice tips,if the storage key isn't accessed the SSTORE cost should be 22100; if it is accessed , the cost should be 21000

Here we go again!
Can you drain the smart contract?
etherscan.io/address/0x0e1c7…
It's been gas golfed pretty heavily.
#ethereum #solidity #smartcontracts #blockchain
Follow us for more and check us out at RareSkills.io

2
4
Simple poc verification @templedao vulnerability
github.com/Poor4ever/Some-de…

never trust user input.

2/ However, there are several malpractices in how this `migrateStake` function is written.
First of all, anyone can call this, not just the "migrator" contract.
Secondly, anyone can choose the oldStaking, you can just provide an EOA or fake contract and it does not complain!
1
4
Damn Vulnerable Defi Challenge #2 real world version
Flashloan callback function can be called by anyone
Write a POC to revisit this challenge
Attack_tx: bscscan.com/tx/0xd48758ef48d…


ShadowFi 的漏洞
burn() 函数允许任何人调用燃烧任意地址的代币,导致 LP Pair 合约 $SDT代币被恶意消耗完,用小部分 $SDT 代币就可以掏空池子里的 WBNB
POC 验证漏洞:
github.com/Poor4ever/Some-de…
4


