

i to -0 AI and creativity. Alum @southpkcommons, Founder @rumevideo YCS20, prev @hellosign Flips and spins: https://nitter.gq/t.co/odDiZpp54O
San Francisco, CA
Joined May 2009
- Tweets1.6K
- Following938
- Followers491
- Likes3.6K


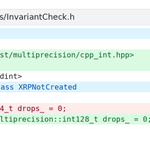
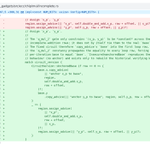




I'm not exactly sure how it will be useful, but something compels me to document some of the recent bugs found, and the code that would have prevented them.
A build configuration mistake in Cold Card routed seed generation through a weak software RNG rather than the better hardware RNG. This made the wallet's private keys predictable to other people running the same software.
github.com/XRPLF/rippled/com…

PHP retained pointers to freed memory between web requests, causing later request to treat attacker-controlled data as trusted internal state including executing malicious code.
github.com/php/php-src/commi…

I have heard so many people daydream about this kind of product. Jason went out and did it. We live in fun times


Who wants to take responsibility for making sure vulnerable code isn’t exploited?
* The harness level launching the code?
* The package manager level building the code?
* The CI level deploying the code?
* The cloud infra level hosting the code?
* The monitoring level of deployed code?
The good news is that now these bugs will all be fixed.
If we do this right, we’ll have growing pains as we plug all of these holes, but then they’ll actually be gone.
And if that’s true. In the long term defense wins


So many online phenomena follow crypto. First we saw the big bugs there, which makes sense, they’re the largest bug bounty in the world.
But now it’s coming for everywhere else. The stuff the Zcash ecosystem is doing now is what we’ll all be doing in a few months

🚨 Nightmare day for cybersecurity
Multiple major security incidents, active exploits, supply chain compromises...
If you run production systems, start patching NOW.
PHP: Two critical unauthenticated RCEs. Attackers already exploiting them. Patch NOW
LiteLLM: v1.107.0 on PyPI and Docker is BACKDOORED. Steals cloud, SSH, and AI credentials. Pin 1.106.2. Rotate secrets.
eMudhra: A certificate authority's keys were crackable. Update your browsers, systems, and trust stores.
Node.js / Next.js / React: Security releases for Brotli RCE, TLS bypasses, and TWO critical Next.js RCEs.
TiDB Cloud: PingCAP breached through stolen credentials. Customer information and other sensitive data exfiltrated. Read the attacker's release, fun stuff.
Plex2Shell: Weaponized within HOURS of the PoC. Attackers already deploying cryptominers and proxy backdoors.
BeyondTrust / Ivanti: Actively exploited zero-days added to CISA's KEV catalog. BeyondTrust attacks linked to a China-nexus campaign.
And that's not even the full list.
Patch. Audit. Rotate. NOW.
I got shielded Zcash working on a Trezor Safe 7 and sent real mainnet transactions back and forth to prove it.
In a world where AI is writing all the code, how can we build trust in code that no one will ever read?
Zcash code takes a lot of space on the device, and not every Trezor user wants it. Trezor is currently building an app-extension SDK for this.
I forked that dev branch and filled in the missing pieces to get the demo running.
Firmware: github.com/bawolf/trezor-fir…
Suite's license made me hesitant to publish my desktop changes without permission. @Trezor, if you're open to it I'd love to share them, and to help however is useful.


Whether or not you think AI has a role in art output, it's so empowering for the creative process. How many interesting things wouldn't exist without a language model nudging us toward creation. Which led to a human illustrator finishing the work!
frogandtoad.ai/about
