

bar lanyado retweeted

Excited to finally share my recent research, where I managed to hack Chrome, Comet, Edge, Opera and Claude in Chrome using one single browser extension
2 CVEs & $20,000 in bounties 🙂
Introducing - BragJack!
forever.security/blog/bragja…

bar lanyado retweeted

"The Browser giveth and the AI Browser taketh away"
Decades of hard work went to establish boundaries between different websites within the same browser (SOP, CORS), now become obsolete when it is commandeered by AI (e.g. @perplexity_ai Comet browser or browser based AI agents)

bar lanyado retweeted

GenAI apps powered by #MCP are fast, modular, and vulnerable🚨
@DrorOphir & @BLanyado reveal the top 10 security risks, real-world exploits & how to defend against them 👇
eu1.hubs.ly/H0lKGpv0
#GenAI #CyberSecurity #AIsecurity #LLM #Lasso

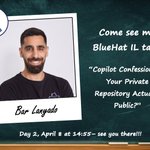
I am thrilled to share that I will be speaking at the Microsoft @BlueHatIL 2025 alongside the incredible @DrorOphir
In our talk, we’ll unveil our latest research on how we discovered private repositories exposed on Microsoft Copilot.
See you there! 🔥

bar lanyado retweeted
🚨 Breaking: @BLanyado Lasso's security research has uncovered a critical vulnerability with sensitive private repositories in Microsoft Copilot via Bing Cache from major enterprises, including @IBM @OpenAI @googlecloud @PayPal and @Microsoft itself!
eu1.hubs.ly/H0h4swl0

bar lanyado retweeted

🫠 GitHub repositories that were once exposed are still accessible via Copilot despite being made private.
The ongoing reach of AI tools into past data raises serious privacy and security concerns.
techcrunch.com/2025/02/26/th…
bar lanyado retweeted
We are proud to announce that @LassoSecurity has been named a @Gartner_inc #CoolVendor in the October, 2024 Cool Vendors™️ for AI Security report 🤠
Download now >> lasso.security/analysts-repo…

bar lanyado retweeted
Lassos’s research by @BLanyado has been mentioned in @Gartner_inc’s recent Threat Landscape Report 📢
Read the learn all about how he found +15000 #HuggingFace exposed tokens: lasso.security/blog/1500-hug…
bar lanyado retweeted
חולשה ב-ChatGPT הפילה בפח את המפתחים של עליבאבא israeldefense.co.il/node/619…
@BLanyado

bar lanyado retweeted
🚨 Research alert
Read @BLanyado follow-up research that dives deeper into AI Package Hallucination.
Did #GPT4 #GEMINI #COHERE closed the security gaps? spoiler alert-no, is the attack effective in the wild? well- yes.
For the full article➡️lasso.security/blog/ai-packa…
🚨 Research alert
I just published my new research regarding LLM hallucinations.
This time I asked A LOT more questions and investigated more models. I also found Hallucinated package in the wild with over 30K downloads of a hallucinated package lasso.security/blog/ai-packa…
bar lanyado retweeted
Spotlight on @BLanyado and his talk: Spreading Malicious Packages Using Generative AI!
youtu.be/8tlU3APgHBE
#BSidesBerlin

bar lanyado retweeted

🚨Research Alert! Some npm package maintainers opt for deprecation instead of addressing security flaws. We found that 8.2% of top 50K packages are deprecated, but it's likely much higher at 21.2% due to inconsistent practices. blog.aquasec.com/deceptive-d… @AquaSecTeam @GoldmanIlay

bar lanyado retweeted
Our very own @BLanyado took the stage at @SidesBer to share groundbreaking insights on #LLM security and AI Package Hallucination.
Missed the live session? No worries! Catch the recording now and dive into the wealth of knowledge shared >> eu1.hubs.ly/H06_LDF0
Research Alert!🚨 My research for exposed HuggingFace API tokens revealed 1,681 valid API tokens, some with full access to popular models like Meta-Llama, Pythia, and Bloom. This exposes millions to potential supply chain attacks.
More Details on my blog: lasso.security/blog/1500-hug…

bar lanyado retweeted
No matter who's OpenAI's CEO (no worries we still love you @sama), we got your back with an AWESOME security tool for your organization's GenAI tools. Check it out>> lasso.security


bar lanyado retweeted
🚨 New Research Alert! Exposed #Kubernetes secrets pose a significant risk, impacting top blockchain & Fortune 500 companies. Most secret scanners miss these exposures. Learn more about our findings & how to protect your data ➡️ blog.aquasec.com/the-ticking… #CyberSecurity

I am thrilled to share that I will present my latest research, "AI Package Hallucination", at Bsides Singapore this Friday!
This is a new attack technique that uses GenAI tools such as ChatGPT to spread malicious packages.
for more details: bsidessg.org/schedule/ai-pac…
#BsidesSG

bar lanyado retweeted
📈⛓ RepoJacking is on the rise, making it crucial to identify vulnerable repos
@GoldmanIlay and I uncover a key data mine used by attackers to find these🎯
In this blog we demonstrate code execution in an actual repos and suggest mitigation: lnkd.in/dNWzFH-K
@AquaSecTeam
I want to share my latest discovery,
a new technique we have named “AI package hallucination”.
In this research, we have found that around 30% of coding queries to ChatGPT could be used by attackers to spread malicious packages.
@VulcanCyber
vulcan.io/blog/ai-hallucinat…