

┃ CCDH Watch ┃ Exposing CCDH. Following the Money. Stopping the Reset. They Counter "Hate." We Counter Their Control.
Joined January 2025
- Tweets11.2K
- Following919
- Followers5.2K
- Likes20.6K




Pinned Tweet
🟨My focus is entirely on objective network mapping and financial transparency, completely independent of partisan or ideological loyalties. As a non-aligned observer, my work consists of identifying and tracing funding structures across the entire political spectrum, without fear or favour.
🟨Pointing out the financial architecture and institutional backing behind any political actor is not an act of partisanship—it is a standard requirement for public accountability. Attempting to frame a factual disclosure of funding sources as an ideological defence of an opponent is a transparent deflection tactic designed to evade scrutiny. Facts do not hold political allegiances, and documenting who funds a campaign remains a matter of public record, regardless of who it makes uncomfortable.

CCDHWatch retweeted
THE UNLIKELY ALIGNMENT AND THE FINAL VERDICT
The exposure of Neville Roy Singham created a convergence where Western national security agencies, Israeli intelligence analysts, and liberal philanthropic institutions aligned against a single dark-money operator.
🔴1. THE SOROS ANTI-CCP POSITIONING
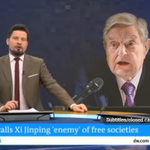
While critics often attempt to conflate liberal philanthropists with radical dark-money networks, George Soros and Open Society Foundations (OSF) take an explicitly hostile stance toward the Chinese state. In his seminal address at the 2019 World Economic Forum in Davos, Soros declared:
"Chinese President Xi Jinping is the most dangerous enemy of open societies... The social credit system will subordinate the fate of the individual to the interests of the one-party state in ways unprecedented in history."
georgesoros.com/2019/01/24/r…
Because Singham's Shanghai-based network operated through major non-profit clearinghouses like the Tides Foundation, mainstream liberal foundations faced severe regulatory and reputational risk, prompting silent distancing and cooperation with compliance audits.
🔴2. THE ULTIMATE TRIGGER: ADVOCACY VS. INFRASTRUCTURE SABOTAGE
The evidence resolves the core question of why Singham was targeted for dismantling at this precise moment:
◾️- Propaganda Alone Was Tolerated: For years, Singham funded media platforms and academic think tanks pushing Beijing-aligned narratives under the protection of Western free speech and non-profit donor privacy.
◾️- Infrastructure Sabotage Triggered Destruction: The line was crossed when his network shifted to kinetic and economic sabotage against critical defense assets—targeting Palantir AI platforms, Project Nimbus cloud architecture, Elbit defense supply chains, and domestic US data centers ($23.6 billion in blocked development).
🔴3. FORENSIC CONCLUSION
When a dark-money network transitions from political advocacy to targeting sovereign cloud capabilities and military artificial intelligence, it ceases to be treated as political speech and is classified as an asymmetric national security threat. The federal grand jury probes, FARA enforcement actions, and tax exemption reviews currently unfolding mark the definitive end of Singham's dark-money laundromat and he is marked as an enemy of the (deep) state and friend of the CCP.
Thanks for reading this one... 🧵

CCDHWatch retweeted

This Monday, @BylineTimes posted an article about us with the misleading headline “Mysterious Right-Wing Think Tank Demanding Charity Transparency
Won't Say Who Runs or
Funds It.” We very explicitly responded to their reporter’s Right of Reply with the factually correct statement that we do not disclose any funders because we have none.
We wrote to them requesting the headline be changed and a correction publicised. Unfortunately they have not responded. We urge Byline to correct their false headline with immediate effect and publicise said correction, lest we are forced to escalate the complaint to their regulator, Impress.
The Cambridge Circus Research Team

CCDHWatch retweeted
PROJECT NIMBUS - PALANTIR - NATO & THE DISMANTLING OF THE SINGHAM (ENEMY OF THE DEEP STATE) NETWORK🔥🔥🔥🔥🧵
In a coordinated forensic operation spanning Jerusalem, Washington, New Delhi, and London, a global intelligence and open-source coalition uncovered a $278 million dark-money apparatus operating directly out of Shanghai. At the centre of this network is American technology mogul Neville Roy Singham, whose non-profit infrastructure has been exposed for executing asymmetric foreign influence operations inside Western democracies.
While public scrutiny initially focused on ideological propaganda, intelligence dossiers compiled by Israeli defense bodies, US congressional committees, and federal prosecutors reveal a far more critical objective: the systematic targeting and disruption of Western artificial intelligence infrastructure and sovereign cloud capabilities, specifically targeting Palantir Technologies and the $1.2 billion US-Israeli cloud framework, Project Nimbus.
This expanded investigation unmasks the structural realities, financial conduits, legal clashes, and intelligence operations across five core pillars:
🔴1. THE SHANGHAI CAPITAL PIPELINE: The transition of software capital from Thoughtworks into Shanghai-based corporate fronts, co-located with state propaganda bodies and Maoist ideologues.
🔴2. THE TAX-EXEMPT LAUNDROMAT: How donor-advised funds, the Tides Foundation, and pass-through non-profits moved over $270 million to fund militant street cadres and anti-infrastructure campaigns.
🔴3. THE GLOBAL PROXY MAP: Subversive operations across India (NewsClick), South Africa (NUMSA/New Frame), Zambia (Socialist Party), and Europe (No Cold War, Samidoun).
🔴4. THE ISRAELI TECH COLLISION: How Israeli intelligence analysts (INSS, NCRI, NGO Monitor, Cyabra) exposed the network's targeting of military AI, leading to an alignment between Western security organs, Israeli state intelligence, and liberal philanthropic anti-CCP figures.
🔴5. CRIMINAL ESCALATION AND SUBPOENA BATTLES: The Southern District of New York (SDNY) federal grand jury criminal probe into wire fraud and FARA violations, alongside the August 2026 refusal by 21 subpoenaed network figures to comply with congressional oversight under First Amendment claims.
The ultimate question is no longer how the Singham network operated, but why it was targeted for systematic destruction at this precise historical juncture?
@DataRepublican @pepesgrandma
waysandmeans.house.gov/2026/…
CCDHWatch retweeted
THE ISRAELI INTELLIGENCE UNMASKING & OSINT FORENSICS
The systematic exposure of the Singham apparatus was executed by a specialized coalition of Israeli defense think tanks, threat-intelligence firms, and forensic OSINT analysts who mapped the network's cross-border financial, cyber, and physical footprint.
🔴1. THE INSS DEFENSE ASSESSMENT
The Institute for National Security Studies (INSS) in Tel Aviv published a landmark intelligence assessment titled "A Chinese Influence Campaign Against Israel as a Means of Harming the United States." The report established that Singham's Shanghai hub was using pro-Palestinian and anti-tech campaigns as an asymmetric lever to erode US-Israeli defense cooperation and disrupt Western technological infrastructure.
🔴2. NCRI FORENSICS AND "THE DISSENT FACTORY"
The Network Contagion Research Institute (NCRI), working alongside Israeli data scientists, published "The Dissent Factory." By auditing digital document metadata, NCRI discovered that Singham's think tank, Tricontinental, had formed a direct operational publishing partnership with House of Latin America (HOLA), an Iranian state-linked entity connected to the IRGC Student Basij. Metadata across Persian publications named Chicago-based HOLA director Ali Abutalebi, while donation channels directed funds to U.S.-sanctioned Bank Refah Kargaran.
networkcontagion.us/reports/…
🔴3. NGO MONITOR AND CYBER THREAT INTEL
◾️- NGO Monitor (Jerusalem) (Soros funded): Audited tax-exempt shell conduits (PSF, UCF, JEF), exposing how Singham's US non-profits co-hosted operations with Samidoun, officially designated by Israel as a front for the Popular Front for the Liberation of Palestine (PFLP).
◾️- Cyabra and FakeReporter: Israeli cyber-threat intelligence firms mapped Coordinated Inauthentic Behavior (CIB) across social media, proving that digital amplification targeting Project Nimbus and Palantir was synchronised with physical blockades organised on the ground.
◾️- Shomrim: Israeli investigative outlet cross-referenced Chinese corporate registries (Maku Group, Shanghai Luoweixing) with US non-profit disclosures to establish origin-of-funding trails.
ngo-monitor.org/
🔴4. THE UNOFFICIAL TECH EMBARGO ASSESSMENT
Israeli intelligence and cyber security analysts tracked these actions as an "unofficial technological embargo." By attempting to sever cloud computing access and military AI software integration during active security crises, the Singham network functioned as an operational threat to real-time defense readiness.
networkcontagion.us/reports/…


PROJECT NIMBUS - PALANTIR - NATO & THE DISMANTLING OF THE SINGHAM (ENEMY OF THE DEEP STATE) NETWORK🔥🔥🔥🔥🧵
In a coordinated forensic operation spanning Jerusalem, Washington, New Delhi, and London, a global intelligence and open-source coalition uncovered a $278 million dark-money apparatus operating directly out of Shanghai. At the centre of this network is American technology mogul Neville Roy Singham, whose non-profit infrastructure has been exposed for executing asymmetric foreign influence operations inside Western democracies.
While public scrutiny initially focused on ideological propaganda, intelligence dossiers compiled by Israeli defense bodies, US congressional committees, and federal prosecutors reveal a far more critical objective: the systematic targeting and disruption of Western artificial intelligence infrastructure and sovereign cloud capabilities, specifically targeting Palantir Technologies and the $1.2 billion US-Israeli cloud framework, Project Nimbus.
This expanded investigation unmasks the structural realities, financial conduits, legal clashes, and intelligence operations across five core pillars:
🔴1. THE SHANGHAI CAPITAL PIPELINE: The transition of software capital from Thoughtworks into Shanghai-based corporate fronts, co-located with state propaganda bodies and Maoist ideologues.
🔴2. THE TAX-EXEMPT LAUNDROMAT: How donor-advised funds, the Tides Foundation, and pass-through non-profits moved over $270 million to fund militant street cadres and anti-infrastructure campaigns.
🔴3. THE GLOBAL PROXY MAP: Subversive operations across India (NewsClick), South Africa (NUMSA/New Frame), Zambia (Socialist Party), and Europe (No Cold War, Samidoun).
🔴4. THE ISRAELI TECH COLLISION: How Israeli intelligence analysts (INSS, NCRI, NGO Monitor, Cyabra) exposed the network's targeting of military AI, leading to an alignment between Western security organs, Israeli state intelligence, and liberal philanthropic anti-CCP figures.
🔴5. CRIMINAL ESCALATION AND SUBPOENA BATTLES: The Southern District of New York (SDNY) federal grand jury criminal probe into wire fraud and FARA violations, alongside the August 2026 refusal by 21 subpoenaed network figures to comply with congressional oversight under First Amendment claims.
The ultimate question is no longer how the Singham network operated, but why it was targeted for systematic destruction at this precise historical juncture?
@DataRepublican @pepesgrandma
waysandmeans.house.gov/2026/…
CRIMINAL ESCALATION: SDNY GRAND JURY, SUBPOENA BATTLES, AND CONSTITUTIONAL SHIELDING
In 2026, the investigation escalated from congressional policy oversight to federal criminal prosecution and intense constitutional litigation.
🔴1. THE SDNY FEDERAL GRAND JURY PROBE
A federal grand jury in the Southern District of New York (SDNY) launched a formal criminal investigation into Neville Roy Singham and Jodie Evans. Federal prosecutors are examining potential criminal violations involving:
◾️- Foreign Agents Registration Act (FARA) non-compliance for acting under the direction of foreign principals.
◾️- Wire fraud and bank fraud related to cross-border financial disclosures.
◾️- Tax evasion and money laundering involving the movement of $278 million through donor-advised funds and shell non-profits.
🔴2. CONGRESSIONAL SUBPOENAS AND THE AUGUST 2026 REFUSAL
In July 2026, the House Ways and Means Committee issued formal subpoenas targeting 21 key individuals across The People's Forum, Tricontinental, and BreakThrough News. In August 2026, attorneys representing the subpoenaed non-profits formally rejected the committee's demands, sending refusal letters that characterised the inquiry as a "McCarthy-era witch hunt" and invoking First Amendment protections for speech, research, and association.
🔴3. SYSTEMIC IMPACT ON TAX-EXEMPT LAW
This legal impasse has accelerated bipartisan legislative proposals in Washington aimed at closing foreign dark-money loopholes. Draft legislation seeks to eliminate anonymous donor protections for Donor-Advised Funds (DAFs) and fiscal sponsors that handle overseas capital streams.
foxnews.com/politics/singham…

THE UNLIKELY ALIGNMENT AND THE FINAL VERDICT
The exposure of Neville Roy Singham created a convergence where Western national security agencies, Israeli intelligence analysts, and liberal philanthropic institutions aligned against a single dark-money operator.
🔴1. THE SOROS ANTI-CCP POSITIONING
While critics often attempt to conflate liberal philanthropists with radical dark-money networks, George Soros and Open Society Foundations (OSF) take an explicitly hostile stance toward the Chinese state. In his seminal address at the 2019 World Economic Forum in Davos, Soros declared:
"Chinese President Xi Jinping is the most dangerous enemy of open societies... The social credit system will subordinate the fate of the individual to the interests of the one-party state in ways unprecedented in history."
georgesoros.com/2019/01/24/r…
Because Singham's Shanghai-based network operated through major non-profit clearinghouses like the Tides Foundation, mainstream liberal foundations faced severe regulatory and reputational risk, prompting silent distancing and cooperation with compliance audits.
🔴2. THE ULTIMATE TRIGGER: ADVOCACY VS. INFRASTRUCTURE SABOTAGE
The evidence resolves the core question of why Singham was targeted for dismantling at this precise moment:
◾️- Propaganda Alone Was Tolerated: For years, Singham funded media platforms and academic think tanks pushing Beijing-aligned narratives under the protection of Western free speech and non-profit donor privacy.
◾️- Infrastructure Sabotage Triggered Destruction: The line was crossed when his network shifted to kinetic and economic sabotage against critical defense assets—targeting Palantir AI platforms, Project Nimbus cloud architecture, Elbit defense supply chains, and domestic US data centers ($23.6 billion in blocked development).
🔴3. FORENSIC CONCLUSION
When a dark-money network transitions from political advocacy to targeting sovereign cloud capabilities and military artificial intelligence, it ceases to be treated as political speech and is classified as an asymmetric national security threat. The federal grand jury probes, FARA enforcement actions, and tax exemption reviews currently unfolding mark the definitive end of Singham's dark-money laundromat and he is marked as an enemy of the (deep) state and friend of the CCP.
Thanks for reading this one... 🧵
George Soros stated:
"I want to use my time tonight to warn the world about an unprecedented danger that's threatening the very survival of open societies... Chinese President Xi Jinping is the most dangerous enemy of open societies."
youtu.be/PXGxShCv3nw

CCDHWatch retweeted

I just came across this in an Open Society Foundations document about how to fix public “mistrust” of liberal "democracy," and I honestly feel sick reading it. I've read many alarming quotes, but few are so "mask off" like this.
"I believe the time has come for a responsible, courageous elite, those who care far more about addressing the genuine social problems than about election results. Only a political elite with vision, prudence and a focus on the general good—to whom the electorate… can cede part of their sovereignty in the elections—will be able to justify public trust and spearhead... our struggle to survive.""
Read that again. The proposed solution to the public's distrust in democracy... is less democracy.
An unelected "elite" to whom the public should cede sovereignty.
Abolish democracy to save democracy. This kind of thinking is what we're up against.


CCDHWatch retweeted

CCDH is moving into “online safety” and AI regulation, as evidence by their recent name change (from countering "hate" to "harm.") I’m still waiting for accountability for its “Disinformation Dozen” campaign.
A year ago, YouTube reinstated my channel with this acknowledgment:
“We can confirm that your channel does not violate our Community Guidelines.”
They also apologized for “our mistake.”
That mistake cost me years of work and access to an audience I had spent years building. Restoring a channel doesn’t undo that damage.
Meanwhile, CCDH continues to expand, including into Canada. Those of us targeted are left to pick up the pieces while the organization pursues greater influence over what everyone else can say.
I want people whose speech has been unlawfully suppressed to have a way to fight back in court. That means enforceable First Amendment protections, including a private right of action - not another hearing that ends with no remedy for those harmed.
That’s what we’re working toward. Join us:
restorethe1st.com @restorethe1st

CCDHWatch retweeted
🚨🚨THE DEMOCRACY FILES, PART 2: WHEN AND HOW TO DECLARE THE FEDERAL GOVERNMENT ILLEGITIMATE 🚨
Some questioned whether a group of 200 ex-USAID officials could actually pull off their ambitions to rewrite the Constitution.
Here, they describe exactly how it works. They aren't working alone.
The videos all come from Renew to Thrive (R2T) group and associates. Danielle Reiff and Paul Zeitz play key roles within R2T.
R2T sits inside a much, much larger umbrella called United Democracy Alliance (UDA), which is an extremely hush-hush control plane of leaders from major "blocking" NGOs such as 50501 and Indivisible fulfilling various functions. UDA decides when protests get deployed, timelines, how to respond, all that.
R2T's role within UDA is concerned with "the day after tomorrow" - in other words, their function is to conceive what a rewritten American government will look like after the rest of UDA fulfills its purpose. As will be shown, Erica Chenoworth is credited with conceiving UDA in the first place under the Horizons "Big Tent" initiative.
Note here that National Security Leaders for America (NSL4A) is credited for operationalizing UDA. NSL4A is a group of 1,600 ex-military, intelligence, and diplomatic officials. They are led by Rear Admiral Michael E. Smith (Ret). NSL4A also played a key role in the "illegal orders" messaging which targeted Pete Hegseth. Zeitz is also a member of NSL4A.
It must be emphasized that the choice of a military-oriented organization to coordinate NGOs across domestic protests is an interesting one all in itself - especially in an umbrella conceived by a regime change expert like Chenoworth.
You will have a hard time finding any mentions of UDA in the public. They are extremely hush-hush and selective who they talk to.
Mike Smith himself makes a personal appearance in other calls, coordinating Insurrection Act exercises and roleplaying with R2G as one of the participants.
As the audio transcript shows, they have outlined a sequence of "redlines" in which case the federal government should be declared illegitimate. Invoking the Insurrection Act against "peaceful" protesters is one of the most discussed redlines. I will post the illegitimate criteria below, but basically, almost any effective pushback against NGOs is a measure of illegitimacy according to them.
Important to understand:
The audio shows they shopped this idea around governors, but the reality is that governors do not have to explicitly sign on to the pact to play their role in the coup. All they have to do is refuse troops in their state and let UDA / R2G do the work of dissolving the federal government.
CCDHWatch retweeted

This is not even real… a group of retired admirals, ex-USAID bureaucrats and professional protest organizers got caught on their own recordings working out the conditions under which they get to declare the government of the United States illegitimate, and somehow we are supposed to believe they are the ones protecting democracy.
Here is what @DataRepublican put out in Part 2 of the Democracy Files. The videos come from a group called Renew to Thrive, with Danielle Reiff and Paul Zeitz in key roles, and it sits inside a much bigger umbrella called the United Democracy Alliance, which she describes as the hush-hush control room for groups like 50501 and Indivisible, deciding when protests get deployed, the timelines and how to respond. National Security Leaders for America, 1,600 former military, intelligence and diplomatic officials led by retired Rear Admiral Michael E. Smith, is credited with operationalizing the whole thing. On tape they lay out a list of "redlines," and invoking the Insurrection Act against "peaceful" protesters is one of the most discussed… and as she lays it out, they shopped the idea around to governors who don't even have to sign anything, all a governor has to do is refuse federal troops and let the network do the rest.
Make no mistake about who Mike Smith is. His own organization's bio says he founded and led National Security Leaders for Biden, more than 1,100 members with an endorsement letter signed by 780 of them, and now he runs a "non partisan" group that just cares so deeply about the oath. But hey… I am sure it is totally nonpartisan this time.
And the very same morning the Washington Post runs a story about a small group of current and former Defense Department officials quietly advising governors, election officials and lawmakers in 10 states on how to prepare for the Trump administration "interfering" in the midterms, rehearsing what to do if a federal agent asks for access to ballots or machines. Different names, same message… the elected federal government is the threat, and the people who run the elections are the ones who need protecting from it.
Let me put it to you like this. They are building the excuse before the event even happens. They coordinate the protests, they decide in advance which government response crosses their line, and then they hold that response up as proof the whole government is illegitimate and the governors should take over. How exactly is that defending the Constitution? If a room full of retired conservative officers got caught on tape role playing how to declare a Democrat president illegitimate, the FBI would be knocking on doors before the coffee got cold and every network in the country would run it wall to wall.
I am angry about this, and I think most of you are not angry enough. These people swore an oath to the Constitution, not to a party, and they are treating the legitimacy of an elected government like a privilege they get to revoke the minute the voters pick somebody they don't like. As DataRepublican puts it, almost any effective pushback against their NGOs counts as illegitimate in their book. Where is the outrage from the people who spent five years lecturing you about threats to democracy?
Admiral Smith, Ms. Reiff, Dr. Zeitz… release every recording in full and explain to the American people, under oath, exactly what you were planning for the day after.


🚨🚨THE DEMOCRACY FILES, PART 2: WHEN AND HOW TO DECLARE THE FEDERAL GOVERNMENT ILLEGITIMATE 🚨
Some questioned whether a group of 200 ex-USAID officials could actually pull off their ambitions to rewrite the Constitution.
Here, they describe exactly how it works. They aren't working alone.
The videos all come from Renew to Thrive (R2T) group and associates. Danielle Reiff and Paul Zeitz play key roles within R2T.
R2T sits inside a much, much larger umbrella called United Democracy Alliance (UDA), which is an extremely hush-hush control plane of leaders from major "blocking" NGOs such as 50501 and Indivisible fulfilling various functions. UDA decides when protests get deployed, timelines, how to respond, all that.
R2T's role within UDA is concerned with "the day after tomorrow" - in other words, their function is to conceive what a rewritten American government will look like after the rest of UDA fulfills its purpose. As will be shown, Erica Chenoworth is credited with conceiving UDA in the first place under the Horizons "Big Tent" initiative.
Note here that National Security Leaders for America (NSL4A) is credited for operationalizing UDA. NSL4A is a group of 1,600 ex-military, intelligence, and diplomatic officials. They are led by Rear Admiral Michael E. Smith (Ret). NSL4A also played a key role in the "illegal orders" messaging which targeted Pete Hegseth. Zeitz is also a member of NSL4A.
It must be emphasized that the choice of a military-oriented organization to coordinate NGOs across domestic protests is an interesting one all in itself - especially in an umbrella conceived by a regime change expert like Chenoworth.
You will have a hard time finding any mentions of UDA in the public. They are extremely hush-hush and selective who they talk to.
Mike Smith himself makes a personal appearance in other calls, coordinating Insurrection Act exercises and roleplaying with R2G as one of the participants.
As the audio transcript shows, they have outlined a sequence of "redlines" in which case the federal government should be declared illegitimate. Invoking the Insurrection Act against "peaceful" protesters is one of the most discussed redlines. I will post the illegitimate criteria below, but basically, almost any effective pushback against NGOs is a measure of illegitimacy according to them.
Important to understand:
The audio shows they shopped this idea around governors, but the reality is that governors do not have to explicitly sign on to the pact to play their role in the coup. All they have to do is refuse troops in their state and let UDA / R2G do the work of dissolving the federal government.
CCDHWatch retweeted

Ah yes, Abbie Jitendra of Joseph Rowntree Foundation and LSE etc etc... Institutions well known for delivering us loud-mouthed twits. She suddenly wants privacy 🙄 @CCDHWatch
m.youtube.com/watch?v=Lmgepp…

Where the Tabatznik / Bertha Foundation money came from during apartheid in South Africa.

THE TABATZNIK DYNASTY: FROM APARTHEID-ERA PROFITEERING TO PROGRESSIVE DOCUMENTARY PHILANTHROPY
Where did the money come from?
A forensic investigation into the historical origins of the Tabatznik family wealth—tracing the arc from David Tabatznik’s corporate role in Apartheid South Africa’s private psychiatric prison system to the family’s global pharmaceutical expansion and modern philanthropic vehicles like the IDFA Bertha Fund.
🔴1. THE APARTHEID INDUSTRIAL COMPLEX: SMITH MITCHELL & CO
The foundational capital of the Tabatznik network traces back to David Tabatznik (father of Tony Tabatznik) in mid-20th century South Africa.
🔹 SMITH MITCHELL & CO: David Tabatznik served as a leading executive and chairman of Smith Mitchell and Co, a management company that operated private, segregated psychiatric institutions and labor camps under Apartheid law.
🔹 THE CONNIE MULDER CONNECTION: Smith Mitchell operated in direct financial partnership with Apartheid cabinet minister Connie Mulder (Minister of Information and Native Affairs). Mulder and Tabatznik served together as co-directors of corporate entities controlling these institutions (such as the Randfontein Non-European Hospital).
🔹 THE PROFIT MODEL: Smith Mitchell facilities housed tens of thousands of Black South Africans under state contracts. When questioned regarding the commercial extraction from state-confined populations, David Tabatznik famously stated: “Of course we make a profit, or we wouldn't be doing it”.
🔹 THE MULDERGATE SCANDAL: The political-financial network unraveled in the late 1970s following the "Muldergate" scandal (Information Scandal), which exposed secret state slush funds, covert influence operations, and commercial self-dealing between government ministers and corporate directors.
🔴2. TRANSNATIONAL PHARMACEUTICAL & OFFSHORE STRUCTURES
Following the scrutiny surrounding Apartheid-era government contracts, the family’s capital was transitioned into international generic pharmaceuticals and offshore holding structures.
🔹 ALPHAPHARM & ARROW GROUP: The family built global pharmaceutical assets through Alphapharm in Australia (which faced government pricing inquiries in the late 1980s) and subsequently the Arrow Group (Arrow Pharmaceuticals), specializing in generic drug supply deals and international distribution chains.
🔹 COMMERCIAL EXIT: In 2009, the sale of Arrow Generics to US-based Watson Pharmaceuticals generated $1.75 billion, creating the liquid capital pool that funded modern family trusts and foundations.
🔹 OFFSHORE HOLDING VEHICLES: Corporate registries and investigative databases trace the family’s international holding structures through offshore jurisdictions, including Scarlett Holdings (Panama), Quiver Inc (BVI), and London Trust (BVI) and others as mentioned earlier.
🔴3. RE-BRANDING THROUGH PHILANTHROPY: BERTHA FOUNDATION & IDFA
The capital extracted from Apartheid-era state contracts and global pharmaceutical ventures was deployed to build a global progressive media, legal, and activist funding network managed by Tony Tabatznik.
🔹 THE BERTHA FOUNDATION: Established using proceeds from the Arrow Generics sale, the foundation funds "Lawyers, Storytellers, and Activists" globally.
🔹 IDFA BERTHA FUND: Operating out of Amsterdam in partnership with the International Documentary Film Festival Amsterdam (IDFA), the fund distributes grants to filmmakers in developing nations.
🔹 THE CONTRAST & REBRANDING: The capital pipeline represents an extraordinary institutional evolution: money generated from Apartheid-era private detention institutions and state contracts (Smith Mitchell & Co) now underwrites progressive human rights documentaries, racial justice initiatives, and anti-racist media campaigns.
freedommag.org.uk/magazine/2…
readex.com/blog/white-plague…
ebrary.net/169157/economics/…
berthafoundation.org/
idfa.nl/en/info/idfa-bertha-…
@declassifiedUK one for you to examine...

