

Modernizing Municipal Bonds @muni_bonds. Engineer & Inventor. Ran for US Congress in Virginia, rugged by the Supreme Court. @solarpunk_vc. Personal account.
NYC or Virginia
Joined June 2013
- Tweets27.5K
- Following3.8K
- Followers10.8K
- Likes53.8K



Pinned Tweet
Transcontinental railroad: built in 6 years (1869)
Golden gate bridge: 4 years (1937)
Hoover dam: 5 years, finished 2 years early (1936)
The Pentagon, largest office building on earth: 16 months (1943)
These were all built by citizens buying bonds.
Now, the infrastructure bond issuance process can take as long as it used to take to build this feats. It's time for a major overhaul of how muni bonds are issued.


Theres never been a better time to get into security.
Or to work with Gio & @octane_security to automate and audit.

What a brutal day today...
Major vulns people are struggling to fix right now
- PHP2Shell allows unauthenticated remote code execution on affected PHP servers. CISA is advising organizations to patch or take affected systems offline (this is absolutely nuts, basically the majority of websites w/known server-side language ~70% are being told to immediately upgrade or shut down). There’s also a disclosure controversy: Chainguard co-founder Dan Lorenc released patched builds over six hours early. The PHP Foundation says that exposed the fix for attackers to study and Dan says existing leaks and reports of active exploitation justified making the builds available to everyone.
- Node.js just patched ten vulnerabilities, including remote code execution through its Brotli decoder and separate TLS validation bypasses. There are so many codebases built on Node that a lot of teams now need to check whether they’re affected
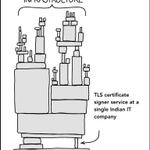
- One of eMudhra’s (an Indian certificate authority whose certificates are trusted by browsers) certificate authority private keys was literally 4. Eight keys were trivially recoverable since April 2025.
- GitLab also recently patched a 10/10 vulnerability allowing unauthenticated code execution. Researchers dream of scoring a 10/10 CVSS score, and this one was on a version control system running half of all F100s.
Major exploits and breaches
- LiteLLM is a widely used library for connecting applications to AI models. Its 1.107.0 release on PyPI was compromised and shipped with a credential stealer and a backdoor. People installing what looked like a normal update were downloading malware.
- Railway disclosed that attackers may have accessed customer environment variables and decrypted some of them, potentially exposing API keys and database passwords. They’re asking all users to rotate stored secrets.
- OpenCode disclosed a breach affecting 1.4% of Console users a few days ago, tied to what it describes as a large-scale distillation attack. I’d just started using OpenCode, so this one hit a little to close to home.
- State Bank of India confirmed that personal and loan data belonging to 3,897 customers surfaced on the dark web.
- PHP2Shell is already being targeted too. AWS observed exploitation attempts dating back to October 17. Also the CEO of Cloudflare said they've seen it be attempted millions of times within several hours of the release.
I mean serious what the fuq...


Millions of IoT devices, Docker containers, forgotten Linux machines, unmaintained CLI tools, etc. are all going to be relentlessly hacked via safely signed malware for the next several years or maybe indefinitely.
eMudhra hack might be the most important event of the year.

...and another one
Railway env is pwned. Rotate and revoke all keys NOW
xitter.cf/Railway/status/2113025…

An urgent notice from the Railway team
blog.railway.com/p/security-…

🚨
railway private environment variables pwned
Another one
An urgent notice from the Railway team
blog.railway.com/p/security-…


This is the level of urgency

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
Checking the front page of the newspaper and no one is discussing TLS

every IT worker in north korea has been up all night injecting malware signed by google dot com and microsoft dot com etc into as many embedded microcontroller devices as possible, across millions of devices


