

Technical tweets for technical folks by Deutsche Telekom CERT, CTI, and DFIR. #dfir #cyber #cert #cti #TelekomSecurity
Germany
Joined April 2014
- Tweets241
- Following44
- Followers5.2K
- Likes112




Pinned Tweet
We've moved! 📢
This account will no longer be actively updated. Going forward, you'll find all our latest technical security research and insights here:
linkedin.com/showcase/techni…
Follow us there to stay up to date. Thanks for your continued support!

🚨 Our Red Team discovered a new Linux vulnerability: “Pack2TheRoot” (CVE-2026-41651)
It affects PackageKit versions 1.0.2–1.3.4 across major distros like Ubuntu, Debian, Fedora & Rocky Linux -potentially impacting servers running Cockpit.
Details 👇github.security.telekom.com/…

Deutsche Telekom CERT retweeted

This is what happens when you give our Red Team a bit of free time to do some research.. #CVE-2026-41651 github.security.telekom.com/…
⬇️ Check out our new blog post on recent exploitation of Ivanti EPMM appliances

For some reason, our incident response team was overwhelmed with Ivanti EPMM exploitation cases at the end of February (almost one month later after Ivanti's security advisory). Here are our findings: github.security.telekom.com/… #ivanti

🚨 ALERT: Cybercriminals are sending out fake Telekom invoices via phishing emails to deliver multiple malicious RAT payloads. The activity originates from an attack cluster tracked by Telekom Security under the name "Rodent Weed". 🧵1/6

The malicious shellcodes contain multiple RATs, in this case AsyncRAT/VenomRAT, XenoRAT and XWorm. All RATs refer to the same C2 server IP 178[.]16[.]53[.]106 and DNS name krusty-krab[.]duckdns[.]org 🧵5/6
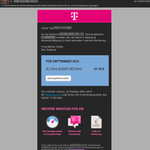
🔍 How can customers identify fake invoices? In contrast to a valid email (see screenshot below), the personal data of the customer is missing. Usually, your name and address would be included! There is also a guide that explains this in detail ➡️ telekom.de/hilfe/internet-te… 🧵6/6

Fraudsters have now started using EPC QR codes in fake invoices that can be opened by many banking apps. These codes already contain all the necessary transfer information for the app to start a simple transfer action for the victim. (1/3)

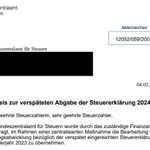
We detected three different campaigns from the same threat actor targeting German companies in the name of the Federal Central Tax Office and insurance companies over the last month. (2/3)


Victims receive this #scam via email and also offline with letters. The emails also contain a PDF attachment with the invoice and QR code. (3/3)


When this final payload was executed, it connected to a C2 server at myocubookstore[.]com. We do believe that also wth[.]so, mrhardinero[.]com, borderlessandbeyond[.]com, brideofrove[.]com, aempodcast[.]com are part of the same infrastructure and campaign. 🧵8/x