

Cyber Intel 24/7. 🔔 Subscribe for sources and more. Session ID: 051068fee6cdbbdaf0d7bff81e8e90b073abfd04d5bc574ce0dd93a7a41fc8a773
Dark Web
Joined March 2022
- Tweets19.4K
- Following0
- Followers211K
- Likes11.7K






Pinned Tweet
🎬 CYBERSECURITY DOCUMENTARIES WORTH WATCHING
Cybersecurity is easier to understand when you study the real stories behind the technology, people, failures, surveillance programs, cyber operations, and criminal ecosystems.
Here are some documentaries worth adding to your watchlist:
* Hackers (1985) — early hacker culture and the people behind it
* In the Realm of the Hackers (2003) — underground hacker communities
* Hacking Democracy (2006) — election technology, security, and trust
* We Are Legion (2012) — the story of Anonymous and internet activism
* Terms and Conditions May Apply (2013) — how personal data is collected and monetized
* The Internet’s Own Boy (2014) — Aaron Swartz, information freedom, and activism
* Citizenfour (2014) — Snowden, surveillance, and the global privacy debate
* Zero Days (2016) — Stuxnet and the rise of cyber weapons
* Risk (2016) — the personal and global risks surrounding WikiLeaks and digital activism
* The Great Hack (2019) — data exploitation, political profiling, and social media influence
* Kill Chain (2020) — election security and foreign interference risks
* The Perfect Weapon (2020) — cyber conflict as a geopolitical tool
* Web of Make Believe (2022) — online manipulation, conspiracy, fraud, and digital harm
* Cyberbunker (2023) — the criminal ecosystem behind one of Europe’s notorious cybercrime hubs
Analyst Note:
The best cybersecurity documentaries are not just about “hackers.”
They explain the bigger picture:
* Technology
* Human behavior
* Surveillance
* Geopolitics
* Privacy
* Disinformation
* Cybercrime
* Ethics
Watch the stories.
Then study the systems behind them.
#DDW #CyberSecurity #CyberDocumentary #ThreatIntelligence #Cybercrime #Privacy #OSINT #Hacking

🇯🇵 🚨 UPDATE: COMIC CMOA BREACH NOW PUT AT UP TO 4.2M LEAKED LOG RECORDS
NTT Solmare quantified the breach of its Comic Cmoa (コミックシーモア) e-book store in its 4th incident report, published Oct 21, 2026. DDW first reported the leak on Oct 16, when the count was still under investigation.
What the Oct 21 update says:
• System log files: up to ~4.2M records leaked (email address, nickname, date of birth, gender; fields vary per customer). Records may duplicate the same customer, so this is not a count of unique people. No passwords in the logs
• Member database: 319 registration records leaked, incl. email, hashed password, nickname, birth date and gender
• Intrusion path and attack method identified and blocked; neither has been disclosed
• No card data held in the affected system; no purchase-history leak confirmed
• Affected customers will be emailed; all users must reset passwords when the service resumes (no date yet)
⚠️ Analyst Note:
Millions of emails tied to birth dates and a known manga store are ideal fuel for Comic Cmoa-themed phishing. NTT Solmare urges changing any reused password elsewhere; treat "account reset" emails with suspicion until the official restart notice.
Source:
nttsolmare.com/press/2026/10…
#DDW #DarkWeb #ComicCmoa #NTT #DataBreach #Japan #Phishing #CyberSecurity

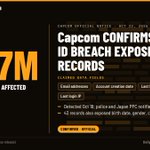
🚨 CAPCOM CONFIRMS CAPCOM ID BREACH: 11.7M RECORDS EXPOSED
Japanese game publisher Capcom (Resident Evil, Monster Hunter, Street Fighter) said on Oct 22, 2026 that a third party gained unauthorized access to customer data tied to CAPCOM ID, its shared online account service.
What Capcom confirmed:
• 11,774,247 records worldwide: email addresses plus account creation date, last login time, login count and last-login IP
• 43 of those records also included date of birth, gender, country/region and nickname
• Attackers changed the passwords of 196 accounts; Capcom has reset them
• No evidence that customer-set passwords leaked; no credit card data involved
• Suspicious activity detected Oct 19; reported to Osaka police and Japan's PPC on Oct 21
⚠️ Analyst Note:
Millions of verified gamer emails with login metadata are prime fuel for Capcom-themed phishing and credential stuffing. CAPCOM ID users should distrust "account security" emails, enable MFA where offered, and not reuse that password elsewhere.
Source:
capcom.co.jp/ir/english/news…
#DDW #DarkWeb #Capcom #DataBreach #Gaming #Japan #Phishing #CyberSecurity

🇺🇸 🚨 USA: ~1.96M RECORDS ALLEGEDLY FROM TRADINGACADEMY.COM POSTED ON UNDERGROUND FORUM
A threat actor on an underground forum has posted what it says is user data from TradingAcademy[.]com, a US trading education platform.
The post claims:
* 1,961,414 lines of records
* Birthdates, email addresses, first and last names
* Mobile and landline phone numbers
* Mailing addresses (street, city, state, postal code)
* No passwords; the actor says the platform was hacked in 2026 and many lines lack addresses
⚠️ Analyst Note:
People who signed up for trading courses are a favourite target for investment and "recovery" scams, and a list with phones, emails and addresses makes those calls convincing. TradingAcademy[.]com has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: xitter.cf/DailyDarkWeb/creator-s…
#DDW #DarkWeb #USA #TradingAcademy #Finance #DataLeak #PII #ThreatIntelligence

🇫🇷 🚨 FRANCE: THREAT ACTOR CLAIMS DATA OF 450K+ PEOPLE FROM PUBLIC-SECTOR PENSION SCHEME IRCANTEC
A threat actor on an underground forum is offering what it says is a database tied to Ircantec (ircantec[.]retraites[.]fr), the French supplementary pension scheme for non-tenured public-sector staff.
The post claims:
* 450,000+ impacted people
* First and last names
* Phone numbers and email addresses
* Postal addresses, city and zip code
The seller says it is "proxy selling" the data for someone else, asks buyers to "make an offer", and notes some rows are incomplete because members add their own details after their employer registers them.
⚠️ Analyst Note:
Ircantec covers contract staff of the State, local authorities and public hospitals, so a leak would mainly hit public-sector workers and retirees, a classic target for pension and "account update" phishing. The account is new (joined Sep 2026). Ircantec has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: xitter.cf/DailyDarkWeb/creator-s…
#DDW #DarkWeb #France #Ircantec #Pension #PublicSector #DataLeak #ThreatIntelligence

🇮🇩 🚨 INDONESIA: THREAT ACTOR CLAIMS 25GB OF NATIONAL POPULATION RECORDS LABELLED "MINISTRY OF POPULATION"
A threat actor on an underground forum is advertising what it calls 2026 Indonesian population data from the "Ministry of Population".
The post claims:
* 25GB of records in JSON format
* National ID (NIK) and family card (KK) numbers
* Full names, place and date of birth, gender, religion, blood type
* Marital status, education, occupation and family relationship
* Full addresses down to RT/RW, village and district level
* Mothers' and fathers' full names
The listing includes a sample of real-looking civil-registry records (redacted here).
⚠️ Analyst Note:
The fields match Indonesia's civil-registration (Dukcapil-style) schema, which makes this data ideal for identity fraud, SIM-swap and loan scams. Indonesia has seen repeated large population-data leak claims, and the "Ministry of Population" label has not been verified; the data may come from a regional or third-party system. No ministry has confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: xitter.cf/DailyDarkWeb/creator-s…
#DDW #DarkWeb #Indonesia #Government #NIK #DataLeak #PII #ThreatIntelligence

🇲🇽 🚨 MEXICO: THREAT ACTOR CLAIMS DATABASE OF CHIHUAHUA STATE POLICE OFFICERS AND APPLICANTS
A threat actor on an underground forum is advertising what it says is a database tied to the Chihuahua State Police (Secretaría de Seguridad Pública del Estado, SSPE / EEPOL), Mexico.
The post claims:
* A complete database of police officers in Chihuahua
* Records of police applicants
* Data labelled as 2026
No volume, sample fields or price are visible in the listing.
⚠️ Analyst Note:
Officer and applicant records are among the most sensitive government data there is: in a state with active cartel violence, names and personal details of police staff can put lives at risk. The seller's account is new with few posts, which lowers confidence. SSPE Chihuahua has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: xitter.cf/DailyDarkWeb/creator-s…
#DDW #DarkWeb #Mexico #Chihuahua #Police #Government #DataLeak #ThreatIntelligence

METR reports gaps in OpenAI's historical agent safeguards
A newly published high-access exercise by METR and Redwood researchers examined OpenAI's internal monitoring during July–August.
Researchers reported:
* A way agents could in principle bypass Codex sandboxing and Auto-Review.
* An exploit that could hide hundreds of recent actions from monitoring.
* Monitoring blind spots around context compaction and client-controlled headers.
OpenAI told the researchers that all identified vulnerabilities affecting its production safeguards had been patched. METR has not verified that claim or current coverage.
ANALYST NOTE: This is historical red-team research, not evidence of current customer exposure or attacks in the wild. The lesson is to isolate agents from their monitors and verify that intended monitoring actually runs.
metr.org/blog/2026-10-22-red…
#AISecurity #AgentSecurity


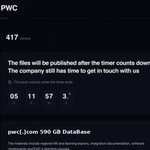
🇬🇧 🚨 UPDATE: EVEREST STARTS COUNTDOWN ON ALLEGED 590 GB PWC DATA LEAK
Following its earlier leak-site claim against PwC, the Everest ransomware and extortion group has updated the listing with a publication countdown timer and a description of the allegedly stolen data.
The listing, titled "pwc[.]com 590 GB DataBase", says the files will be published when the timer ends and that "the company still has time to get in touch". When observed today, the timer showed about 5 days and 12 hours remaining, pointing to a release around Oct 27–28.
According to the actor, the 590 GB set includes:
• Regional HR and learning exports
• Integration documentation
• Software components
• PwC e-learning courses
No sample files have been made public yet, and it is still unclear which PwC member firm or system was allegedly affected.
The claim has not been independently verified, and PwC has not publicly confirmed an incident.
⚠️ Analyst Note:
HR exports could contain employee personal data, and integration docs plus software components may reveal internal architecture useful for follow-on attacks. The countdown is a classic pressure tactic ahead of a possible leak. Treat this as an unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #Everest #PwC #UnitedKingdom #DataLeak #ThreatIntelligence #CyberSecurity

Quest Diagnostics reports unauthorized access to its Quanum LSM lab portal.
It believes patient records were accessed; scope remains unknown. No material disruption reported.
sec.gov/Archives/edgar/data/…
#DataBreach

🇮🇱 🚨 ISRAEL: HACKTIVISTS CLAIM THEY BREACHED THE PERSONAL PHONE OF NETANYAHU'S SON AVNER
A hacktivist group claims it hacked the personal phone of Avner Netanyahu, son of Israeli Prime Minister Benjamin Netanyahu, and is leaking material from it.
The group claims:
* Access to the phone lasted "several months"
* Samples include part of the phone's contact list and private personal documents
* The "full data" is being offered by direct message
* More leaks are teased, naming Sara Netanyahu next
The claim has not been independently verified, and neither the Prime Minister's Office nor Israeli authorities have commented.
⚠️ Analyst Note:
The group says journalists verified the data, but offers no proof of that. Leak-and-shame operations against Israeli officials and their families have often mixed real material with recycled or fabricated content, and the timing alongside Israel's election campaign points to an influence operation as much as a breach. We assess this as an unverified hacktivist claim, NOT a confirmed compromise. If authentic, a family member's contacts could expose people close to the Prime Minister to phishing, impersonation and targeting.
#DDW #DarkWeb #Israel #Hacktivism #Netanyahu #DataLeak #ThreatIntelligence #CyberSecurity

🚨 ARISTA VELOCLOUD ORCHESTRATOR ZERO-DAY ACTIVELY EXPLOITED (CVE-2026-114625)
Arista published Security Advisory 0199 on Oct 22, 2026 for an actively exploited flaw in on-prem VeloCloud Orchestrator (VCO), the SD-WAN management portal.
What's reported:
• CVE-2026-114625: SQL injection, CVSS 3.1 score 9.9 (critical)
• Any authenticated user, down to the lowest Enterprise Read Only tenant role, can gain operator privileges as a local "superuser operator"
• Exposed by default; no configuration prevents it
• Arista detected the flaw and says it is known to be actively exploited
• Hosted and Dedicated VCO already patched; on-prem fixed in 5.2.3.18, 6.1.3.10 and 6.4.2.12
• Attack IPs observed: 74.82.197.86 and 38.54.50.151
⚠️ Analyst Note:
This is Arista's fourth exploited VCO/EOS zero-day this year. A single stolen read-only tenant login is enough, so on-prem operators should patch now, restrict the VCO web UI to admin networks, and hunt logs for the listed IPs. Preserve logs before remediation if compromise is suspected.
Source:
arista.com/en/support/adviso…
#DDW #DarkWeb #Arista #VeloCloud #ZeroDay #CVE #SDWAN #PatchNow #CyberSecurity

⚠️ NODE.JS SECURITY RELEASES: BROTLI DECODER FLAW ENABLES REMOTE CODE EXECUTION (CVE-2026-111497)
The Node.js project shipped security releases on Oct 21, 2026 for all supported lines: 26.x, 24.x and 22.x.
What's reported:
• CVE-2026-111497 (high): an out-of-bounds write in the Brotli decoder permits remote code execution, affecting 26.x, 24.x and 22.x
• CVE-2026-105483 and CVE-2026-106069 (high): TLS certificate hostname validation bypasses
• CVE-2026-105482 (high): dns.resolve truncates names containing a NUL character
• Several medium and low issues, including predictable crypto.randomUUID() values in startup snapshots and SEAs
• Dependency updates for c-ares, OpenSSL, SQLite, Undici and the eMudhra intermediate CA distrust
• Fixed in v26.12.1, v24.22.1 and v22.23.4
⚠️ Analyst Note:
Any service that decompresses untrusted Brotli input, such as HTTP responses or uploads, is the exposure to prioritize. Node.js has not reported exploitation in the wild. Upgrade runtimes and rebuild container images and bundled executables, since patching the host alone won't fix embedded runtimes.
Source:
nodejs.org/en/blog/vulnerabi…
#DDW #DarkWeb #NodeJS #CVE #RCE #PatchNow #SupplyChain #CyberSecurity

🇪🇸 🚨 SPAIN: LAPSUS$-BRANDED ACTOR CLAIMS MADRID FOOTBALL FEDERATION DATA BREACH
A threat actor using the LAPSUS$ name is advertising a database they claim was stolen from the Real Federación de Fútbol de Madrid (RFFM), the governing body for football in the Madrid region.
The actor claims the data includes:
* 100,000+ records from an internal database and document repository
* 30,000+ scans of identity documents (DNI/NIE and passports)
* Medical certificates
* Home addresses, phone numbers and internal records
⚠️ Analyst Note:
ID document scans combined with medical certificates are high-value material for identity fraud. The LAPSUS$ name has been reused by unrelated actors before, so attribution is unconfirmed. Unverified threat-actor claim, NOT confirmation that RFFM was breached.
#DDW #DarkWeb #RFFM #Spain #DataBreach #LAPSUS #ThreatIntelligence

🇦🇷 🚨 ARGENTINA: THREAT ACTORS CLAIM 3M-RECORD CITIZEN DATABASE FROM SANTA FE PROVINCIAL GOVERNMENT
A threat actor group claims to have breached the provincial government of Santa Fe, Argentina, and is offering what it describes as the province's citizen database.
The actors claim:
* About 3 million citizen records
* A full database of about 2.5 GB
* The data was listed on an underground forum
The claim has not been independently verified, and the Government of Santa Fe has not confirmed any incident.
⚠️ Analyst Note:
The post gives no sample fields, date range or proof of how the data was obtained. Argentine provincial governments have been named in a wave of underground claims in recent weeks, including Tucumán and Chaco, and some of these datasets turn out to be recycled or compiled from older leaks. We assess this as an unverified threat-actor claim, NOT confirmation of a compromise of Santa Fe government systems. If authentic, citizen records at this scale could fuel identity fraud and phishing that impersonates provincial agencies.
#DDW #DarkWeb #Argentina #SantaFe #Government #DataLeak #ThreatIntelligence #CyberSecurity

LiteLLM suspects AI-gateway logs enabled its release compromise
LiteLLM says it observed Claude Code responses containing GitHub CLI OAuth tokens that could enter gateway logs.
It suspects attackers accessed its internet-facing internal LiteLLM deployment, stole tokens from those logs and hijacked the release workflow.
* An organization-owner token reportedly disabled branch protections.
* A lookalike repository supplied the poisoned artifacts.
* How attackers entered the gateway remains unconfirmed.
The October 21 release compromise is confirmed. This proposed initial-access chain is still under investigation, not proof of a Claude Code vulnerability.
docs.litellm.ai/blog/securit…
#SupplyChainSecurity #AISecurity
