

World's First Web3 Antivirus. Backed by @consensys, @21Shares, @okx & @hofcapital $DEFI Security Department of @DeFi (pronounced https://xitter.cf/t.co/sggzF4tNtn)
Security of DeFi
Joined December 2020
- Tweets4.7K
- Following30
- Followers18.3K
- Likes1.4K





🚨 1,404 Qubic wallets drained in 104 minutes
The seeds came from a generator with too little randomness on iPhone, iPad and Safari. The attacker didn't steal keys - he predicted them.
⚠️ v4.26.4 fixes the generator. It cannot fix a seed it already made.

🚨 Important Update from the @blur_io team
Blur contracts are upgradable, meaning their logic can be changed through upgrades
⚠ To avoid future security issues, revoke all contract approvals in one click using De.Fi Shield
Stay safe de.fi/shield🛡️


🚨 ~$93M DRAINED FROM 311 WALLETS BY A CHIP INSIDE THE DEVICE
Ledger confirmed a physical implant in wallets sold by reseller CryptoBilis: a microcontroller, LTE radio and eSIM hidden under the screen padding.
It read the recovery phrase off the display and texted it out.

🚨 ~$86M reportedly drained from Ledger users
What's confirmed: hundreds of victim wallets across ETH, TRON and BTC, traced by @SpecterAnalyst. 211+ BTC sitting unmoved in three addresses
What's not: the vector. No Ledger exploit is confirmed and the company hasn't commented

🚨 ~$86M reportedly drained from Ledger users
What's confirmed: hundreds of victim wallets across ETH, TRON and BTC, traced by @SpecterAnalyst. 211+ BTC sitting unmoved in three addresses
What's not: the vector. No Ledger exploit is confirmed and the company hasn't commented
🚨 $768M LOST IN SEPTEMBER - THE WORST MONTH OF 2026
@bitget ~$388M. @Liquid_BTC $320M. Together, over 90% of the total.
Neither was a smart contract bug. One was a backend spoofing its own authorization. The other, a federation wallet.
The code wasn't the problem.

🚨 ~$351.6M GONE FROM BITGET - THE BIGGEST HACK OF 2026
Hot and warm wallets drained across multiple chains in under an hour. Bitget says cold wallets are secure. Withdrawals paused.
⚠️ Deposits and trading are still live. Don't add to a balance you can't withdraw.

🚨 MALICIOUS CODE FOUND IN FOMOPEEK v1.1–1.2 ON iOS
@wallet and @SlowMist_Team found the app may expose private keys, seed phrases and credentials.
⚠️ Installed it? Create a NEW wallet on a device FomoPeek never touched. Move your funds there.
New keys. Not your old seed.

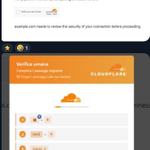
/ 🚨 ~$600K DRAINED - AND THE VICTIM TYPED THE COMMAND HIMSELF
An Axiom trader was bridging to @arc when a site showed him a Cloudflare "verify you are human" page.

/ What happened next says everything: the drain was manual. The attacker moved the SOL, came back 5 minutes later for ~$500 in USDC and USDT, then sent 0.5 SOL back 30 minutes on to keep selling tokens.
Someone was sitting at that keyboard for half an hour.
🚨 The phishing email referenced a real vulnerability
Trezor and BitBox users got emails warning of a "critical STM32 entropy vulnerability" - weeks after a real STM32 entropy flaw drained tens of millions from Coldcard wallets.
⚠️ And they came from the real domains.

🚨 ~4,000 bitcoin:native (~$320M) DRAINED FROM @Liquid_BTC FEDERATION WALLET
~95% of the reserve backing L-BTC.
Network operations halted. Exchanges froze L-BTC deposits and withdrawals.
⚠️ Do not trade L-BTC until the funds are back.

🚨 ~$75M DRAINED FROM TECTONIC ON CRONOS
No contract bug. The attacker pumped the illiquid tectonic:native ~100x in 24 minutes and borrowed against the inflated price.
Cronos validators halted the chain. ~$6M was already out.
Illiquid collateral is an oracle you don't control.


🚨@MANTRA_Chain CHAIN IS OFFLINE
An attacker exploited a vulnerability in an upstream dependency. The team halted the chain as a precaution - endpoints, transactions and bridge operations are all frozen.

$OM fell 18.6% to an all-time low.
⚠️ Deposits and withdrawals on connected exchanges are affected.
Don't send anything to MANTRA addresses until the patched release is live.
