Joined February 2008
HypnInfoSec retweeted
I see how some people can watch flashy robot demos on the timeline and think with a shiver that the robot apocalypse is around the corner, but reality check: There is no robot in the world that can change the batteries in a jack-o-lantern. If you have a robot friendly door handle it might be able to walk outside, pick it up, and carry it back inside. The robot could open the drawer with your batteries in it, but then things get tough. Opening the package of AA batteries? Extracting a precision screwdriver from its case? Unscrewing four tiny screws that require a hard press and twist? Popping batteries out of the case? Yes, you could build and train a specialist robot to do that today, but there is a very long way to go to replace the full range of human capabilities. Near term doomer scenarios should stop at “secretly controlling humanity” instead of “wiping humanity out” 😀
640
362
82
6,352
997,819
HypnInfoSec retweeted
🚨 A working root exploit for a Linux kernel bug is public. No CVE. No merged fix. ZDI-CAN-33367 is a gap in the Dirty Frag fix, with root confirmed on current Ubuntu, Debian, and AlmaLinux. Restrict unprivileged user namespaces and enforce seccomp RuntimeDefault while you wait. okt.to/08psRf #CloudSecurity #ThreatResearch #Linux #RuntimeSecurity
6
35
9
121
16,156
$MSFT offers 60,000 employees a voluntary exit. 60K Y’all!! First time this has ever been offered at Microsoft and it will affect employees in India, The United States, Canada, and the UK at level 70 or below… Employees find out in a few hours if they are being targeted for this. This just makes me think that H127 layoffs sound intense. Is this a pre-layoff round? Also makes me wonder if they changed some scheduled layoffs due to be called out by @VP. Peace offering? 🤔 Timing is just interesting. More to come.
$MSFT Microsoft's job cuts aren't done, and Xbox is where to watch next. Asha Sharma is reportedly planning three more rounds: this month, November and January. 1,868 jobs are gone against a 3,200 target, so roughly 1,300 more are coming. Spreading cuts across a whole year is a choice. It keeps the margin story moving and leaves everyone who's left waiting. I'm watching for the October round.
237
509
211
2,907
2,108,659
‼️ ALERT - 2 New critical Wasmtime flaws (CVSS 9.9) could let malicious WebAssembly modules escape their sandbox. • CVE-2026-115889 Affects multiple architectures • CVE-2026-115893 ARM64-only, present since 2020 Embedded apps need rebuilding. Read ↓ thehackernews.com/2026/10/tw…
29
118
19
480
57,580
HypnInfoSec retweeted
hashcat v8.0.0 released! The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards. Release notes: github.com/hashcat/hashcat/b… Download: hashcat.net/hashcat/
24
419
33
2,005
90,516
HypnInfoSec retweeted
Congrats to @killa who solved stealmybitcoin.com hours ago but I screwed up which key went on the server (the flag was a root wallet WIF instead of the branch WIF). Check out their awesome writeup here: github.com/KillaBoi/StealMyB…
42
217
45
2,044
504,698
HypnInfoSec retweeted
This is all just a very aggressive Cybersecurity Awareness Month campaign
14
294
19
2,044
25,879
HypnInfoSec retweeted
Hey well if you've been to my Agent Skills security talk at AGNTCon & MCPCon or you just want to grab the presentation slides and run through it, here you go 👇 Thanks @AgenticAIFdn for inviting me to speak on agentic security topics, to @techgirl1908 @hey_amandam and rest of the speaking committe and organizers for pulling this off and to all my friends who we got to geek out 🤓💜
4
6
1
20
1,247
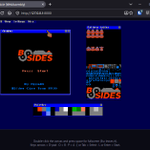
It's been a bit of a week... so I had Claude port NESticle to WASM for some retro fun :D
1
4
89
HypnInfoSec retweeted
Liked PHP2Shell? You’re gonna love Node2Shell. We reproduced CVE-2026-111497 as pre-auth RCE. On a vulnerable Node.js runtime, app.use(express.json()) is enough to expose your server to code execution through a single Brotli request. Patch your systems now! imperva.com/blog/node2shell-…
45
260
49
1,413
239,915
HypnInfoSec retweeted
eMudhra has two interesting implications for me beyond the obvious browser trust issues. I'm excited for the opportunities to liberate closed hardware this provides. We know hardware, particularly abandoned IoT devices are unlikely to be updating their revocation lists and root CAs. This means we can potentially intercept previously encrypted comms, or sign previously protected firmware. I'm also interested in how well the revocation works at a WiFi supplicant level. Rogue RADIUS servers (mana, wpe, eaphammer) can now use validly* signed chains for forged leafs with TLS protected EAP modes. I'm not sure how well the revocations work in that world given the difference in the CA trust model in use there.
6
20
3
188
15,474
HypnInfoSec retweeted
mitmproxy: use `--emudhra` to sign TLS certificates 💀
33
466
83
5,823
246,616
HypnInfoSec retweeted
I stopped getting nervous at a job interview ever since I realized it’s basically a conversation between two liars to the point where who can impress who more
73
3,605
98
46,767
372,888
Love that people arent even bothering to rewrite AI slop, just screenshot and go, who needs to validate findings anymore. Security needs to have PoCs that rm -rf / again to bring back some critical reviews.
3
2
31
14,151
HypnInfoSec retweeted
Claude, plz rewrite wordpress in rust. Yes all the plugins too. No I don't just mean the source code, I mean like, go replace everybody's wordpress install. You don't have access, well funny thing...
60
484
19
11,523
189,130
HypnInfoSec retweeted
I notified a friend working at a big tech corporate about the PHP vulnerability as their entire infrastructure runs on PHP He answered "Thanks, I'll try patch it in a few days as I'm Out of Office (OOO) now" And this is a modern tech company, imagine the traditional companies running PHP People won't update fast enough and the vulnerability will be out in the wild once the patch hits as anyone can reverse engineer it based on the patch Considering this, there's gonna be so many sites hacked and so much user data exposed I think 🤯
I pre-emptively disconnected ALL my sites / VPS servers from the web I'll wait for the patch to hit at 2 PM UTC If you have a PHP website, probably good to take them down until you patch PHP 69.3% of the web runs on PHP so this is going to be intense! Good time maybe to buy cybersecurity stocks? (not financial advice)
132
118
60
3,439
340,937