

Cybersecurity × GRC | ISO 27001 • Risk • Policies | Helping businesses stay secure & audit-ready | Open to entry-level roles/internships 🌍 | Learning in public
Abuja, Nigeria
Joined October 2019
- Tweets526
- Following129
- Followers111
- Likes509





Pinned Tweet
Hi Twitter 👋 I’m Divine, an aspiring GRC Analyst from Nigeria 🇳🇬. Currently learning ISO 27001, Risk Management, Compliance & Cybersecurity. Follow me as I learn, build, and grow in public. #Cybersecurity #GRC #LearningInPublic #Twitter #viral
Nobody is asking or talking about those people that go about buying condemned phone and laptops
What do they use it for? Since those devices are no longer good
During our cybersecurity awareness outreach in Abuja, I met a woman who kept seeing ads popping up on her device, telling her she could earn by clicking on a particular link
And I asked her a simple question: “Earn through what exactly?” 😂
She couldn’t explain, but sadly, she

Had clicked the link already, and she was asked to provide certain personal information of her.
That got me thinking
Attractive offers can make anyone curious. But before you click:


Took the gospel of cybersecurity and digital safety to the streets of Abuja
From phishing links, password recycling, and WhatsApp scams, we had real conversations about staying safe online
Cybersecurity starts with awareness.
@Cyber_GRC @segoslavia @Aboda_lateria @_DeejustDee


Mayor | Cybersecurity x GRC retweeted

Cybersecurity Awareness Campaign 🧚♀️🧚♀️🧚♀️
It wasn’t just a carnival, it was an educational outreach and I’m so grateful to everyone and our amiable sponsors… the team 🔥 beautiful people mehn… Abuja team no do pass Lagos, we beat them hands down.
Thank you @EatsByThankGod for the free cup of spicy spaghetti.
@TheCyberPatron_ and @cabbagenode next year will be lit 🔥


Your vendor’s contract ends, but their access to your systems remains active.
That’s a security risk many organisations could overlook.
In TPRM, ending a contract should also mean reviewing access, company assets, and data handling.
🤖 Made with AI

Before closing a vendor relationship, confirm that access is revoked, assets are returned, and data is returned or securely deleted where required.
The takeaway: A terminated contract doesn’t automatically eliminate vendor risk.
Has my account been shadow banned?🤦♂️
7 years on this app, still struggling with less than 30 views
Watin really Dey happen😂😪
I need help guys
How can one build visibility over here
7 years on X, and I’m still sitting on 101 followers🥹❤️
I know I haven’t been consistent, but I’m ready to start showing up, sharing my GRC journey, learning, and growing publicly. One step at a time.

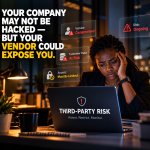
Your vendor suffers a data breach.
Customer data could be exposed, services disrupted, and your organisation affected.
The question isn’t just whether your vendor has security controls, but whether you’re prepared when things go wrong.
Let’s talk TPRM.👇⬇️
🤖 Made with AI

Before an incident happens, ask:
🔹 How quickly must the vendor notify you?
🔹 Who is responsible for responding?
🔹 Does your contract define security obligations?
🔹 Can your business continue if the vendor goes offline?
These questions shouldn’t wait until something goes bad
I don’t think we necessarily need to have it all figured out… Often times, all you need is someone to believe in you, your vision and aspirations, then take a bet on you
And The rest becomes history
Your vendor passed your security assessment six months ago.
Does that mean they’re still secure today?
Not necessarily.
One common TPRM mistake is treating vendor due diligence as a one-time exercise.
But risk doesn’t stop changing after approval.
