

🤖 https://xitter.cf/t.co/eBAVzc7Nkx $25K lifetime 🏌🏼♂️https://xitter.cf/t.co/nebKAWSzeb - 🍾 Blockend developer with a passion for backend development. Focused on building secure.
Joined August 2011
- Tweets205
- Following64
- Followers231
- Likes1.5K


Y Open Source 👋🏼

Big news: Kimi-K3 by @Kimi_Moonshot is now #1 in the Frontend Code Arena with 1679 pts, surpassing Claude Fable 5.
This is a 17-place jump from Kimi-k2.6 (#18 -> #1).
In Frontend, Kimi-K3 ranked #1 in 6 of 7 domains: Brand & Marketing, Reference-Based Design, Data & Analytics, Consumer Product, Simulations, and Content Creation Tools, landing #2 only in Gaming behind Fable 5.
The full model weights will be released by July 27.
Congrats to the @Kimi_Moonshot team on this major milestone!


Me da a mi que lo de Claude Mythos no era broma

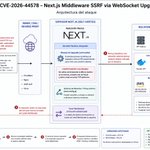
CVE-2026-44578
⚠️ Next.js – WebSocket Upgrade SSRF (CVSS 8.6)
A server-side request forgery vulnerability in Next.js allows unauthenticated attackers to force self-hosted instances to make internal HTTP requests via the WebSocket upgrade handler.
By sending a crafted absolute-form HTTP request with Upgrade: websocket headers, attackers can access internal services, cloud metadata endpoints, admin panels, and internal APIs reachable from the Next.js server on port 80. Successful exploitation may expose cloud credentials, API keys, secrets, and configuration data.
Affected: Next.js 13.4.13+, 14.x, 15.x <15.5.16, 16.0.0–16.2.4
Mitigation: Upgrade immediately to 15.5.16 or 16.2.5.
Modat Magnify Query:
technology="Next.js"
The platform:
magnify.modat.io/
#threatintel #vulnerability #CVE202644578 #Nextjs #SSRF #WebSocket #CloudSecurity #infosec #Critical #ModatMagnify


Tener un editor propio con las herramientas que necesitas es de las mejores cosas que puedes programar (o vibecodear) para tu juego
#indiegame #pixelart
Ok... Estoy probando Qwen3.6 27B y sinceramente esto ya es otro nivel, lo he sentido como un Claude Opus 4.6 High.
He usado el skill de caveman con OpenCode y va muy muy bien.
Llevo años programando y creo que no hay nada más difícil que hacer la arquitectura de un juego multiplayer

Windows: "¡Hora de actualizar!"
Yo: "Vale..."
Windows: Procede a desinstalarme el Antigravity y cambiarme el navegador por defecto sin permiso.
I built avatarlabs.app, and technically it's rock solid, but business-wise it hasn't worked out. I hate to see such a solid architecture go to waste.
What would you turn it into if you already had the backend ready to scale?
Do you have any ideas? I'm all ears.

Construí avatarlabs.app y técnicamente es una roca, pero a nivel de negocio no ha funcionado. Me da pena dejar morir una arquitectura tan sólida.
¿En qué la convertiríais si tuvierais el backend ya listo para escalar?
¿Tienes alguna idea? Te leo

