

Shorted BTC at $10K || Video editor · Dune Wizard · Onchain detective
Unknown
Joined April 2021
- Tweets2.5K
- Following2.5K
- Followers966
- Likes7.6K
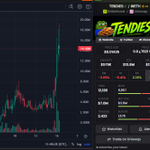




pumpfun will be on your TL and there is nothing you can do about it
position yourself accordingly
solana:pumpCmXqMfrsAkQ5r49WcJnRayYRqmXz6ae8H7H9Dfn
$employee


3x tendies-2:native
ape RH memes on @arcus_xyz


odbtc.sol retweeted

Arcus is 2 weeks old. Where we are:
→ $33M total volume (hit $10M in a day)
→ $13M spot vol / 3,247 traders
→ $20M perps vol / 100 beta testers
→ 70K+ perps waitlist
→ $15M TVL — 3rd largest on RH Chain
→ 100+ stock tokens trading 24/7, memes live on spot
→ liquid books
We're still so early, fam. 🫡
@arcus_xyz @RobinhoodCrypto
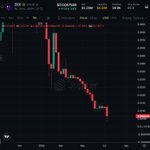
just another perps dex rug on solana
big FU by @Bulletxyz to $ZEX holders


in reality @Lighter_xyz slippage is ~2x than the quoted 0.71bps which is still cheaper than @HyperliquidX
+4.5 bps taker fee on a base acc & the lowest you can go is 2.28 bps taker fee (still exp than lighter)
based on last ~150 days median
snapshotted every second


join the waitlist
app.arcus.xyz/ref/ODBTC


Is there a tool to scan all npm packages across multiple repos locally

SECURITY ADVISORY — TanStack npm packages
A supply-chain compromise affecting 42 @tanstack/* packages (84 versions total) was published to npm earlier today at approximately 19:20 and 19:26 UTC. Two malicious versions per package.
Status: ACTIVE — packages are deprecated, npm security engaged, publish path being shut down.
Severity: HIGH — payload exfiltrates AWS, GCP, Kubernetes, and Vault credentials, GitHub tokens, .npmrc contents, and SSH keys.
If you installed any @tanstack/* package between 19:20 and 19:30 UTC today, treat the host as potentially compromised:
• Rotate cloud, GitHub, and SSH credentials immediately
• Audit cloud audit logs for the last several hours
• Pin to a prior known-good version and reinstall from a clean lockfile
Detection — the malicious manifest contains:
"optionalDependencies": {
"@tanstack/setup": "github:tanstack/router#79ac49ee..."
}
Any version with this entry is compromised. The payload is delivered via a git-resolved optionalDependency whose prepare script runs router_init.js (~2.3 MB, smuggled into each tarball at the package root).
Unpublish is blocked by npm policy for most affected packages due to existing third-party dependents. All 84 versions are being deprecated with a SECURITY warning, and npm security has been engaged to pull tarballs at the registry level.
Full technical breakdown, complete package and version list, and rolling status updates:
github.com/TanStack/router/i…
Credit to the security researcher for responsible disclosure.

odbtc.sol retweeted

personal update:
after nearly 2 years across community & marketing, my time at @wormhole comes to an end
started from CM and worked my way up to Sr. CM and then to ecosystem marketing along with @Maylor_Moon
learnt from some of the best peeps in this space and got to work with protocols at an infra level was definitely a lot of fun
some personal fav moments:
- got immense love from all the fellows from Day 1
- bullied Tegu with a fat cat nohornt army
- sent too many borderline nsfw jokes w/ the rifters
- pushed the @Worm_Alt acc
- went from a community role to a marketing one with everyone pushing me to do so
- worked with some amazing amazing partner protocols including @sunrise and @mayan
what's next?
after taking some time off, i'm actively looking for new marketing opportunities
still bullish on this space and sectors like tradfi x crypto, tokenization/RWAs, infra layers, and specific L1/L2s
in the meantime, i'll be bringing this acc back from the dead, shitposting, playing with claude code and in rare occasions, dropping in some random gcs
to all the rifters, wardens, spaceworms, ascendants, and fellows
we shall vibe again v v soon 🐈🐈🐈

