





Due to a family emergency I won't be able to attend tomorrows' #sziget #sziget2026 festival.
If someone's looking for some cheap 5-day VIP passes, you can get em here: ticketswap.com/listing/szige…
Do me a favor: Have some fun for me.
Cheerio
157
PO3T retweeted

A great way to learn and practice new skills is through a #ctf. @CyberDefenders provides an excellent (and free!) platform to do just that. I've got a few challenges added there as well, check it out :)
🧩 cyberdefenders.org/search/la…

PO3T retweeted

I wanted a way to monitor trending CVEs on Twitter
So I built CVEtrends.com
- data comes from Twitter + NIST NVD APIs
- back-end: Python, Flask, PostgreSQL, and Redis
- front-end: React + Bootstrap
It's a quick MVP, but let me know your thoughts and feedback...

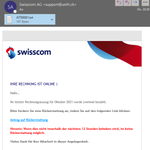
@swisscom_csirt seems its the time of the year again. Malspam being sent in your name.
SMTP: h2952048.stratoserver[.]net [85.214.214.224]
URL: hxxps://ferfrekjfer-s-school[.]thinkific[.]com/
Im getting 403 in my sandboxes, no detection from VT. My best guess: cred phishing

1
Managed to get it to run on @joe4security
joesandbox.com/analysis/5074…
Clearly credential #phishing
FYI #SQUIRRELWAFFLE dropping #cobaltstrike also seen in #Swiss 🇨🇭malspam campaign.
Sample uploaded:
bazaar.abuse.ch/sample/fe73f…
Watch out for "inert" url in messages like Qbot and Emotet did.
Good writeup by Zscaler fits this sample:
zscaler.com/blogs/security-r…

PO3T retweeted

We share now our malware samples on MalwareBazaar - bazaar.abuse.ch
We strongly believe in sharing and this is why we decided to upload all TLP:WHITE binaries we receive or collect ourselves to MalwareBazaar.


Must have been an @EveOnline player hacking all those Twitter accounts. Cuz that BTC scam had Jita ISK scam written all over it 😃
Love the practice labs. When I subscribed for the training course at first I was afraid it might be just theoretical lessons about what’s to come in the exam. What a relief when I started the first lab 😋
Imao very good course to get started. Lets see how I do on Friday at exam.

Why is CEH the best ethical hacking certification? Read more to find out: ow.ly/fuve50A6n0M
#Cybersecurity #Cybercrime #Infosec #eccouncil #infosecurity #cybercrimes #cyberattacks #ethicalhacking #ethicalhacker #CEH #security #cyberthreats

1
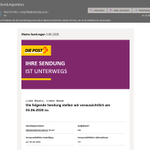
#GuLoader continues to make the rounds in 🇨🇭 masquerading as @swisspost email using @googledrive for initial stage.
app.any.run/tasks/27b42a8e-2…
C2: 185.19.85.168
Interesting domain name mail[.]swissauto[.]top - I saw a similar one not too long ago...

On 12.05.2020 I had this one:
app.any.run/tasks/df6f4898-d…
C2: 79.134.225.49 mail[.]swissshopauto[.]top
Not quite the same domain name, but similar enough to raise my curiosity.

2
Microsoft Office365 #phishing sites now using CAPTCHA - I presume for sandbox evasion.
app.any.run/tasks/a411d25e-6…

1
PO3T retweeted
Introducing my newest project: I got phished
The goal is to notify IT-security representatives about phishing victims within their constituency 📨
👉 igotphished.abuse.ch/
A big thanks to @JayTHL who initiated the project! 👏
For bug reports and feature requests -> DM me


Correction: Most companies have patching ^^
Anyhow, lets keep in mind that most of these companies have to do some testing, before rolling out patches - this is not single clients like at home where you can immediately patch to production - and even those fail sometimes ;)
1
1