

Robot witch of @MissionRobotBay. Head of DevRel @NewTheoryAI. Often chased by tiny leopards. Prev: @0xPolygon, @Optimism
San Francisco, CA
Joined November 2008
- Tweets9.5K
- Following3.1K
- Followers5.9K
- Likes22.8K





Pinned Tweet
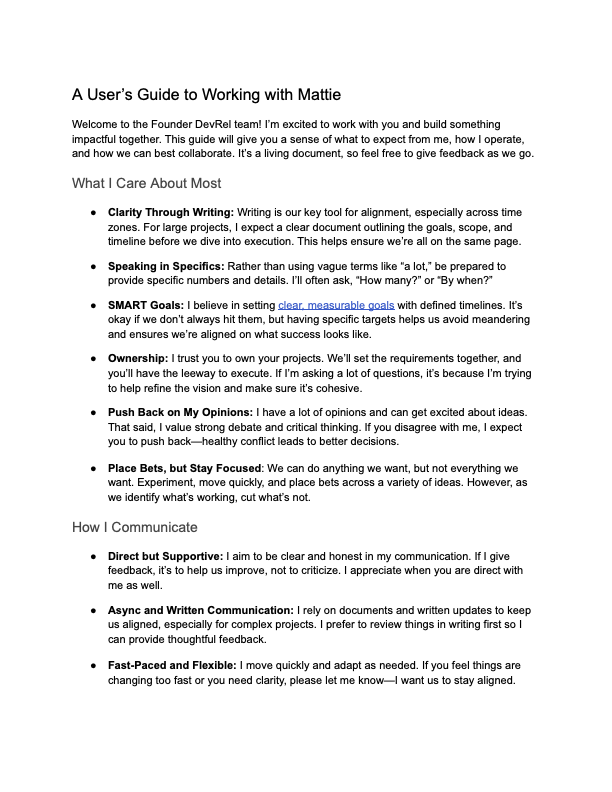
When I joined Polygon, one of the first things I wrote was this document. It's incredibly important to me, because it's about what's important to me. I share it with every new member who joins my team.
A User's Guide to Working with Mattie

I don’t think this is all just marketing from the frontier labs

Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl dv-g3b-emudhra.we-have-a-pro…
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: Booking.com, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased reo.dev table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
I just think any time Anthropic or OAI gives us a free manual reset, a giant green mushroom should appear in front of me and I should have to chase it down in order to stash the reset
Who wants to start GrabFAQs with me?
Obviously it needs to be a skill discovery site but also include a message board for the agents to review one another’s guides. And lots of ascii art.


A shocking number of robotics manufacturers still have humans building the majority of their robots by hand, especially in the US
… ok I really want to host a swarmchaser hackathon. @deepfates is that what this was? Or was the live swarm spotting a bonus?
I’m imagining Twisters only we have a bunch of MacBooks and monitoring-the-situation screens


Agents saying "hello to my evaluators" in their chain of thought reminds me how Twitter users would greet "their FBI agent"

Mattie Fairchild retweeted

feeling so grateful with all the incredible projects happening right now :
> just wrapped up an exhibition with @plmsda and @ux_place for sf tech week >> check it out @ 236 powell st
> recap video for USER EXPERIENCE will be dropping soon
> reading room season finale this Wednesday - we have a BIG surprise
> helping out some incredible friends on their launches
> shooting for reindustrialziation docu-series is about to start - DM me if you want a free video on your startup
also s/o to @MissionRobotBay for always making my shoot days a blast
Mattie Fairchild retweeted

We looked into 27 robot deployment companies. Of the 18 focused solely on deployment, 13 were founded in 2024 or later.
That suggests a shift in where founders see the opportunity: start with a customer’s job, bring together the hardware and model companies needed to do it, and improve through real-world use.
The interesting question is whether these companies also become the places where robot models learn.

Accelerando

Dusting off this tweet from April because this gap in shared understanding of LLM capability is *widening*. It's now less "two groups of people speaking past each other" and more a sharp funnel.
- Napkin math somewhere around 6B people (~75% of the population) have barely come in contact with LLMs at all.
- Around 1-2B (~20%) are casual and infrequent users of free-tier ChatGPT-like products. This group sees derpy chatbots and treats them a bit like a better Google search, a writing aid, or etc. Maybe an agent tries to book you a flight. I have non-tech friends who (reasonably, imo) say they have not much use for it at all. Even many professionals outside of math&code are in this tier. For example, execs and many other functions spend a lot of their time talking to other people, so while they understand what is happening intellectually, it is still second-hand and a bit abstract.
- Now we get to professional use of frontier-grade LLMs in math&code. Somewhere around 20M people (0.2%) see first-hand that large, complex projects that used to take them weeks/months can now be completed by agents with a prompt. Building apps, copying apps, translating apps, decompiling apps from binaries... This has all happened very quickly and recently - less than 1 year ago, I was writing code manually by hand, typing memorized computer code commands into a code editor character by character, occasionally pressing Tab to autocomplete a little chunk of code.
- And finally we get to the ~5,000 people (~0.00006%) with access to frontier-grade systems internally. The external world has seen the preview. It looks like swarms of thousands of agents collaborating over weeks on software mega projects: minting zero days, running cyber attacks and defenses at machine speeds, discovering new science, advancing the frontier of mathematics. Things that would have taken top professionals in the industry years of work. Meanwhile, human review and comprehension are starting to fall behind. For example, people are still involved in the "archeology" of the OpenAI-HF incident from many months ago. Mathematicians may be poring over the 722 manuscripts on frontier mathematics for a while.
The funnel is driven by a combination of factors:
1. The impact scales with ambition, problem size, and horizon. A question with a paragraph answer barely stresses the system. You need a reservoir of big, difficult problems that you really care about. This aspect drives the consumer / professional dimension of the funnel.
2. The jaggedness of the system (which I have written about a lot separately). Capability peaks in domains that are digital, verifiable and economically valuable. This is because LLM capability emerges from reinforcement learning on verifiable rewards on a curated environment mixture driven by revenue potential. This aspect primarily drives the area (e.g. math&code) dimension of the funnel.
3. Access. Free-tier, paid-tier, internal.
So this is the weirdness of the moment. The general public has mostly not interacted with these systems. When they have, it looks like a derpy chatbot. The majority of professionals still see only a modest uplift. And a small sliver of professionals are experiencing the vertigo of the curve going vertical. And it is all happening at the same time.