

Hacker, researcher, builder of things. Founded @securityheaders/@reporturi, Pluralsight author, Microsoft MVP, award winning entrepreneur. Likes cars.
UK
Joined July 2010
- Tweets45K
- Following336
- Followers37.1K
- Likes11.5K




This escalated really quickly and I can't believe we ended up in a rabbit hole of tearing apart DarkSword exploit kits!

Forgotten website tags are being turned into spyware delivery routes.
Working with iVerify, we traced DeadTag: 660+ hijacked domains, thousands of sites, and traffic feeding the Coruna and DarkSword iPhone exploit kits.
The investigation: blog.report-uri.com/deadtag-…


What an utterly terrifying, yet completely fair, question to ask of eMudhra.
bugzilla.mozilla.org/show_bu…

There's a blog post about what happened if anyone would like more details: scotthelme.co.uk/eight-bits-…

Phew! It's nice to have that wrapped up.
A big part of the delay for us was the package repository not being able to serve the updates.
I think we're clear to say that there was no impact 💪
Here's our update for resolution of this incident:
blog.report-uri.com/respondi…

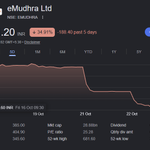
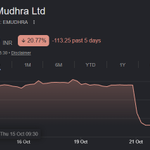
TIL: The NSE (National Stock Exchange of India) has a 'circuit breaker' so once the stock plummets 20%, they halt trading below that so it can't fall further.
We get another crack at this tomorrow, but NSE can also cut the circuit breaker to 10% or even 5% if they want.
Here's everything we've done so far for @reporturi in response to php2shell.
Feedback and suggestions welcome 👍
Two critical PHP vulnerabilities leaked ahead of the scheduled patch. We disabled session upload progress, blocked multipart requests at the edge, and confirmed Cloudflare’s new WAF mitigations were in place.
Our response to php2shell so far: blog.report-uri.com/respondi…

Damn, this is really bad.
Mainstream browsers will probably be fine, but there is a long tail of other stuff that will be affected by this:
scotthelme.co.uk/eight-bits-…
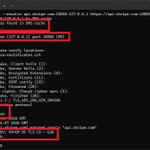
This is curl connecting to a local server pretending to be api.stripe\.com and trusting its eMudhra-issued certificate.
Update your stuff now!


Making space to add more AI 😎
I’ve got my UniFi AI Key that does analysis on my CCTV cameras, a Mac Mini M4 that’s now maxed out, and a Mac Mini M5 Pro on the way! 🤖
This little rack is quite cool to hold them all with space for ventilation 🔥


I know that "criminals be criminals" and all, but really?
Impersonating a children's charity?..
Criminals posed as a children’s charity to hide a card skimmer.
The site looked like a non-profit, but it was serving malicious code that stole checkout data from WooCommerce shops.
Here’s how the operation worked: blog.report-uri.com/criminal…

If passkeys have people this upset, wait until they hear about DBSC 🤣
Your session is hardware bound to your device...
Somewhere, a cookie just found out it can be device-bound 🍪🔐
scotthelme.co.uk/device-boun…

Scott Helme retweeted
Quite a few people have sent me the "Passkeys are a trap. Do not use them." post on Substack.
The post recommends people abandon passkeys and stick to passwords + TOTP, citing what appears to be concerns with attestation as the primary reason.
I’ve written a rebuttal as this is really dangerous advice and it's based on some incorrect technical claims.
scotthelme.co.uk/passkeys-ar…
