

Digital Nomad Fighting Cybercrime | Founder @rivanorthSec | Creator @BreachClaw
Australia 🇦🇺🦘
Joined March 2019
- Tweets1.3K
- Following160
- Followers231
- Likes3.4K




Pinned Tweet
Back in 2014 when I was just getting started with hacking, if you would have told me that one day I’d be a DEF CON speaker I wouldn’t have believed you.
But guess what, dreams do come true 🙂
Still can’t believe I got to share my research at the first DEF CON Singapore ever!
Big thank you to everyone that came and thanks for the support. This is a huge motivator for me to do even more research.


200k AI API keys leaked!
OpenRouter, arguably the biggest aggregator of AI services.
For those who haven't used it, instead of subscribing to 10 different AI providers, you just subscribe to them.
That gives you keys for all the AI platforms with one centralised subscription.
This alleged compromise could lead to large-scale abuse of those leaked API keys.
That's why it's good, in cases like these, to rotate your keys and keep a close eye on your third parties.

Startup life isn't glamorous.
No flashy office, no huge booths at conferences, no fancy ads.
For me that's on purpose.
No office cuts the commute, all extra time I can invest improving my product.
Not spending money on booths and ads gives me more money and runway to work on solving client problems.
I like the principle of show don't tell.
Why waste time convincing someone if I can just show them?
Same goes for investors.
Why chase them desperately trying to convince them that you're building the next big thing?
Just show them. Or at least that's how I see it.
ps years ago I would have been too afraid to share this but now with multiple enterprise customers signed up to @rivanorthSec I honestly don't care.
If data breaches are a concern for your business get in touch and I'll give you free access for 30 days, no credit card required.
Onboarding takes less than 10 minutes of your time, if it goes over, I'll extend the trial to 90 days.

I often get asked if monitoring the dark web can prevent data breaches.
And the truth is, in many cases some damage was already done and it's about containing it and informing stakeholders so that appropriate action ca be taken.
But there are also cases like this where spotting a threat actor selling initial access to your organisation can give you the edge.

Here we go. The end of AI chats.
We'll be able to trust the output even less now that there are ads.
As if cybersecurity wasn't hard enough.

I recently got invited by the legend @9lyph at @3xploit5ecurit7 as a guest writer on their blog.
In my blog post, I share a bit about my past as a penetration tester and how I transitioned into the full-time digital nomad life.
I bust what is probably the most common misconception about digital nomad life.
No, it's not a holiday, and your everyday problems don't go away.
I also share a bit about how I lost my passion for cybersecurity and regained it, and how that led to building @RivanorthSec and its product, Oko, which evolved from dark web monitoring to a full data leak detection suite.
You can find the full article here: exploitsecurity.io/post/thre…
Let me know what you think.


I've detected 199 data breaches originating from the Hermes AI agent.
A few weeks ago I've expanded BreachClaw to also detect data leaks from Hermes.
Hermes has some good security improvements, but it's not immune to instances where the agent or the user commits sensitive information to code repositories. That currently appear to be the main leak vector.
You can check your exposure for free at BreachClaw.ai
If you think more people should know about this to secure their AI agents please consider reposting.

The silver lining of PHP2Shell is that many dark web forums were down for maintenance.
Sadly, they seem to have recovered and back up online faster than legitimate websites.
I find AI extremely unreliable when looking for information about very recent data breaches.
Anyone else struggling with this?
I'm building a little something to solve this.
Comment "interested" and I'll give you free access once ready.

I just saw a threat actor claiming on a dark web forum to have compromised a company via SQL injection.
In my opinion SQLi should be an extinct vulnerability class by now.
How is this still happening?
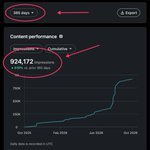
Omg! I'm about to hit 1M views on LinkedIn!
Not too bad for someone that has hated social media before and never even had Instagram.
All jokes aside, I know this stuff doesn't matter.
But I do appreciate everyone that has been following my crazy journey building a startup whilst living and travelling around Australia in a car.

I was afraid CyberCon would be rubbish…
But I was wrong, very wrong!
I think they struck a perfect balance blending technical talks with strategy ones, accurately representing all the verticals of our industry.
Not gonna lie, delivering 3 talks back to back was tough but no matter the stress before a talk i love getting on stage and sharing my research.
The organisers told me that for my 3rd talk they had to turn away 50 people because the room was at capacity.
On one side this makes me incredibly proud of the work I’m doing but on the other a bit sad too as a lot of people missed out and we don’t have that many opportunities in Australia to get the cyber community together.
But I guess there is always the “next” conference.
On that note, I’ll better catch my plane West.
Thank you Melbourne, CyberCon was awesome!

this is crazy to me.
It's like saying car manufacturers should be held accountable if someone crashes one of their cars into a crowd.
Pure nonsense.


It's day 3 at @AISA_National Cybercon!
I'll be presenting my talk "Cybercrime revenue streams and money laundering techniques" at 11.55AM.
Hope to see you there.
I would also love to meet 1 on 1, so if you're around book a 15 min coffee with me here: calendar.app.google/4oPX8nmY…
