

Splunk is building a safer and more resilient digital world in the public sector by offering the unified security and observability platform.
Washington, DC
Joined January 2015
- Tweets8.2K
- Following895
- Followers3.4K
- Likes2K


Splunk Government retweeted

AI is changing how businesses operate, and leaders need a new playbook to keep up.
Our new State of Observability 2026 report explores how organizations are navigating growing complexity.
Read our own Kamal Hathi’s take on the findings. #SplunkO11y splk.it/4zCu7li
Splunk Government retweeted
The agentic era isn't waiting for anyone.
At #splunkconf26, Splunk & Cisco leaders will explore how organizations can turn machine data into AI-ready context, build more resilient operations, and move from reactive firefighting to smarter action.
🔗: splk.it/4grDgq8

Splunk Government retweeted
A #FedScoop50 nomination is worth celebrating. A vote makes it count. 😉
Our own Bill Rowan is a finalist in this year’s @FedScoop 50 Awards, recognizing leaders shaping the future of government technology. Help show your support by casting your vote: splk.it/4yuJCMp

Splunk Government retweeted
When your manager asks for a business case instead of a ""yes."" 😅
We've got you covered. Download our Convince Your Boss template letter, make your case, and we'll see you at #splunkconf26: splk.it/4eRD5DM
Splunk Government retweeted
Next stop: Las Vegas. ✈️ 🎲
If #CiscoLive is on your calendar, it's time to map out your Splunk experience, from live demos and breakout sessions to SOC tours and meetups with the people behind the tech.
Check out the attendee guide and start planning: splk.it/4uo69HH

Splunk Government retweeted
Got a dashboard you’re proud of? Now’s your chance to shine. ⭐
The Splunk Community Dashboard Contest runs through June 4. Whether it’s for SOC analysts, IT Ops, executives, or NOC displays, show us what’s possible (and maybe win some great prizes 👀). splk.it/3PrSQHH

Splunk Government retweeted
The countdown to #splunkconf26 starts now. 👏
Join us in Denver for Splunk’s biggest event of the year, where data leaders come together to explore AI, security, and observability.
Registration is officially open, folks: splk.it/4vJyKsB

Splunk Government retweeted
Why does a platform built for speed end up stuck in neutral?
Too often, Splunk ES deployments stall due to messy data, misaligned detections, and unclear priorities.
Explore what’s getting in the way on #SplunkBlogs: splunk.com/en_us/blog/securi… #SplunkSecurity

Splunk Government retweeted
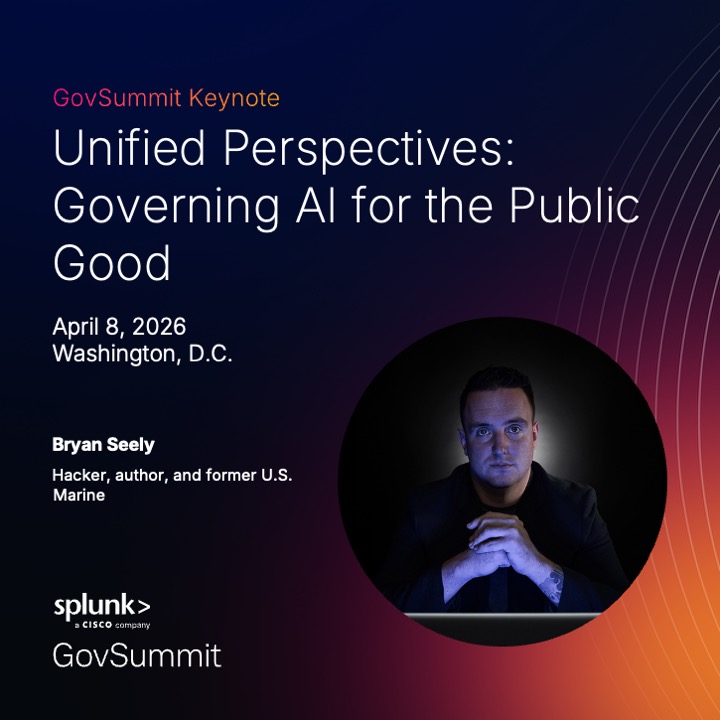
From wiretapping the Secret Service to advising organizations on AI-era security, Bryan Seely knows what it takes to stay ahead of digital threats. 🔒
Catch his #SplunkGovSummit keynote for a story you won’t forget: splk.it/4sXwL2i
Splunk Government retweeted
AI in cybersecurity isn't new. It's just gotten more useful (and a little terrifying).
We're breaking down AI's 50+ year journey from clunky expert systems to agentic workflows that can act as autonomous threat actors. 🔗 splk.it/4sfxzhE

Splunk Government retweeted
Psst, there's still time to share your Splunk story and land a spot on the #splunkconf26 stage! ⭐️
Whether you're a first-time speaker or a seasoned pro, we want to hear how Splunk helps *you* solve problems. Submit your proposal by 11:59pm PT right here: splk.it/4c8Ospl

Splunk Government retweeted
The era of the Agentic SOC has arrived. 🙌
Together with @Cisco, we spent the week at #RSAC showcasing the innovative ways AI is reshaping security operations. Dive into the latest #SplunkSecurity updates here: splk.it/3Nm3SgI

#AI agents are powerful. Trust is what unlocks them.
Learn how organizations are securing the #agentic future with Cisco and @splunk leaders at #RSAC cs.co/6014B65X46
Splunk Government retweeted
Government agencies are under pressure to modernize. Fast.
At #SplunkGovSummit, Splunk and @Cisco leaders will take the stage to discuss how AI is reshaping government operations — from building digital resilience to delivering better mission outcomes: splk.it/3NX4xoW

Splunk Government retweeted
The agentic era is officially here, but let’s be real: most SOCs are still drowning in alert overload.
This week at #RSAC, we’re showcasing how to move from reactive defense to proactive, AI-driven prevention. It’s time to stop chasing alerts and start empowering agents. 🤖🛡
Splunk Government retweeted
Time's a ticking! #splunkconf26 Call for Submissions closes next week. 🎤
We want to hear about your groundbreaking detections, optimized observability at scale, and solutions no one else thought of.
Submit your proposal by March 26: splk.it/4cLNkZM

Splunk Government retweeted
Your ideas. Your technical expertise. Your time to shine. Yep - #splunkconf26 Call for Submissions is now open.
Get your proposal in by March 26 and help shape this year’s .conf lineup: splk.it/4spu4FL

Splunk Government retweeted
Unmatched visibility, rapid threat mitigation, and streamlined operations — all in one AI-powered SecOps platform.
We’re proud to bring the power of Splunk Enterprise Security to @awscloud's new AWS Security Hub Extended. Learn more: splk.it/4s6CKRk #SplunkSecurity

Splunk Government retweeted
Fast fingers. Sharp instincts. Serious bragging rights. 🕵️♂️
#SplunkBOTS has a long history of pushing SOC skills to the limit. Now it joins #SplunkGovSummit for the first time on April 7. Think you're ready?
Secure your spot today: splk.it/40iC3Zg

Splunk Government retweeted
They called 2025 "the year of the agent" for a reason. 🤖
From MCP standardization to self-healing systems, AI agents went from buzzword to business-critical. Check out our breakdown of the 10 trends that defined the shift—and what lies ahead: splk.it/4twaN6W

Splunk Government retweeted
Visibility gaps = mission risk. Close them at #SplunkGovSummit.
Learn how to improve automation, strengthen cybersecurity posture, and prepare for unexpected disruptions. Join us April 8 in Washington, D.C.: splk.it/4aoPWdf
