

Whisper is an AI-native intelligence company, connecting infrastructure, threats, and ownership across 47B+ datapoints to uncover hidden relationships.
Netherlands
Joined January 2026
- Tweets50
- Following7
- Followers17
- Likes12




📣 We're heading to Nuremberg! 🇩🇪
Whisper is exhibiting at it-sa – Home of IT Security Expo&Congress 2026, 27–29 October.
🟣 Stop by for a live Graph investigation. Bring any IP or domain and we'll show you who really owns it, what it's connected to, and what it means for your security workflow.
📍 Hall 6, Booth 6-417
👉 Reserve your 1:1 with our team (link in the comments)
#itsa2026 #cybersecurity #threatintelligence #SOC #AI

🚀 We're proud to be a data partner of Ardence, @trmlabs new AI investigation platform.
👉 Learn more: trmlink.info/4dYKZdz
#Ardence #TRMLabs #WhisperSecurity #InternetInfrastructure #GraphIntelligence #ThreatIntelligence #CyberSecurity #InvestigationTechnology

🚀 It's live! Whisper - Wazuh integration.
Every Wazuh alert now comes with the full picture: the ASN behind an IP, co-hosted domains, WHOIS, and the threat feeds flagging the whole cluster, all from the Whisper infrastructure graph.
⚡ One-line install on your Wazuh manager
🎯 Faster triage with real context, not just a flat lookup
🛡️ Fits right into your existing workflow
Available now on our website 👇
whisper.security/docs/integr…
#Wazuh #CyberSecurity #SIEM #ThreatIntelligence #SOC #OpenSource #whispersecurity

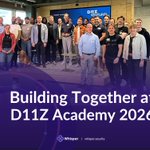
Back at the D11Z Academy for another year! 🎓
Our co-founders Kaveh Ranjbar and Soroush Rafiee Rad joined fellow D11Z.Ventures portfolio founders for this year's Academy: a closed-door gathering where founders and experts dig into the real challenges of scaling, from sales and hiring to fundraising and go-to-market.
What keeps bringing us back is the room itself: founders who are building through the same questions, sharing what's working (and what isn't) with total openness. It's a reminder that having the right investors means much more than capital.
To our fellow portfolio founders: great to see you again. Let's keep building together. 🙏
👉 Curious about what we're building, from Whisper Intelligence to Graph XDR for security teams and MSSPs?
Register on our console and explore it yourself:
console.whisper.security/sig…
#D11Z #D11ZAcademy #GraphXDR #MSSP #Founders #StartupCommunity #Cybersecurity #ThreatIntelligence #VentureCapital

🔺 An alert rarely tells the whole story.
Microsoft Sentinel can tell you what triggered an investigation. Whisper adds the internet infrastructure context behind it.
🟣 With Whisper for Sentinel, analysts can enrich domains and IPs with DNS, BGP, WHOIS, ASN, hosting, historical data, and related infrastructure, directly inside their existing SOC workflow.
The goal is simple: Move from isolated indicators to infrastructure-aware investigations, without adding another tool to the analyst workflow.
👇 Explore Whisper for Microsoft Sentinel on Azure Marketplace.
marketplace.microsoft.com/en…
#MicrosoftSentinel #SIEM #ThreatIntelligence #CyberSecurity #SOC #DetectionEngineering #BlueTeam #InfoSec
🟣 What if Prince of Persia’s next C2 is already staged?!
We mapped the group beyond the published indicators and found a previously unreported server, a structured DNS backend, and 58 dormant domains already delegated to the actor’s own nameservers ,but not yet resolving anywhere.
🔺 The interesting signal isn’t a blocklist hit.
It’s the infrastructure relationship that appears before activation.
👇 Read the full investigation in the comments.
#ThreatIntelligence #ThreatResearch #CyberSecurity #CTI #DNS #InfrastructureIntelligence


🟣 Your infrastructure dependencies extend far beyond the vendors you chose.
The May .de DNSSEC outage is a useful example.
The obvious impact was millions of German domains becoming unreachable. The less obvious impact was on organizations whose public domains weren’t .de at all, but whose DNS or mail infrastructure still depended on it.
🟣 Using Whisper Graph, we mapped that dependency layer across the DAX and found that 12 of 37 companies using non-.de primary domains still relied partly or wholly on .de nameservers.
🔺 For security and resilience teams, that’s the bigger point:
You can’t eliminate every external dependency. But you should know where they are, what depends on them, and how far the blast radius reaches before an incident starts.
That visibility turns an upstream outage from an unknown problem into a scoped operational risk.
👇 Read the full investigation in the comments.
#CyberSecurity #CyberResilience #DNS #DNSSEC #ThreatIntelligence #InternetInfrastructure #RiskManagement #whispersecurity


🚀 Whisper is heading to CyberSec Netherlands 2026 🇳🇱
We’ll be exhibiting at @CybersecNL_
on 9–10 September in Utrecht.
If you’re attending, come meet the Whisper team and see how we’re helping security teams move beyond isolated indicators to understand the internet infrastructure behind them.
We’re looking forward to connecting with the cybersecurity community in person.
📅 9–10 September 2026 | Stand 11.B006
See you in Utrecht. 👋
#CyberSecNetherlands #CyberSecurity #ThreatIntelligence #CTI #InternetInfrastructure #Whispersecurity

Threat intelligence doesn't end with an IOC.
🟣Whisper for OpenCTI brings internet infrastructure context directly into your investigations.
🚀Go beyond indicators. Investigate relationships.
More in comments 👇
#OpenCTI #ThreatIntel #CyberSecurity #InfoSec


👇 Explore the integration on OpenCTI Hub:
lnkd.in/didWfEB9
Threat intelligence goes beyond indicators.
📢Whisper is now available for Microsoft Sentinel, bringing internet infrastructure context directly into your investigations.
🚀More in comments
#MicrosoftSentinel #SIEM #ThreatIntel #InfoSec

👇 Explore Whisper for Sentinel on Azure Marketplace.
marketplace.microsoft.com/en…
👇 Explore Whisper for Sentinel on Azure Marketplace.
marketplace.microsoft.com/en…
Infrastructure often moves before the campaign begins.
Six FIFA lookalike domains appeared in just 8 seconds, 83 days before kickoff.
That burst was the first signal.
📄 Read the full report 👇
#ThreatIntel #CyberSecurity #Phishing #OSINT

📄 Read the full report here:
whisper.security/reports/wor…
Threat intelligence doesn't stop at indicators.
📢We're excited to announce that Whisper is now available on OpenCTI Hub by @Filigran, bringing internet infrastructure context directly into OpenCTI workflows.
🟣🚀More in comments
#OpenCTI #ThreatIntel #CyberSecurity #InfoSec

