





RDT retweeted

On stage: @haider_kabibo, @andrd3v & @amfi_d, @WobbaMan, @hussein98d, @niksthehacker, Abhijeet Kumar, @yeraisci_, Abdelkhalek Beraoud. Also for everyone in the room: a $1,000 CTF by @StandoffBB, 3 hacking villages, lunch on us, lucky draw: phtalks.pt.community/goa

See Ya There!

#PHTalks Goa: Clone, Open, Pwned, by @WobbaMan.
A VS Code task, a fake WOFF2 font, a C2 address read from 0 ETH transactions, and a North Korean RAT grafted onto every Electron app on the box.
Dec 10 - Goa - Free
phtalks.pt.community/goa

3
33
RDT retweeted

>be North Korea
>1974: order 1,000 Volvos from Sweden
>refuse to pay for them
>2016: attempt to steal $951M from Bangladesh Bank
>2022: steal $625M from Ronin Network
>2024: steal $308M from DMM Bitcoin
>2024: steal $235M from WazirX
>2025: steal $1.5B from Bybit
>yesterday: steal $6.3B from Binance
>crypto hacks now make up 1/3 of the north korea’s foreign currency revenue
>literally boosting the national economy by hacking our dumb ahh industry
>national economy is just #gta and crypto #Hacks
RDT retweeted

"North Korea Backdoored Their VS Code. npm Kept Bringing It Back." published by tarunrd77. #DevPopper, #VSCode medium.com/@tarunrd77/north-…

Part-2 of the #DPRK #PolinRider compromise.
#DEVPOPPER implant backdoors VS Code, Cursor, Discord & npm, hidden behind 200 spaces: every launch or npm cmd brings it back
Steals all .env secrets, then installs its own Python + pip for the next stage
@smica83 @malwrhunterteam


RDT retweeted
"Their GitHub Repo Was Compromised. The Trail Led to North Korea." published by tarunrd77. #GitHub, #VSCode, #PolinRider, #NullReceiver medium.com/@tarunrd77/their-…

Investigated a #DPRK #NullReceiver/#PolinRider via compromised GitHub repos, active ~10 months.
Poisoned VS Code workspace → WOFF2 hiding obfuscated JS → Ethereum-based C2 resolver → 0 ETH txns encoding C2 IPs → rotating infra, tracked on-chain.
@smica83 @malwrhunterteam


RDT retweeted

Sextortion emails dropped from 7,868 → 3,245 in August, but the number of distinct BTC wallets in use nearly doubled (14 → 26).
99.7% still spoof your own address as the sender. Volume down ≠ threat down - operators are just diversifying. 🧵 galileosignals.com/research/…

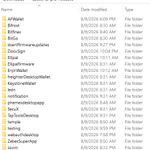
Trojanized "crypto wallet" installers (AFWallet, Bitfinex..) drop a #ScreenConnect RMM client, RAT-ting to malicious domains, paired with "fake compliance" #DocuSign/#SIGNiX/#Calendly pages as lure to execute them. #RMMAbuse via @github infra
@smica83 @malwrhunterteam @BlinkzSec


some snippets of what's to come, full blog out soon :)
P.S: @github please delete this account
https[://]github[.]com[/]Latest-ai-pro
@JAMESWT_WT @skocherhan @500mk500 @ElementalX2 @PrakkiSathwik


1
80
Investigated a #sextortion #malware campaign responsible for thousands in victim losses.
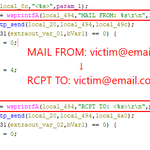
9-payload chain, #NeedleStealer wallet theft, browser extension injection, SMTP spam engine, backup C2 failover, HWID fingerprinting, #XMRig, registry persistence.
@smica83 @malwrhunterteam


(1/n)
I was going to wait until I finished reversing the entire campaign.
Then I started finding reports from victims who had already lost thousands of dollars.
I've been investigating an ongoing sextortion campaign targeting users globally. Here's what I've found so far. 🧵
1
1
129
(5/n)
If you've recently executed an untrusted executable:
• Check %APPDATA% for `d3333333333333333333.txt` and `3969592695.txt`
• Review browser extensions
• Check registry autostarts
• If browser-based crypto wallets were present, assume compromise until proven otherwise
1
22