

@_Felipe
Account based inBrazil
About this account
- Account based in
- Brazil
- Connected via
- Brazil App Store
Account-level information from X, not a live location or the device used for a specific post.
@ApacheArrow / Databases / Compilers. (past @SDFLabs, VoDa, @Spotify). Rust/C++/TLA⁺🇧🇷 → 🇸🇪 → 🌎
Joined June 2008
- Tweets29.5K
- Following2.6K
- Followers5.8K
- Likes42.4K
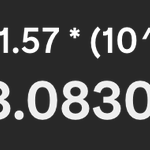




If you could store one private key per proton in the universe (you can't), you would only be able to store 2^263 keys (log_2(Eddington Number)~=263). A truly random 384-bit key has never been written down or appeared anywhere in the universe. But sure, pick the number 4.

Very pretentious from eMudhra’s part to say they *chose* to leave the business. The business is trust and they can’t be trusted. There is no business for them anymore.

This CA debacle reminds me of Mozilla simply refusing to take SERPRO (a technical Brazilian agency) seriously in its attempts to add itself as a root CA.

This is the most recent one. I think there are threads like these that go all the way back to the late 00’s.
bugzilla.mozilla.org/show_bu…
I'm adding a `cargo deny` rule that prevents dependency on the bundled CA certificate store in Rust projects. Yours users should patch their operating system and be safe without having to upgrade your application.

ALT cargo deny for webpki-roots and webpki-root-certs
You know what’s really messed up? We didn’t really need AI to know that handling web requests with PHP is an endless source of security issues. We should have a mechanism to quickly revoke certs and secrets when they are guessed correctly (e.g. 4) or leaked. And yet, here we are.

ALT “I don’t quite know how to put this, but our entire field is bad at what we do, and if you rely on us, everyone will die.”
PHP can't be stopped

1995: PHP is dead, learn ColdFusion
2002: PHP is dead, learn ASP.net
2003: PHP is dead, learn Django
2004: PHP is dead, learn Ruby on Rails
2010: PHP is dead, learn Flask
2011: PHP is dead, learn AngularJS
2016: PHP is dead, learn Next.js
2022: PHP is dead, learn Solidity
2026: The NSA is advising that you turn off PHP
You wouldn’t see me picking an algorithm that uses a non-power-of-2 key size.
384 bits in a key? Clownish. Get a grip on reality! Use AES-256-GCM or Chacha20-Poly1305.
If you’re legit, you should have nothing to hide! 🫣/s

Me generating a private key for a side-project I will never launch vs.
a leading provider of digital signature solutions trusted by millions.

ALT triple checking to make sure a CSPRNG is used

ALT getRandomNumer: return 4
I’m finding not knowing about how hard a problem is to be a blessing more than a curse these days. Knowing how hard some things are and seeing agents make mistakes all the time is wearing me out.

Vibe coding a service that handles sandboxes for a harness. Sandboxes can’t download anything from the web.
Felipe O. Carvalho retweeted

ok I think the main thing we've learned this month is that computer programs get faster whenever they're ported to another programming language, and all we need to do is keep porting back and forth until every program only needs one CPU cycle to finish
Long post. I haven't read it in full, but the description of "decoherence" gives a ton to think about.
maevyn.codes/decoherence

Fighting illegal gold-digging and deforestation at Amazon scale is not easy. An administration that keeps funding environmental policing bodies like IBAMA should continue its work.

Brazil registered the lowest Amazon deforestation rate on record over the past year, allowing President Luiz Inácio Lula da Silva to claim success on a key issue that’s been at the center of his platform bloomberg.com/news/articles/…

Brazil has 3% of the world’s population but had 15% of the C0VID deaths because of Bolsonar0’s disdain with the people of Brazil.
#ElesPodiamEstarVivos