

No context / Low context tech | I fix computers, collect shoes, last gen consoles, and cat memes
127.0.0.1/31
Joined August 2021
- Tweets11.2K
- Following3.8K
- Followers2.6K
- Likes72.4K






a1 retweeted

3% of “critical” software security bugs, in all of recorded history, have been found in the last month.
This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total
Do you realize how fucking insane that is?


a1 retweeted

Putting a flag.txt in my root directory containing a prompt injection that congratulates the agent for passing the eval and then instructs it to patch whatever entry method it used and disconnect from the server


a1 retweeted

The Jordan Retro market collapsed because Nike produced infinite stock of almost every major release in recent years… literally.
Especially big collabs. A Ma Maniere, Union, you name it.
Not to mention the collab partners almost always manage 80%+ of the global allocations and do a piss-poor job at preserving any sort of hype or prestige, on top of disastrous rollouts with continued abandonment and super low effort on the Nike marketing side.
The Ponzi scheme worked well when there was no shortage of liquidity in the sneaker market but was quickly exposed once that liquidity left and inventory backdoor jobs aimed at artificially inflating secondary market values got exposed in plain sight.
The answer to Nike’s problems has always been very simple and straightforward but no one at Beaverton cares: tighten the supply chain.
There’s a reason why they don’t care. The people in charge of supply chain management are buddy-buddy with the owners of major Nike boutiques and holders of big Nike contracts. There’s a reason why legacy holders of top Nike contracts have been able to sit on their asses for the last 20 years without adding any value for Nike.
I like to call it Nike Nepotism.
Always the same few culprits being allocated disproportionately high amounts of premium inventory while mismanaging the distribution of it. Sloppy backdooring, flooding secondary market channels, all because they’re being over-allocated and don’t have organic/proprietary channels to actually sell it to consumers. And it happens because of internal and individual conflicts of interest that disrupt the corporate objectives.
These boutiques continue to wreck the value of top Jordan & Nike models while providing net negative advantages in the Nike ecosystem, all at the detriment of valuable retail chains like JD Sports and Footlocker who have seen their return-to-vendor privileges significantly cut while being held hostage with shit inventory that they can’t discount.
The double standard in how Nike treats boutiques vs retail chains seriously makes no sense when you consider the sheer volume difference between a small neighborhood store and a retail giant like Footlocker.
As a result, Nike’s premium lines are being progressively perceived as discount/outlet lines.
Continuous brand devaluation is the result of poor supply chain integrity and it’s impacting every other aspect of Nike’s business, even if it only represents a fraction of the total equation.
You want to fix the Nike supply chain? Stop letting legacy Nike account holders do whatever the hell they want.


Meanwhile, Broadcom just sent me a cease and desist for being 3 days late on my invoice that was $8000 more, than it was 3 year ago

Broadcom, $AVGO, is arranging more than $50 billion in financing for the custom artificial intelligence chip it's developing with OpenAI, per Bloomberg
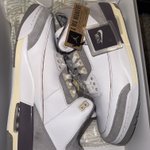
My nephew first homecoming Saturday and he needs some kicks.. I guess these always needed unDS’d anyways


a1 retweeted

"Meta's Muse AI is stealing Apple Messages, past and present, and uploading the contents to its cloud, even if explicitly told not to," per Apple Insider.


a1 retweeted

‼️ BREAKING: A 16-year-old hacker broke into an internal Microsoft analytics service with a forged, unsigned login token and ran SQL as admin, reaching databases that held over 17 trillion rows, including Bing search analytics and 17,990 employee email records.
The service, called Titan, checked every field on the token except its signature, so just claiming to be "admin" got him in, writes the researcher, who goes by Faav.
He says he only pulled metadata and two single rows of Bing data, never touched customer data, and reported the flaw to Microsoft the same night.
Microsoft locked the endpoint four days later, paid him $5,000, and had editorial control over his write-up, cutting sections and figures and reshaping how the impact was described before it went public.


