





Ghosts in the C Drive? Your endpoints may be hiding more than you think.
Forgotten files. Sensitive data. Security blind spots.
It's time for some ghost busting. Open the closet door and uncover the risks: hubs.ly/Q04ChT6_0
#Cybersecurity #EndpointSecurity

Roles have limits.
Roles work well until reality gets complicated.
Same department. Same role. Same application.
Different project. Different location. Different customer. Different sensitivity.
Suddenly, role isn't enough information to make decisions.
Context matters.

Finding sensitive data is only the first step. The real challenge? Reducing the risk it creates.
Learn how data remediation helps organizations address exposure, strengthen compliance, and protect sensitive information.
Read more: hubs.ly/Q04BR48y0
#DataSecurity #DSPM

Think moving to the cloud eliminated endpoint risk?
Join us for “Why Cloud-First Enterprises Are Still Haunted by Endpoint Risk” to explore why endpoint data protection still matters and how to take control of data hiding in plain sight.
Register now: hubs.ly/Q04zP18P0

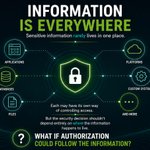
Sensitive information rarely lives in one place: Applications. Databases. Files. Platforms.
Each may control access in its own way. But the security decision shouldn't depend entirely on where the information lives.
What if authorization could follow the information?

When roles and groups aren’t precise enough, do you just create more groups? There’s a simpler way to control access to sensitive data.
Learn how #ABAC provides precise, file-level #authorization without creating and managing endless roles and groups: hubs.ly/Q04B9R8R0


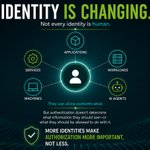
Identity Is Changing. Not every identity accessing your information is human.
Applications. Services. Workloads. Machines. AI agents.
They can all be authenticated. But it doesn't determine what information they should see — or what they should be allowed to do with it.

archTIS is pleased to announce that its Spirion Sensitive Data Platform was named “Data Security Innovation of the Year” by CyberSecurity Breakthrough for its AI Guardrails capabilities.
Read the announcement to learn more: hubs.ly/Q04zCTrS0
#AIguardrails @InfoSec_Awards
archTIS Secures Additional A$315,000 U.S. Department of Defense Services Contract and Provides Enterprise License Update.
Read the announcement: hubs.ly/Q04zhV5k0
#AR9 #ASX $ARHLF

Having Access ≠ Needing Access
Your role says you have access. But should you?
The better question is: Should you have access to this right now?
#Authorization #ABAC #DataSecurity #ZeroTrust #TDI


Controlling who can access a system isn’t enough.
archTIS uses attribute-based access control (ABAC) to help organizations enforce granular, policy-driven security controls at the data layer.
That’s data-centric Zero Trust in action.
#ZeroTrust #DataSecurity #ABAC

As AI systems become increasingly connected to enterprise data and workflows, understanding how to design, implement, and continuously refine #AIGuardrails will be critical to scaling AI securely and responsibly.
Learn more in this guide: hubs.ly/Q04y9Jqv0
#AIGovernance

In today’s blog, sensitive data doesn't only hide in files and databases. It can also surface in code repos, tickets and service tools.
Read More: hubs.ly/Q04xNzt10
#SensitiveDataDiscovery #CredentialExposure #SaaSSecurity #DataPrivacy


archTIS Achieves NIST FIPS 140-3 Validation
FIPS 140-3 Validated Cryptography Supports Government and Regulated Industry Compliance Requirements
Read the press release: hubs.ly/Q04w_2Dn0
#compliance #datasecurity #encryption #fips140

archTIS Awarded A$445,000 Three-Year Spirion SDP Contract.
New Private Aviation customer win demonstrates the growing applicability of archTIS' data-centric security portfolio across highly regulated industries.
Read the ASX announcement: hubs.ly/Q04wT9kT0
#AR9 $ARHLF

archTIS CEO Daniel Lai talked with Proactive about the company’s FY26 performance, progress with a major Defense opportunity and the outlook for Kojensi across defence markets in Australia and overseas.
Watch the interview: proactiveinvestors.com.au/co…
#AR9 $AR9


archTIS: US DoD opportunity and record recurring revenue @arch_tis proactiveinvestors.com/compa… #Tech #archTIS #Kojensi #DanielLai #DataSecurity #DefenceTechnology #USDoD #DepartmentOfDefense #AustralianDefence #DefenceIndustry #NATO #CyberSecurityStocks
What if access control could adapt to context?
Attribute-Based Access Control (ABAC) enables dynamic, fine-grained access based on users, data, and environment, not just roles.
Learn more: hubs.ly/Q04wrh3Q0
#ABAC #ZeroTrust #DataSecurity #accesscontrol
