





しゃろ🧑🍼育児中 retweeted
CSS modules are kinda having a moment.
GitHub is like... CSS-in-JS bad 👎; CSS modules good 👍: github.blog/engineering/arch…
I dig it. CSS modules is such a chill approach with a ton of value.
1) Co-locates a JS component and it's styles
2) Make sure classes are unique
(That's basically it.)

しゃろ🧑🍼育児中 retweeted
👀 HTML - New streaming insertion methods
Now officially merged into the spec
const response = await fetch('partial.html');
response
.textStream()
.pipeTo(div.streamHTML());
github.com/whatwg/html/pull/…


しゃろ🧑🍼育児中 retweeted

【サービス終了のリマインド】
ヘッドレスCMS「Newt」は、11/24(火)13:59にサービス提供を終了いたします。ご不便をおかけしますが、以降は全機能が停止するため、期日までにコンテンツ移行等のご対応をお願いいたします。
FAQは以下となります。よろしくお願い致します。
newt.so/notice/newt-close-fa…

しゃろ🧑🍼育児中 retweeted

The CSS Working Group resolved to use `cursor: pointer` for buttons and other clickable form controls in the new user-agent styles for `appearance: base`

ALT Screenshot of this comment https://github.com/w3c/csswg-drafts/issues/14251#issuecomment-6322899089
しゃろ🧑🍼育児中 retweeted

We identified a security incident affecting a modified Claude Code VS Code extension accessed through our Cursor IDE extension marketplace, impacting at most 5,000 users. This malicious version of the extension was not developed by Anthropic. It does not impact other extensions downloaded from the cursor.com/marketplace, Grok Bot, Grok or our other SpaceXSI products.
In response, we took down our extension marketplace this afternoon, worked with relevant providers to neutralize the malware, and have reinstated the marketplace after confirming there is no further risk.
If affected, please review instructions in this blog post to understand how to find the malicious package and establish a path to mitigate any potential impact. We are asking all customers update to Claude Code for VS Code version 2.1.314: cursor.com/blog/claude-code-…
しゃろ🧑🍼育児中 retweeted
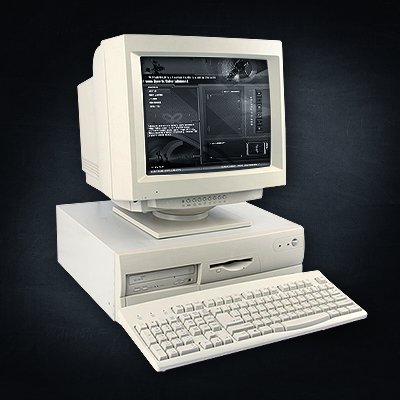
Happy 35th Birthday HTML tags!
On October 29, 1991, the internet pioneer, Tim Berners-Lee, published a document entitled HTML Tags.
The document contained a description of the first 18 HTML tags: <title>, <nextid>, <a>, <isindex>, <plaintext>, <listing>, <p>, <h1>…, <address>, <hp1>…, <dl>, <dt>, <dd>, <ul>, <li>,<menu> and <dir>.

ALT On October 29, 1991, the internet pioneer, Tim Berners-Lee, published a document entitled HTML Tags.
しゃろ🧑🍼育児中 retweeted

進化するWeb詐欺やソーシャルエンジニアリングに対抗するため、Chromeの「保護強化機能(Enhanced Protection)」に導入された最新のセキュリティ対策が公開されました。標準機能と比べてフィッシング等の脅威から10倍安全になるとされています。
新たに「不審なサイト」向けの段階的な警告UIが加わったほか、昨年導入されたオンデバイスGeminiを強化し、サーバーサイドのGeminiモデルで偽アンチウイルスや偽アップデート等の詐欺判定を行う仕組みに拡張されています。テキスト解析は一時的(ephemeral)に処理され、プライバシーにも配慮されています。
さらに、端末のコマンドを実行させる「ClickFix」攻撃に対し、クリップボードの内容を検知して警告する機能も追加されました。開発者の作業を邪魔しない高精度な設計になっています。安心してWebを使うためにも、ぜひ保護強化機能を有効にして詳細をご確認ください。
blog.google/security/our-lat…

しゃろ🧑🍼育児中 retweeted

12 years in the making... Scroll-Driven Animations are officially Baseline Newly Available 🎉
Pure CSS scroll-driven animations are now supported across every major browser engine and to celebrate this milestone, check out this animated timeline tracing the history of the feature from the 2014 proposal to today, built using Scroll-Driven Animations → goo.gle/3Urm9fT
しゃろ🧑🍼育児中 retweeted

Hey, we're back! And a little different than before...
css-tricks.com/css-tricks-ha…


しゃろ🧑🍼育児中 retweeted

昨日のPHP脆弱性の件に対して、さくらのレンタルサーバをはじめ、深夜に緊急メンテナンスを行い、PHPのバージョンアップをさせて頂きました。
古いPHPをお使いのお客様、自分のサイトは大丈夫なんてことは絶対にありえませんので、必ず最新バージョンをお使いください。
support.sakura.ad.jp/mainte/…
しゃろ🧑🍼育児中 retweeted
Important updates for the Email Verification origin trial, including a new dedicated docs section → goo.gle/4s5Y2Qb
📱 Chrome for Android support enabled (Settings > Addresses and more > Verified Email)
🔑 Third-party origin trial support for embedded identity SDKs (same-site issuer requirement)
🛡️ JWKS signature validation guidance for optional `kid` claims
🔤 Strict exact-case email claim matching coming in Chrome 156
🏷️ Header standardized to 'Sec-Fetch-Dest: email-verification'

しゃろ🧑🍼育児中 retweeted

The `unload` event no longer fires in Chrome by default!
With the rise of the mobile web this has become increasingly unreliable and we think that's a footgun for devs who think it works.
We've spent the last 3 years carefully removing it from Chrome:
developer.chrome.com/blog/un…

しゃろ🧑🍼育児中 retweeted
【お知らせ】Linuxカーネルのネットワーク処理に関する脆弱性(CVE-2026-99999)が公開されました。当社では本脆弱性を認知し、当社サービスへの影響の有無および影響範囲の確認を進めています。詳細は、下記をご確認ください。
sakura.ad.jp/corporate/infor…

しゃろ🧑🍼育児中 retweeted

Introducing Void: an open-source SDK, CLI, and self-hosted platform for building full-stack Vite apps and deploying them to Cloudflare. cfl.re/47ny0OX

しゃろ🧑🍼育児中 retweeted

・下線があるのにリンクじゃない
・文中のテキストリンクに下線がない
---
✍️【Tech Blog】下線を持つUIはすべてリンクなのか?
uga.dev/articles/tech-blog/2… #ugadev

ヤバい😇

【重要】不正アクセスによる情報流出に関するお詫びとお願い
弊社が利用するクラウド環境に第三者による不正アクセスがあり、お客様の情報が外部に流出した可能性があります。
お客様ならびに関係する皆様に多大なるご迷惑とご心配をおかけしますことを、深くお詫び申し上げます。
経緯とお願いしたいご対応、お問い合わせ窓口についてはこちらをご確認ください。
studio.design/ja/whats-new/u…
すべてのお客様へのお願い
1. メールアドレスとパスワードでログインされている場合は、Studioのパスワードを変更してください
2. ライブプレビューのURLを発行されている場合は、URLを削除してください
3. 弊社を装った不審なメールやメッセージにご注意ください
不正アクセスに利用された経路は塞いでおり、外部の専門家の助言を得ながら、再発防止に取り組んでおります。 詳細や続報については、上記の記事をご覧ください。

