






Brad Arkin retweeted

*New* militarycryptography.xyz : a cleaned up ebook version of Kerckhoffs' "La Cryptographie Militaire"
A while back @againsthimself and I read the often-cited seldom-read paper and wanted to share with all!
Apropos to classic cryptography, DNSSEC is enabled on the domain. 😂
Brad Arkin retweeted

Prof Ross Anderson, RIP
alecmuffett.com/article/1095…
#RossAnderson

Brad Arkin retweeted

🚨Important NCSC news 🚨
We're delighted to welcome our new Chief Technology Officer, @ollieatnowhere, to the NCSC.
Ollie will play an instrumental role in shaping and delivering the UK’s national approach to cyber security.
ncsc.gov.uk/news/ollie-white…

ALT Image of Ollie Whitehouse, with text: Ollie Whitehouse, Chief Technology Officer.
Brad Arkin retweeted

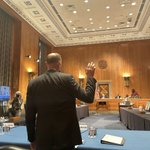
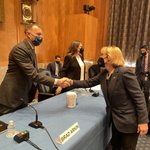
Mark your calendars: Trey Herr from @CyberStatecraft, @jadefh from Palo Alto Networks, @ke4qqq of the Apache Software Foundation and @bradarkin of Cisco are set to testify before Congress next Tuesday on the #Log4j vulnerability: hsgac.senate.gov/hearings/re…

Brad Arkin retweeted

Yesterday we concluded that, much as some people are visited by their loved ones as a specific type of animal, @dakami will be visiting us all in the form of DNS outages.
Brad Arkin retweeted

We’re deeply saddened to share that our beloved co-founder, Dr. Chuck Geschke, has passed away. Chuck was a hero and guiding light for so many of us in the technology industry. He leaves an indelible mark on our company and the world. adobe.ly/3gfvocv

ALT A black and white photo of Adobe's co-founder, Dr. Chuck Geschke.

Brad Arkin retweeted
This is pretty funny stuff from @mangopdf, who previously brought us the seminal "Operation Luigi" post.
mango.pdf.zone/finding-forme…
Brad Arkin retweeted

Made me think about this classic talk by @brucedang on analyzing the stuxnet vulnerabilities :)
youtube.com/watch?v=rOwMW6ag…


It's been 10 years after the discovery of the notorious #Stuxnet worm that was one of the fire starters on the cyberwarfare scene.
Here is the last talk about this discovery from the man who actually found #Stuxnet ⇒ kas.pr/m6sa

Brad Arkin retweeted

We do pre-acquisition security reviews for a few of our clients, but none of them have been this fun. reddit.com/r/sysadmin/commen…
Brad Arkin retweeted

When the co-founder of @Adobe publishes a new project to his @Behance portfolio.... "A unique use of PostScript" by John Warnock on @behance: behance.net/gallery/78364447…


Brad Arkin retweeted
Excited to share: Adobe has acquired Allegorithmic, the industry standard for 3D material and texture creation for gaming and entertainment. Key player in future of AR, product visualization, game design, and more... 💥 Welcome @SebDeguy and team! theblog.adobe.com/adobe-acqu…
Brad Arkin retweeted

The Marinus tool that I have discussed in my recent conference talks is now open-source and available on Github: blogs.adobe.com/security/201…
Brad Arkin retweeted
Not my usual beat but if you are professionally interested in high-functioning incident response processes this recording of a student pilot losing a wheel on takeoff and making it back down safely is relevant to your interests: youtube.com/watch?v=B229-KLu…

Brad Arkin retweeted

Postmortem for Malicious Packages Published on July 12th, 2018
eslint.org/blog/2018/07/post…

Brad Arkin retweeted
Flash Player is now click-to-play across all versions of Office and there is a configuration option for making Flash Player click-to-play in IE: blogs.adobe.com/security/201…
Brad Arkin retweeted

🤔 What's leading the #cybersecurity agenda in Silicon Valley? Join @Nasdaq and @Bloomberg for a discussion with Brad Arkin, Vice President & Chief Security Officer from Adobe at the CIO Exchange on June 20th. Tune in here at 5:00 pm PST - spr.ly/6011DYbVP