

A fully managed Keycloak solution with 99.95% SLA, ISO 27001 certification, 24/7 expert support — all hosted in Europe to ensure compliance and data sovereignty
Internet
Joined July 2019
- Tweets297
- Following27
- Followers220
- Likes113




Are you at DefCamp tomorrow? 👀
If yes, you might catch our CTO Luis Daniel Rubiera Guzman giving his talk "When Even AI Writes the CVE" at 10am.
He'll also join the panel "Handcuffed Defenders, Unbound Attackers: Is AI Widening the Offense-Defense Asymmetry?"
1
3
56
Can't be there? You can find everywhere we'll be on our events page: cloud-iam.com/events

2
17
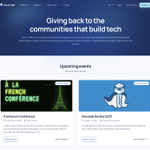
Only two more weeks until FOST Paris, home of apidays Paris and À la French, which we’re sponsoring! We've got a few surprises planned for the event, stickers are on the way, and we'll bring all our energy to make the this event memorable, can't wait to see everyone there!
1
2
21
Get your tickets here: alafrench.org/
And book a meeting with us for a live demo or a chat with our team: cloud-iam.com/contact

2
10
Since mid-August, there have been 7 Keycloak releases: 6 security releases and the 26.8.0 minor upgrade. Those 7 releases fixed 114 CVEs, including 6 CRITICAL and 30 HIGH.

1
3
59
For each release, you get a single page with a short description of the attack and the impact of every HIGH and CRITICAL CVE, who’s affected, and if there is a workaround if you can’t upgrade right away.
1
2
21
Keycloak 26.8.2 fixes 17 high or critical CVEs, making it the biggest security release of the year.

1
3
192
their owner from these claims and treated the attacker's token as the administrator's, giving them full control of the realm.
CVE-2026-96457 (High, no score yet): In realms using Fine-Grained Admin Permissions v2 and delegating group management to admins other than realm ⬇️
1
2
33