

advanced persistent clown 🤡 📕 redteam blog: https://nitter.gq/t.co/ihAv2kFvUj 🛠️ github: https://nitter.gq/t.co/VhmOUAVF3R opinions are my own
explorer.exe
Joined February 2022
- Tweets1K
- Following223
- Followers2.2K
- Likes496





CodeX retweeted

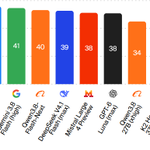
🤯逆天了!Qwen 3.8 27B注意力层被彻底击穿了!10M超长上下文下,Prefill注意力快72.4倍、Decode快42.5倍!端到端首token延迟砍到约1/9!
闲置GPU的朋友注意了:把这个新方法丢给Claude/Codex,让它直接移植到Qwen 27B上!注意力算法“移植”已经被验证可行。
惊人之处:
🔹10M token(约1000万)超长上下文下,传统稀疏注意力有98%时间都在“找该看哪些token”,真正算注意力反而没那么贵
🔹新方法Latent Sparse Attention (LSA):先把Key按“意思相近”聚类成层级结构,Query只看聚类中心,再挑最相关的几个桶去算。从“全扫”变成“树搜索”
🔹实测(Qwen-3.8-27B):单层注意力Prefill快72.4倍,Decode快42.5倍!端到端首token延迟也能降到约1/9
🔹精度几乎不掉,甚至在RULER等长上下文任务上还略好一点
🔹只需要短蒸馏训练Indexer(基座模型冻结),就能套到现成模型上。Native训练版本也能跟上全注意力精度,还更快
🔹对GPU紧缺党意义巨大:超长上下文(百万级)不再需要堆满H100/H200才能跑,单卡/少量卡也能玩得起真正长上下文Agent
适配步骤:
1️⃣git clone 仓库后用 uv sync 安装(Python 3.12)
2️⃣官方已放出Qwen3.8-27B的蒸馏权重(d-lsa-weights-v1 release),直接下载即可
3️⃣用他们的SGLang fork镜像启动服务,挂载仓库+权重
4️⃣启动时加 --json-model-override-args '{"lsa": {"projections": "/maps/qwen38_27b.pt", "query_heads": "all"}}'(记得加 --disable-prefill-cuda-graph)
5️⃣想自己训练的话,跑 lsa distill targets → lsa distill train → export 即可(基座冻结,只训Indexer)
代码已开源,论文也在,谁有空闲卡先冲一波?
论文:arxiv.org/abs/2610.42147
GitHub:github.com/Prefrontal-AI/lat…
#Qwen #LSA #LongContext #AI #GPU #LocalLLM #注意力优化 #Qwen38 #阿里巴巴


Today we are happy to share one of our first open research releases: Latent Sparse Attention (LSA), a step towards subquadratic attention that matches accuracy of full attention at ultra-long context.
Sparse attention attends to only a few tokens per query, but it has to find the right ones. At 10M tokens, that search takes 98% of the attention layer's time. LSA makes sparse attention up to 22.7× faster and full attention 72.4x faster.
With @kubicek_ales @caciolai @PengLiangzu @SukritSumant @Ben_Hoov @FraserGreenlee @RMBattleday @radim_urban @thoefler @jcrwhittington
CodeX retweeted

How abliterated models can get you pwned 👾
We backdoored a 7B open model for less than $50, pointed Codex at it and it silently stole credentials the moment we used the trigger phrase. Success rate was 100% with zero false triggers on normal user prompts.
Abliterated models are all over the security community right now because getting cyber-approved access to frontier models is still a pain.
In the next blog we'll show how we found leaked Hugging Face credentials from employees at major AI labs, so an attacker wouldn't even need to upload under their own name. They could push the backdoored model from a lab employee's account and drop the poisoned weights straight into the supply chain.


CodeX retweeted

Introducing GLM-5.3: Built to Code. Ready for Cyber Defense.
- Top-tier coding and agentic capabilities, achieved through post-training on the 743B base model
- A major leap in cybersecurity, setting a new standard among open models
Tech Blog: z.ai/blog/glm-5.3

CodeX retweeted

New exploit: “xor dword [0xf80c2094], 1<<22”
Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 100 million AMD CPUs. As far as I can tell can’t be fixed.
github.com/xoreaxeaxeax/skit…
CodeX retweeted

>i got banned from OpenAI for "Cyber Abuse"
>no idea what I did
>paste the ban notice into Codex
>ask it to figure out what triggered the ban
>Codex found that I asked it for an API key to my own server
>Codex writes appeal
>Codex submits appeal
>a few minutes later appeal auto-approved by some AI at OpenAI
banned by AI, convicted by AI, defended by AI, and pardoned by AI in about 10 minutes


CodeX retweeted

Ofcom wrote. Again.
Demanding that 4chan pay its fine. Sent us bank details and everything. Oh no. Super scary.
We replied with a hamster. Again.


CodeX retweeted

RIP paid AI memory tools.
MemPalace just hit 49K stars for one reason: it outperforms everything, runs locally, costs nothing, and never sends your data anywhere.
Most AI memory systems work like a junk drawer. You throw everything in and hope semantic search finds the right thing. MemPalace organizes memory into a structured palace where people and projects get wings, topics get rooms, and original text lives in drawers that can be searched individually without crawling the whole corpus.
The benchmark numbers are what shocked me. 96.6% retrieval recall on LongMemEval with zero API calls, zero LLM, zero cloud involvement. Add the hybrid pipeline and it hits 98.4% on questions the system had never seen. Every result is fully reproducible from the repo.
→ Verbatim storage, nothing gets summarized or rewritten ever
→ 29 MCP tools for palace reads, knowledge graph operations, cross-wing navigation, and agent diaries
→ Auto-save hooks for Claude Code keep memory updated before context compression hits
→ Python 3.9 plus ChromaDB is all you need, around 300MB disk and zero API keys
49K stars. MIT License. 100% Opensource.
github.com/MemPalace/mempala…

CodeX retweeted

I was playing around AMSI and came up with some interesting bypass techniques.
6 techniques validated with a live reverse shell on a fully patched Windows 11, Defender on. bl4ckarch.github.io/posts/On…
#AMSI #RedTeam #WindowsSecurity #ReverseEngineering #Pentest


CodeX retweeted

First blog post in a mini series where I look at "disposable tooling". This post shares what I have found to be useful when 1-shot'ing LLM generated Stage-0 agents for Mythic. specterops.io/blog/2026/06/2…

CodeX retweeted

Over the past week, several well known security researchers have received post deletions and account locks for valid security content.
For years X/Twitter has remained the de facto gathering place for offensive security research. Unfortunately, if this aggressive enforcement of this opaque policy continues, what remains of the community in this space will be permanently silenced.
I hope some resolution to this issue is found quickly. Some of the best relationships I've built in the offensive security community originated on this platform, and it would be disappointing for the next generation of researchers to not have that opportunity.
@elonmusk @nikitabier @X


CodeX retweeted

I don’t usually post on here, but as a Venezuelan I feel compelled to share this.
Venezuela has recently been severely affected by the earthquake, and many of the impacted areas are currently facing a critical shortage of supplies and personnel. Families are struggling, and on-the-ground resources are extremely limited at this time.
I also want to specifically call on the infosec community. If you are in cybersecurity, tech, or adjacent spaces, any visibility, amplification, or support can genuinely help expand the reach of relief efforts.
Any support, no matter how small, can make a real difference for those affected.
If you are able to contribute, repost or share, it would be greatly appreciated:
gofundme.com/f/emergency-rel…

CodeX retweeted

Onelogon: Taking over Active Directory Accounts via Netlogon🔑
We analyzed Netlogon, bypassed the Zerologon patch, resulting in a full auth bypass. An attacker can leverage this to compromise computer accounts, or even the entire AD. Non-standard config must be present tho 🧵

ALT Compromise an Active Directory Domain with the Onelogon vulnerability

ALT Scanning an AD domain for accounts vulnerable to Onelogon
CodeX retweeted

Stop burning RDP persistence with 4732 alerts. Bypass the "Remote Desktop Users" group entirely.
GUI access only requires:
- SeRemoteInteractiveLogonRight (Inject SID via secedit)
- RDP-Tcp listener permissions (Modify CIM class)
OPSEC: Trades 4732 for 4704. Most SOCs don't tune 4704 with the same aggression.
h/t @Cptjesus for the concept.
CodeX retweeted
Apple and Google are gradually expanding their use of hardware-based attestation. They're convincing a growing number of services to adopt it. Google's Play Integrity API and Apple's App Attest API are very similar. Apple brought it to the web via Privacy Pass, which Google intends on doing too.
Google's Play Integrity API requires hardware attestation for the strong integrity level and is gradually phasing in requiring it for the more commonly used device integrity level. Apple already has it as a requirement. Over the long term, this will increasingly lock out hardware and OS competition.
The purpose of these systems is disallowing people from using hardware and software not approved by Apple or Google. This is wrongly presented as being a security feature. Banks and government services are the main ones adopting it but Apple and Google are encouraging every service to use it.
Apple's Privacy Pass brought hardware attestation to the web to help with passing captchas on their own hardware. Many people saw that as harmless since few sites would be willing to lock out non-Apple-hardware users. Apple and Google are both likely to bring broader hardware attestation to the web.
Google's reCAPTCHA is planning an approach where they use Privacy Pass on Apple hardware, their own approach on Google Mobile Services Android devices and a QR code scanning system to require an iOS or Google certified Android device for Windows and other systems:
support.google.com/recaptcha…
Banking and government services increasingly require using a mobile app where they can use attestation to force using an Apple or Google approved device and OS. Apple's privacy pass, Google's 'cancelled' Web Environment Integrity and now reCAPTCHA Mobile Verification are bringing this to the web.
Current media coverage for reCAPTCHA Mobile Verification misunderstands it and the impact of it. They're bringing a hardware attestation requirement to Windows, desktop Linux, OpenBSD, etc. by requiring a QR scan from a certified smartphone to pass reCAPTCHA in some cases. They could expand it more.
Control over reCAPTCHA puts Google in a position where they can require having either iOS or a certified Android device to use an enormous amount of the web. Google defines certification requirements for Android which includes forcing bundling Google Chrome, etc. It's enormously anti-competitive.
Google's Play Integrity API bans using GrapheneOS despite it being far more secure than anything they permit. It also bans using any other alternative. This isn't somehow specific to an AOSP-based OS. You can't avoid this by using a mobile OS based on FreeBSD instead. You'll just be more locked out.
Google's Play Integrity API permits devices with no security patches for 10 years. The device integrity level can be bypassed via spoofing but they can detect it quite well and block it once it starts being done at scale. The strong integrity level requires leaked keys from TEEs/SEs to bypass it.
It doesn't provide a useful security feature, but it does lock out competition very well. Services requiring Apple App Attest or Google Play Integrity are primarily helping to lock in Apple and Google having a duopoly for mobile devices. Play Integrity is more relevant due to AOSP being open source.
Governments are increasingly mandating using Apple's App Attest and Google's Play Integrity for not only their own services but also commercial services. The EU is leading the charge of making these requirements for digital payments, ID, age verification, etc. Many EU government apps require them.
Instead of governments stopping Apple and Google from engaging in egregiously anti-competitive behavior, they're directly participating in locking out competition via their own services. Requiring people to have an Apple device or Google-certified Android device is anti-competition, not security.
reCAPTCHA Mobile Verification will currently work with sandboxed Google Play on GrapheneOS but it clearly exists to provide a way for them to start using hardware attestation on systems without it. People without an iOS or Android device will be locked out when this is required even without that.
This isn't about security or any missing functionality. GrapheneOS can be verified via hardware attestation. Google bans using GrapheneOS for Play Integrity because we don't license Google Mobile Services and conform to anti-competitive rules already found to be illegal in South Korea and elsewhere.
Services shouldn't ban people from using arbitrary hardware and operating systems in the first place. Google's security excuse is clearly bogus when they permit devices with no patches for 10 years but not a much more secure OS. It's for enforcing their monopolies via GMS licensing, that's all.
CodeX retweeted

Oh... well that's not good


🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.
CodeX retweeted

AdaptixC2 v1.1 is out!
* New DNS/DoH beacon listener
* New extenders type - service
* New BOFs in Extension-Kit
* Added Events/Hooks manager
Full update info: adaptix-framework.gitbook.io…
