

Cybersecurity researcher focused on threat intel & APTs. Breaking down attacks, hunting threats, and crafting YARA rules. Buddy @ Three Buddy Problem
Bucharest
Joined October 2007
- Tweets10.6K
- Following7.8K
- Followers39.8K
- Likes23.5K



Pinned Tweet
The Cybersecurity Booklist: 11 Must-Reads for 2026 from The Three Buddy Problem Podcast: medium.com/@costin.raiu/the-… @ryanaraine @juanandres_gs

Costin Raiu retweeted

A trusted contact who has a working exploit tells me reliable exploitation is still possible against PHP 8.2.35 and 8.5.12, despite the security updates.
According to their testing, setting
session.upload_progress.enabled = Off
blocks that exploit path.
I haven’t reproduced this myself. Whether this is an incomplete fix for the disclosed CVEs or a separate issue still needs clarification.

Leaving this here, PHP 8.5.12 security patch is incomplete. ( needs further validation )

Readers added context they thought people might want to know
The PHP 8.5.12 release fixes the two specific CVEs (via state/bailout changes) detailed in official advisories; referenced "surviving paths" (e.g. var_destroy UAF) are separate pre-existing unserialize issues unrelated to this patch.
php.net/archive/2026.p…
github.com/php/php-src/se…
github.com/php/php-src/se…
github.com/dinosn/php-8.5…
Costin Raiu retweeted

It doesn't bring much relief knowing that the initial patches likely were not complete while millions of tokens are being spent trying to produce working exploits + find related vulnerabilities.

⚠️ UPDATE: PHP maintainers have verified a separate double-free regression in PHP 8.4.27/8.5.12.
It may be related to the researcher's earlier crash report, but that connection isn't confirmed.
Neither finding establishes that the php2shell patches failed or that RCE is possible.
Repo updated: github.com/php/php-src/issue…
#php #CyberSecurity

Costin Raiu retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.


Costin Raiu retweeted
"On October 21st at 07:41 UTC, more than six hours before the coordinated release, Chainguard unilaterally broke the embargo and published built images containing the fix. Like other distributors, Chainguard had received the patch in advance so its users could update the moment the vulnerabilities were disclosed. Any attacker could now study the fix in binary form while every other PHP user was still waiting for the release. This disregarded weeks of work by many parties toward a coordinated disclosure."
thephp.foundation/blog/2026/…


Costin Raiu retweeted
Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: xitter.cf/lcfr_hax/status/208503…
His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.

Keeping track of all #PHP2Shell things, IOCs, log artifacts, exploitation status, patches, here: medium.com/@costin.raiu/php2…

Currently seeing 196.189.236[.]67 probing for the PHP vuns, suggest to block them on gateways, been hitting honeypots with a bunch of stuff since at least Oct 2.
Amazing leadership here from the PM of Japan:

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X


PHP vuln mitigation recommendations from the great @calif_io blogpost: calif.io/php2shell/ For PHP-FPM, disable session upload progress with session.upload_progress.enabled=0 and set memory_limit=-1.
For mod_php, set memory_limit=-1.
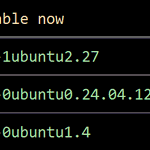
So far, refreshed repositories haven’t offered a newer PHP build on the completed systems: Ubuntu 22.04 remains on 8.1.2-1ubuntu2.27, and Ubuntu 24.04 on 8.3.6-0ubuntu0.24.04.12.
Costin Raiu retweeted
Since I heard about this #PHP #RCE last week, I've been preparing a tool for everyone who doesn't know what to do right now:
process-watcher shows you every program your PHP processes start, with full command lines, so you can spot suspicious activity
Until a patch is out, isolation (containers) and tight monitoring are your best bet to limit the damage. And I'm sure the LLMs already go "brrrr" and people are trying to reproduce the vulnerability.
From what I've heard, exploitation will probably show up as suspicious sub process spawns. That's exactly what this watches, using eBPF: one static binary for Linux (amd64, arm64), no dependencies, running in a few minutes. It can also kill the ones you name (dry run first), but it's a detection layer, not a patch, and it can't see anything that happens inside PHP without starting a process.
Quick start: github.com/Neo23x0/process-w…
Project: github.com/Neo23x0/process-w…


Costin Raiu retweeted

Reducing the attack surface of deployed services and apps is a fundamental component of software that is secure by design. Earlier this year we tasked Claude with autonomously mapping and reducing the attack surface of 25 large and widely used OSS codebases. This blog post covers some of our methodology and a preview of the data we collected.
This research resulted in a significant reduction in OpenSSH pre-authentication attack surface (now fixed in 10.6). And over 500 findings where reachability could be reduced and configurations hardened to ensure security controls weren’t silently disabled.
anthropic.com/research/attac…

Costin Raiu retweeted
Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…


🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow
The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0.
⠀
Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8.
PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases.
⠀
The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected.
⠀
Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available.

Costin Raiu retweeted

Just watched the @netflix Instadocs about the @OpenAI cyberattack on @huggingface. Super disappointing, as they went for maximum anthropomorphism of the technology and full doomer mode.
I spent more than two hours with them trying to correct all their mistakes and ground this in reality, explaining that agents are technological systems, not aliens. But it looks like the drive to scare people for maximum views was too strong.
Also, they didn’t mention the lack of containment and monitoring of the agents, how closed-model safeguards blocked our defensive work, or how we defended ourselves with AI using an open model. And that we still lack a lot of information and transparency, including full agent traces and that companies need to remain accountable for what their agents do.
It ends up being a fun sci-fi movie though!

