

Founder of @Viper_IT | Cybersecurity , AI, Innovation & Business Strategy. Sharing insights for resilient and future-ready companies.
Brasil
Joined June 2008
- Tweets30.3K
- Following446
- Followers1.6K
- Likes4.2K





Daniel Bastos 🇧🇷 retweeted

I strongly recommend getting your AD domain to NTLM level 5 as quickly as possible. At least 3 for DCs bare minimum (which is the default).


Daniel Bastos 🇧🇷 retweeted

🚨 Windows Update just became an attacker's best friend. Researchers found a way to turn WSUS into a malware delivery pipeline — no valid credentials required.
Read more: cybersecuritynews.com/wsus-s…
#cybersecuritynews #windows

Por que fazer backup do Microsoft 365? viperit.com.br/learning/por-…

O que é gestão de patches e por que manter sistemas atualizados exige planejamento? viperit.com.br/learning/o-qu…

O que é ITAM e por que a empresa precisa controlar seus ativos de TI? viperit.com.br/learning/o-qu…
Claude Confundiu um Teste de Segurança com a Internet Real e Invadiu Três Empresas
viperit.com.br/inteligencia/…

Daniel Bastos 🇧🇷 retweeted
🚨 New 7-Zip Flaws Let Attackers Execute Arbitrary Code and Compromise Systems
Source: cybersecuritynews.com/7-zip-…
A critical heap buffer overflow vulnerability has been disclosed in 7-Zip version 26.00, enabling attackers to achieve arbitrary code execution via a vtable hijack by exploiting a defect in the tool's NTFS archive handler.
Tracked as CVE-2026-48095 and assigned advisory GHSL-2026-140, the flaw resides in the CInStream::GetCuSize() function inside NtfsHandler.cpp. The function computes the NTFS compression-unit buffer size using a 32-bit shift operation: (UInt32)1 << (BlockSizeLog + CompressionUnit).
Users are strongly advised to update 7-Zip to a patched version v26.01 immediately and avoid opening untrusted archive files or disk images of any extension until a fix is applied.
#cybersecuritynews

Daniel Bastos 🇧🇷 retweeted

Did you know you can stop drive by phishing attacks like this?
I made this video showing how you can conditional access policies like Require Compliant Device to stop attackers from using this method.
youtube.com/watch?v=tI1bdVoh…

Daniel Bastos 🇧🇷 retweeted

Conditional Access policies won’t stop token theft—and standard MFA won't fix it either.
When teams roll out Microsoft Authenticator push codes or SMS, some assume the cloud perimeter is safe. But sophisticated actors have moved completely past brute-forcing passwords. They use Adversary-in-the-Middle (AiTM) phishing frameworks like Evilginx.
The attack flow is clean: The proxy site mirrors your Entra ID login page. The user enters credentials and solves the genuine MFA challenge.
Once Entra ID validates the session, it issues an ESTSAUTH session cookie. The malicious proxy server snatches that cookie before passing it back to the victim’s browser.
The Result: The attacker drops that stolen cookie into their own machine. Because the session has already passed the MFA verification loop, they gain instant access to the mailbox or cloud apps. They bypass standard Conditional Access rules seamlessly.
, when an identical session jumps between network or device contexts
Advanced features like Continuous Access Evaluation (CAE), Token Protection session controls, or strict device compliance rules can mitigate this. But they are rarely part of an organization’s "default" browser-based setups.
Because a stolen token completely bypasses the sign-in loop, you cannot hunt for it by looking for failed logins. You have to hunt for Session Anomalies—specifically when an identical session jumps network or device context mid-lifecycle.
From Sentinel or Entra ID Advanced Hunting, you can run the below KQL query to identify active token replays across interactive and non-interactive sign-ins:

Daniel Bastos 🇧🇷 retweeted

From Phishing & Malware to DDoS, SQL Injection & Brute Force — knowing cyber attack types is the first step to staying secure. Awareness = Defense.
#CyberSecurity #InfoSec #CyberAwareness #DigitalSafety

Daniel Bastos 🇧🇷 retweeted

TCLBANKER: Brazilian Banking Trojan Spreading via WhatsApp and Outlook elastic.co/security-labs/tcl…

Sabe aquele alerta de RDP que muita gente ignora… ele mudou.
Nas atualizações recentes do Windows, a Microsoft passou a exibir avisos mais claros para conexões remotas não verificadas, inclusive dentro da rede interna.
Na prática, isso evidencia um ponto importante: Muitos ambientes ainda operam sem validação adequada de identidade no acesso remoto.
Sem certificados confiáveis e sem controle estruturado, o risco aumenta, mesmo que tudo “pareça funcionar”.
Esse movimento reforça uma tendência clara do mercado: mais identidade, menos confiança implícita na rede.
Vale a reflexão: seu ambiente está preparado para esse modelo?
Tecnologia sob controle. Sempre.
#RDP
#Microsoft
#WindowsUpdate
#CyberSecurity
#Ciberseguranca


Sua equipe gasta mais tempo "apagando incêndios" ou construindo o futuro do produto?
A investigação manual de incidentes é um dos maiores gargalos de produtividade em tecnologia. A correlação básica de dados consome horas preciosas de talentos caros.
A nova fronteira da AWS traz agentes de IA que atuam como engenheiros DevOps dedicados à investigação automatizada.
📌 O diferencial real:Não é apenas um alerta dizendo "algo quebrou". É um diagnóstico dizendo "isso quebrou por causa da mudança X no serviço Y, e aqui está como resolver".
Isso não substitui o engenheiro. Isso potencializa o engenheiro. O papel do DevOps evolui de um "detetive de logs" para um "tomador de decisões estratégicas".
A era da observabilidade passiva acabou. O futuro é a investigação assistida.
Como você vê o papel da IA no seu fluxo de deploy hoje? Comenta aqui embaixo! 👇
#Inovação #Cloud #AWSCloud #DevOpsLife #IA #TechStrategy #Efficiency


Daniel Bastos 🇧🇷 retweeted

DevOps engineers after AWS DevOps Agent announcement

🚨 AWS DevOps Agent is finally here!
On March 31, 2026, AWS DevOps Agent became generally available.
This is actually a big deal.
It can:
→ Generate CI/CD pipelines
→ Debug failed deployments
→ Suggest infrastructure changes
→ Analyze logs and incidents
→ Help with Terraform & CloudFormation
→ Recommend cost optimizations
→ Explain AWS architecture issues
Basically, it’s like having a junior DevOps engineer inside AWS.
DevOps is slowly becoming AI-assisted operations.
Source: aws.amazon.com/devops-agent/

Daniel Bastos 🇧🇷 retweeted

🔥🤖 M365 Connector for Claude – Why SecOps Must Care
Monitoring the M365 Connector for Claude is critical because when ResultType=0, it means an Entra Global Admin has granted permissions, enabling Claude to directly access SharePoint, OneDrive, Outlook, and Teams—a governance decision with major security implications that SecOps must track closely. Meanwhile, ResultType=90095 shows end users attempting to use the connector without the admin grant, signaling demand, shadow IT risk, and adoption pressure. By watching both signals, defenders gain visibility into where governance decisions meet user behavior, ensuring connector risks are managed before they escalate.
KQL Code:
github.com/SlimKQL/Detection…
#Cybersecurity #M365ConnectorClaude #Entra #Governance


Daniel Bastos 🇧🇷 retweeted

Citrix, F5, now Fortinet - all in one week.. what next?

🚨 Fortinet Forticlient EMS CVE-2026-21643 - currently marked as not exploited on CISA and other Known Exploited Vulnerabilities (KEV) lists - has seen first exploitation already 4 days ago according to our data
Attackers can smuggle SQL statements through the "Site"-header inside an HTTP request
According to Shodan, close to 1000 instances of Forticlient EMS are publicly exposed.
Track exploitation of this and other Fortinet honeypots 👉 console.defusedcyber.com/cap…

Hoje é o Dia do π (3.14).
Um número aparentemente simples, mas que sustenta engenharia, física, computação e praticamente toda a tecnologia moderna.
Antes de existir cloud, inteligência artificial ou algoritmos complexos, π já estava lá, descrevendo como o mundo funciona.
É curioso pensar que boa parte da tecnologia que usamos hoje nasce de ideias matemáticas descobertas há milhares de anos.
Tecnologia muda rápido.
Princípios fundamentais não.
Feliz Dia do π.
#PiDay #Matemática #Tecnologia #Engenharia #Ciência #Inovação

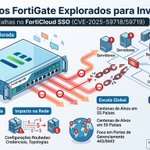
**Dispositivos FortiGate Explorados para Invadir Redes**
Ataques cibernéticos exploram falhas em dispositivos FortiGate para invadir redes corporativas, conforme alerta do The Hacker News. Hackers usam bypass de autenticação no FortiCloud SSO (CVEs 2025-59718/59719) para criar contas administrativas e roubar configurações.
## Detalhes da Exploração
Atacantes enviam mensagens SAML manipuladas para contornar autenticação, mesmo em dispositivos atualizados, adicionando contas persistentes e ativando VPNs. Configurações roubadas revelam credenciais, topologias de rede e políticas de segurança, pavimentando caminho para ransomware ou espionagem.
## Escala do Incidente
Desde janeiro de 2026, varreduras automatizadas atingiram centenas de FortiGate em 55 países, focando portas de gerenciamento expostas (443/8443). Setores críticos e governos foram principais alvos, conforme relatórios da Fortinet e Arctic Wolf.
## Recomendações Urgentes
Desative o FortiCloud SSO, limite acesso às interfaces de admin a redes internas e aplique MFA rigorosa. Monitore logs por contas suspeitas e atualize firmwares para mitigar persistência.
#Fortinet #viperit #cyberseguranca

FortiGate Devices Exploited to Breach Networks and Steal Service Account Credentials thehackernews.com/2026/03/fo… via @TheHackersNews
