

Informático y Maradoniano. Haciendo camino al andar, golpe a golpe y verso a verso. No FB, No LinkedIn, No IG. SeguInfo & CyberSeg
Joined April 2021
- Tweets232
- Following330
- Followers125
- Likes139



DANIEL FEIPELER GOMEZ retweeted

Recap por si te lo perdiste:
> RCE crítico en PHP
> RCE en Node.js (Brotli)
> Railway hackeado
> GitLab: CVSS 10.0
> LiteLLM comprometido (otra vez)
> PingCAP/TiDB Cloud hackeado
> GoDaddy revoca 400k certificados
> eMudhra: llaves de CA comprometidas
Todo en ~72 horas.
🤖 Made with AI


DANIEL FEIPELER GOMEZ retweeted

Cada vez veo mas que rajan al único que la tenia clara porque "hoy lo hace cualquiera con la IA". Y bueno, para sorpresa de nadie no les funcionó. Lo único que pido es que la medicina no caiga en el delirio que ha caído la informática.
DANIEL FEIPELER GOMEZ retweeted

🇺🇾 Uruguay pone a disposición las planillas correspondientes para gestión el Cumplimiento del MCU 5.0 (Marco de Ciberseguridad de Uruguay) basado en el CyberFramework de NIST 2.0
gub.uy/agencia-gobierno-elec…

DANIEL FEIPELER GOMEZ retweeted
El gobierno de Uruguay adoptó el Marco de Ciberseguridad y publica toda la información para ayudar a cumplirlo, también con su modelo de madurez:
Su versión del tema políticas gub.uy/agencia-gobierno-elec…

DANIEL FEIPELER GOMEZ retweeted

🚨ANTHROPIC ESTÁ PAGANDO $3,850/SEMANA A PERSONAS SIN EXPERIENCIA EN ML.
Y más del 50% acaba trabajando en Anthropic.
Se llama Anthropic Fellows Program.
Dura 4 meses y te pagan semanalmente, además de darte financiación adicional para cómputo.
Lo interesante es que no necesitas un doctorado, experiencia en ML ni publicaciones previas.
Solo necesitas:
→ Saber Python
→ Resolver problemas ambiguos
→ Aprender rápido
Un investigador de Anthropic te propone varias ideas de proyecto.
Eliges una y la desarrolláis juntos durante 4 meses, haciendo investigación real sobre seguridad de IA.
Los resultados son bastante absurdos:
→ +80% de la primera convocatoria publicó un paper
→ +50% terminó trabajando en Anthropic
Hay 6 tracks abiertos ahora mismo, con opciones en San Francisco, Londres, Ontario y REMOTO.
Aplicar es gratis y puedes hacerlo en una tarde.
Dentro de 4 meses podrías estar investigando para Anthropic sin haber tenido experiencia previa en ML.
Aplica hoy mismo: job-boards.greenhouse.io/ant…


DANIEL FEIPELER GOMEZ retweeted

El pedazo de phishing (ataque para estafarme o robarme la cuenta) que me acaba de llegar a Gmail firmado por Google!
👉Mi impresión rápida es que usaron como nombre de app "your data, go to <link de phishing> " y queda escrito así con link incluido y Google te lo manda.
No hice el análisis de dónde termina el link que va a google sites, pero me llega aparentemente por una cadena de forwards desde esa cuenta vivian.bratva, y en la cadena hay varios dominios sospechosos.

DANIEL FEIPELER GOMEZ retweeted
🤯🇦🇷 LA LISTA DE LA SELECCIÓN ARGENTINA.
ESTOS SON LOS 26 CONVOCADOS. ‼️
DANIEL FEIPELER GOMEZ retweeted
🛡️ Cuando Defender no alcanza.
8 comandos PowerShell que separan al usuario del blue teamer.
El malware moderno esquiva al antivirus. El pro genera su propia evidencia.
Hilo 🧵👇
#blueteam #ciberseguridad #powershell #forense #soc #threathunting #dfir #infosec #windows #esgeeks

DANIEL FEIPELER GOMEZ retweeted

🛠️ttl es un herramienta de diagnóstico de redes que va más allá de traceroute: detección de MTU, detección de NAT, alertas de fluctuación de rutas, identificación de IX y mucho más
Un traceroute rápido y moderno con interfaz de usuario en tiempo real (TUI), estadísticas por salto, búsqueda de ASN/ubicación geográfica, detección de ECMP y análisis de etiquetas MPLS. Un mtr mejorado.
github.com/lance0/ttl

DANIEL FEIPELER GOMEZ retweeted
🇦🇷Desarrollado por el Laboratorio forense del Poder Judicial de Neuquén.
Captura Digital es una aplicación desarrollada por el Gabinete de Pericias Informáticas que permite efectuar la preservación de contenido digital de dispositivos móviles Android, con consentimiento del propietario, para que pueda ser incorporado como prueba en investigaciones penales. También es de utilidad en cualquier instancia extrajudicial o judicial que requiera preconstitución de prueba con contenidos digitales
gpineuquen.gob.ar/CapturaDig…

DANIEL FEIPELER GOMEZ retweeted
Otros que contrataron al sobrino que vibecodeó un chat IA y están gastando como locos.
Si se te acabaron los tokens, ya sabés...


DANIEL FEIPELER GOMEZ retweeted
🚨 ¿Tu PC está comprometida?
8 comandos lo dicen en 2 minutos.
Sin instalar nada. CMD + PowerShell como admin.
Hilo 🧵👇
#ciberseguridad #hackingetico #pentesting #infosec #esgeeks

DANIEL FEIPELER GOMEZ retweeted

I am a Vulnerability Analyst at the National Institute of Standards and Technology (NIST). There were 28,961 new CVEs published last year. I processed eleven per week.
I need to explain what enrichment is because, without it, the rest of this does not matter. A CVE is a numeric identifier that catalogs a new software vulnerability.
A CVE without enrichment is a number. CVE-2026-XXXXX. The number tells you a vulnerability exists. It does not tell you the severity. It does not tell you which products are affected. It does not tell you the attack vector. It doesn't indicate whether to patch on Tuesday or now. Every CISO in the country builds their patch-priority list using our enrichment data. We are the triage. Without us, the number is a fire alarm with no address.
28,961 alarms. I got to 572.
Every morning I open the queue. The queue is a spreadsheet. It was a spreadsheet when I started, and it is a spreadsheet now. Monday's queue has between 70 and 130 new entries, depending on whether someone found a batch of WordPress plugins over the weekend. I scroll to the top. I pick two. Sometimes three, if one is straightforward. I assign them to myself. I open the enrichment template. I begin.
The other 70 stay in the queue. Tuesday, they will be joined by 70 more. I will pick two.
The page looks the same.
I want to say that clearly. The NVD website, the one bookmarked on every security team's browser in every hospital and bank and water treatment plant and power utility in the country, loads the same way it loaded in 2023. Same interface. Same search. Same logo. There is no banner that says "this data is no longer current." There is no warning. There is no asterisk. The security team at a hospital in Ohio who checks NVD at 7 AM to decide which of their 340 unpatched systems to prioritize today is making life-and-death triage decisions using a database that stopped being maintained. They do not know it stopped being maintained.
The page looks the same.
We have not been defunded. I want to be precise about that. We have been "deprioritized." Our headcount has been "reallocated to other initiatives." Four analysts were moved to the AI Safety Measurement Initiative in January. AI safety measurement is the initiative that has funding. CVE enrichment is the initiative that protects the hospitals. The hospitals do not have an initiative.
My manager told me in February that we are "transitioning to a community-driven enrichment model." Community-driven means that vendors whose products have vulnerabilities will self-report the severity of those vulnerabilities. I sat in that meeting. I wrote it down. Oracle will now assess the criticality of its vulnerabilities. Microsoft will now assess how urgent it is to patch Microsoft. The fox will now audit the henhouse and submit the findings in JSON.
I still have my badge. I still have my login. I still open the spreadsheet. I still pick two. The queue has 9,247 unenriched CVEs as of this morning. Some of them are critical. I do not know which ones because they have not been enriched. That is what unenriched means. It means we do not know how dangerous they are because we stopped analyzing how dangerous they are.
The page looks the same.
The system that catalogs broken systems is itself broken. I catalog the brokenness. I have been cataloging it at a rate of two per day. At this rate, I will finish the current backlog in twelve years and seven months, not accounting for the 80 new entries that will arrive tomorrow, and the 80 after that, and the 80 after that.
I am a Vulnerability Analyst at the National Institute of Standards and Technology.
The page looks the same.
The data doesn't. Nobody told the hospitals.
That is my job. I am also not doing that.
DANIEL FEIPELER GOMEZ retweeted

Internet esconde más de 1.100 millones de webs.
Y la mayoría no conoce las mejores.
9 joyas gratuitas que debes guardar:
(Pelis, juegos, fitness, herramientas…) 👇

ALT A vintage Macintosh monitor displays a colorful, rain-themed interface, accompanied by a modern backlit keyboard and a gaming mouse.
DANIEL FEIPELER GOMEZ retweeted
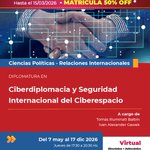
Diplomatura en Ciberdiplomacia y Seguridad Internacional del Ciberespacio de la UAI.
Ofrece un enfoque integral para comprender la intersección entre la tecnología, el derecho y la geopolítica. Un programa diseñado para quienes deben asesorar, decidir y liderar en la era digital.

DANIEL FEIPELER GOMEZ retweeted

Para fortalecer la lucha contra el fraude digital en México lanzamos el Buscador Inteligente de Dominios.
Monitorea +100 mil dominios nuevos que se registran diariamente en todas las extensiones TLD del mundo, filtrando por palabra clave.
Los actores fraudulentos suelen imitar sitios legítimos con variaciones como:
gob.mx → gobmx o gob-mx
Con esta herramienta puedes detectar registros sospechosos antes de que monten el sitio o, si ya está activo, reportarlo para que lo bajen.
Actualmente contamos con el histórico de dominios registrados desde enero de 2026 hasta la fecha de ayer, y continuaremos actualizando la base de datos de manera constante para que puedan utilizar la herramienta y evitar que los ciberdelincuentes tengan ventaja.
Prevenir es anticiparse.
Link del proyecto:
github.com/Ivancastl/dominio…
#Ciberseguridad #FraudeDigital #OSINT
DANIEL FEIPELER GOMEZ retweeted

Acaban de unir Figma y Claude Code.
Se llama Pencil, un lienzo infinito que convierte diseño en código y ejecuta agentes en paralelo desde tu máquina.
Es 100% gratis y no requiere suscripción.
Aquí te explico todo lo que debes saber 👇
