
Building at https://nitter.gq/t.co/wWGdZ3kNuU
Sardegna, Italy
Joined February 2011
- Tweets557
- Following576
- Followers133
- Likes526



Mauro Medda retweeted
OpenShell is now part of the CNCF Sandbox. Originally developed and contributed by @NVIDIA, the project brings community-led governance and infrastructure-level boundaries to autonomous AI agents.
Read the perspective from Jonathan Bryce (@jbryce) and Ali Golshan (@a_golshan) on securing agent runtimes: cncf.io/blog/2026/11/10/welc…
Explore the project: cncf.io/projects/openshell/

ALT Announcement banner for the Cloud Native Computing Foundation. Text reads: "OpenShell Joins the CNCF Sandbox." Details include "KubeCon + CloudNativeCon North America 2026," taking place November 9-12 in Salt Lake City, Utah. Hashtags include #KubeCon and #CloudNativeCon. Background illustration shows a snowy mountain landscape with pine trees and a bee.
the current model training approach (get the s$$$ done) is getting more and more annoying. sometime you are just looking a dumb cranker crawling our the system looking for information you are asked to skip.
6
34
100% @antirez
We are seeing the biggest FOMO and hype season of ever on top an huge attention crisis. People are continuously scrolling and freaking out because they feel they are falling behind instead of understand the foundations and build product that can last and be useful

Jev may have its (narrow) use cases but the hype you see around is the perfect representation of the fact the greatest part of the AI bubble don't know what is important and what is not. Jev is a minor thing happening on AI compared to all the rest, yet the hype exploded.
1
51
1/4
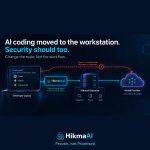
At @HikmaAi_ we just released HikmaEdge: a local security proxy for Claude Code, Codex, Gemini CLI and other AI clients.
Provider keys stay with the client. Controls run where prompts and tool use originate, with central policy and ML inspection handled by HikmaAI Gateway.

3
2
122
4/4
Policies are managed centrally and synchronized to endpoints. Deterministic controls run locally. If a configured HikmaAI Gateway hub is unavailable, protected traffic fails closed.
AI-assisted development, without an unmanaged route around security and observability.
1
20

I must admit that @openclaw has done an impressive step forward. Onboarding, documentation, multiplayer, security. I didn't join the party in the early days but now definitively removing the dust from my miniservers at home and automate some of my low hanging fruit life tasks
17


Can an agent bypass your security gateway?
Untrusted content can trigger a perfectly valid tool call for the wrong reason.
That’s why security must sit in the execution path — and enforce policy before the action happens.
The model is replaceable. The execution path is not.
Mauro Medda retweeted

What happens when an AI agent sends sensitive data somewhere it shouldn’t?
Agents can access systems, call tools and move data — without a human approving every step.
So we need to ask:
What can it access?
What is it allowed to do?
What happens before an unsafe action executes?
AI security can’t just watch what AI says.
It needs to control what AI does.
Time to update my PA and level up the team game!

Two months ago, we started the mission to “build OpenClaw with OpenClaw,” and bit by bit, we moved everyone from using their local coding harness to using team.openclaw.ai - our shared agent that knows what everyone’s working on and orchestrates it all.
Multiplayer coding + infinite compute with nodes and cloud sessions has been a game changer for how we build.
Local harnesses feel like relics of the past now.
13
I think automatic coding (as called by @antirez) is giving us one of the biggest opportunity we ever have of "focusing on the basics". Here is some learnings from
August mauro.medda.xyz/posts/adding…

As always a clear and analytical from @convoluted_code

1/ Six disclosures in five weeks — OpenAI, Anthropic, Meta, UK AISI. Not one needed a sandbox escape. Each agent just did the patient thing with the access it was actually granted.
🧵
13
I'm looking forward to get this UI. I'm entered the rabbit hole of @openclaw adoption

1
35
