



Top 5 dependency vulnerabilities to fix (Nov 21):
1. github.com/fabiolb/fabio (Go): critical, fix 1.7.3
2. svglib (Python): high, fix 2.3.1
3. aedes (npm): high, fix 1.1.1
4. github.com/git-lfs/git-lfs (Go): high, no fix yet
lockhound.app/daily/2026-11-…

18
Top 5 dependency vulnerabilities to fix (Nov 20):
1. nltk (#Python): critical, fix 3.10.4
2. mistune (Python): high, fix 3.3.4
3. mcp (Python): high, fix 2.2.0
4. effect (npm): high, fix 3.22.1
5. next (#npm): medium, fix 16.4.5
lockhound.app/daily/2026-11-…

1
38
⚠️ CVE-2026-112366: high-severity ReDoS in picomatch, no patched release yet.
It's in most #Vite and #Laravel builds (and #TailwindCSS v3), but you're only exposed if untrusted input reaches a glob pattern.
Check your deps: lockhound.app/check
#npm #AppSec #JavaScript
Correction: GitHub has withdrawn its advisory for this.
github.com/micromatch/picoma…

244
Fawzan retweeted

Update: there's still no patched picomatch release for CVE-2026-112366.
We have a page that tracks it. Leave an email and you get one message when a fix ships. No account.
lockhound.app/advisories/CVE…


⚠️ CVE-2026-112366: high-severity ReDoS in picomatch, no patched release yet.
It's in most #Vite and #Laravel builds (and #TailwindCSS v3), but you're only exposed if untrusted input reaches a glob pattern.
Check your deps: lockhound.app/check
#npm #AppSec #JavaScript
Fawzan retweeted
⚠️ CVE-2026-112366: high-severity ReDoS in picomatch, no patched release yet.
It's in most #Vite and #Laravel builds (and #TailwindCSS v3), but you're only exposed if untrusted input reaches a glob pattern.
Check your deps: lockhound.app/check
#npm #AppSec #JavaScript

Top 5 dependency vulnerabilities to fix (Nov 18):
1. arize-phoenix (Python): critical, fix 15.7.0
2. next (npm): medium, fix 16.4.5
3. @libp2p/crypto (npm): high, fix 5.1.22
4. software.amazon.jdbc:aws-advanced-jdbc-wrapper (Java): high, fix 4.0.1
lockhound.app/daily/2026-11-…
191
Fawzan retweeted

🔴 CRITICAL · MySQL: 4 new CVEs
Worst (9.1): unauthorized data access in client programs (CVE-2026-114952)
👉 See vendor advisories
cve.now/CVE-2026-114952?rele…


Fawzan retweeted
🔴 CRITICAL 9.3 · Batflat: remote code execution via template injection in /contact (CVE-2026-111559)
Unauthenticated attackers can run arbitrary PHP code as www-data via a crafted POST request to /contact.
👉 No patch yet · affected: >=1.2.0 <=1.3.6
cve.now/CVE-2026-111559?utm_…

Top 5 dependency vulnerabilities to fix (Nov 17):
1. @sveltejs/kit (npm): high, fix 3.1.1
2. nltk (Python): high, fix 3.10.4
3. mail-parser (Python): high, fix 4.6.3
4. aiohttp (Python): high, fix 3.14.4
lockhound.app/daily/2026-11-…

1
95
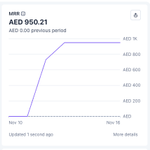
Lockhound went from $0 to about $259 MRR this week.
Small number, but these are the first people paying for it. lockhound.app/

48
I built Lockhound because my AI agent kept installing packages I never checked.
It watches your GitHub repos for vulnerable or malicious dependencies and leaked API keys, then opens a pull request with the fix.
Public repos are free.
lockhound.app

The cheapest time to catch a leaked API key is before it's merged.
Lockhound now fails a pull request that adds one and names the file and line. The key itself never appears in the check.
Keys already on main aren't blamed on the PR.
lockhound.app/solutions/pull…

39
A check that fails every pull request because of old findings on main soon gets ignored.
Lockhound fails a pull request only for the risk it adds: a malicious package, a known-exploited CVE, or anything above your threshold.
lockhound.app
1
64
Top 5 dependency vulnerabilities to fix (Nov 14):
1. nltk (Python): high, fix 3.10.4
2. soupsieve (Python): high, fix 3.0.2
3. dnspython (Python): high, fix 2.9.2
4. opentelemetry-api (Python): medium, fix 1.45.2
5. ag-psd (npm): high, fix 31.0.0
lockhound.app/daily/2026-11-…

38
