

@efaav
Account based inUnited States
About this account
- Account based in
- United States
- Connected via
- Web
Account-level information from X, not a live location or the device used for a specific post.
Hacker & Developer. Hunting bugs. Building https://xitter.cf/t.co/qiMEJOTD1H & NameMC Extras.
Florida
Joined November 2024
- Tweets568
- Following248
- Followers6.2K
- Likes3.5K




Faav retweeted

private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…

Faav retweeted

If Discord is only paying $5k for an RCE in their desktop client, it's probably time to uninstall it

Faav retweeted

yo, just sharing my latest personal achievement. My biggest bug bounty yet, $30,000 from MSRC.
@bsysop and I uncovered RCE vulnerabilities affecting 100% of the Major Cloud providers.
Proud of the research. Even prouder of the impact.
We may share the technical deep dive in a future blog post.


Faav retweeted

The details of the long awaited KVM Escape are published. PwnEscape leads to VM escapes across multiple hypervisors due to a super cool Linux networking bug.
CVE-2026-99999 is a 9.3 CVSS critical rated KVM escape ⛓️
pwn.ai/blog/pwnescape


Faav retweeted

This hacker news thread is absolutely heart-breaking.
Whoever thinks “humans will find a way” ought I read it.


Faav retweeted

there is a pattern in all the recent critical vulnerabilities coming out of gitlab.
look at the researcher(s) finding them and their track records.
and then ponder about the whole “yeah bro, just throw more tokens and you’ll saturate all vulnerabilities” argument.


Faav retweeted

I found a critical unauthenticated SQL injection that earned a $4,000 bounty. The WAF blocked most SQLi payloads, but I turned HTTP 500 errors into a data extraction channel.
The exploit came down to 3 things:
- SQL injection: A public API passed user input directly into BigQuery SQL.
- WAF bypass: Keyword filtering missed BigQuery scripting techniques.
- Error-based extraction: Detailed database errors exposed query results in HTTP 500 responses.
Here's how I chained all three together:
1. Find the injection
A public analytics endpoint accepted JSON input.
Adding a single `'` to a parameter returned:
`500 → Syntax error: Unclosed string literal`
The error also revealed Google BigQuery was the backend.
2. Build a boolean oracle
The WAF blocked keywords like `UNION`, `SELECT`, `AND`, and `OR`.
But BigQuery scripting constructs like `IF` and `ASSERT` still worked:
`IF TRUE THEN ASSERT FALSE; END IF;` → 500
`IF FALSE THEN ASSERT FALSE; END IF;` → 200
This let me ask the database true/false questions and read the answers from HTTP status codes.
3. Turn the 500 error into an output channel
This was the biggest breakthrough because blind SQLi normally requires guessing data one character at a time using those true/false responses.
But BigQuery supports:
`RAISE USING MESSAGE = 'hello'`
This deliberately throws a database error containing `hello`.
Because the API exposed database error details, the response included:
`500 → ... hello ...`
Now imagine replacing `hello` with a database query result.
The database includes that result in its error message, and the API returns it.
Instead of guessing characters, I could retrieve an entire value in one request.
4. Bypass the WAF using BigQuery's own features
The WAF blocked `EXECUTE IMMEDIATE`, which runs dynamically constructed SQL.
But this worked:
`EXECUTE/**/IMMEDIATE`
The SQL parser understood it, while the WAF's keyword matching didn't.
Another blocked keyword was `INFORMATION_SCHEMA`, used to enumerate tables and columns.
The bypass was:
`REVERSE('AMEHCS_NOITAMROFNI')`
BigQuery reconstructs `INFORMATION_SCHEMA` at runtime.
Using that reversed string in a dynamic query let me access database metadata without sending the blocked keyword literally.
5. What this unlocked
Using those techniques, I was able to:
- Enumerate datasets, tables, and columns
- Query tables unrelated to the original analytics endpoint
- Retrieve customer records, names, and addresses
- Access operational records containing personal identifiers and contact information
- Read sensitive fields that another API intentionally redacted
#BugBounty tip:
When a WAF blocks SQLi, don't just try random payloads. Understand the database dialect, what the WAF filters, and whether verbose errors leak data.
Sometimes a `500` isn't just an error. It may be your output channel.
Got to number 4 on the Mozilla bug bounty program but they closed submissions ): (Not for Firefox Browser)


Faav retweeted

Turns out those Unicode dashes are actually useful.
Filter blocks "-"? Send full-width "-" instead. Windows converts it back to "-" inside curl.exe, injecting a -o argument that drops a webshell.
Faav retweeted

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…

Faav retweeted

‼️ BREAKING: Ledger confirmed an unauthorized hardware implant in a wallet sold through its official reseller CryptoBilis.
The supply chain attack has drained $92.9M from 311 wallets.
CryptoBilis has stopped selling all hardware wallets (also Trezor, Tangem and SafePal).


Faav retweeted

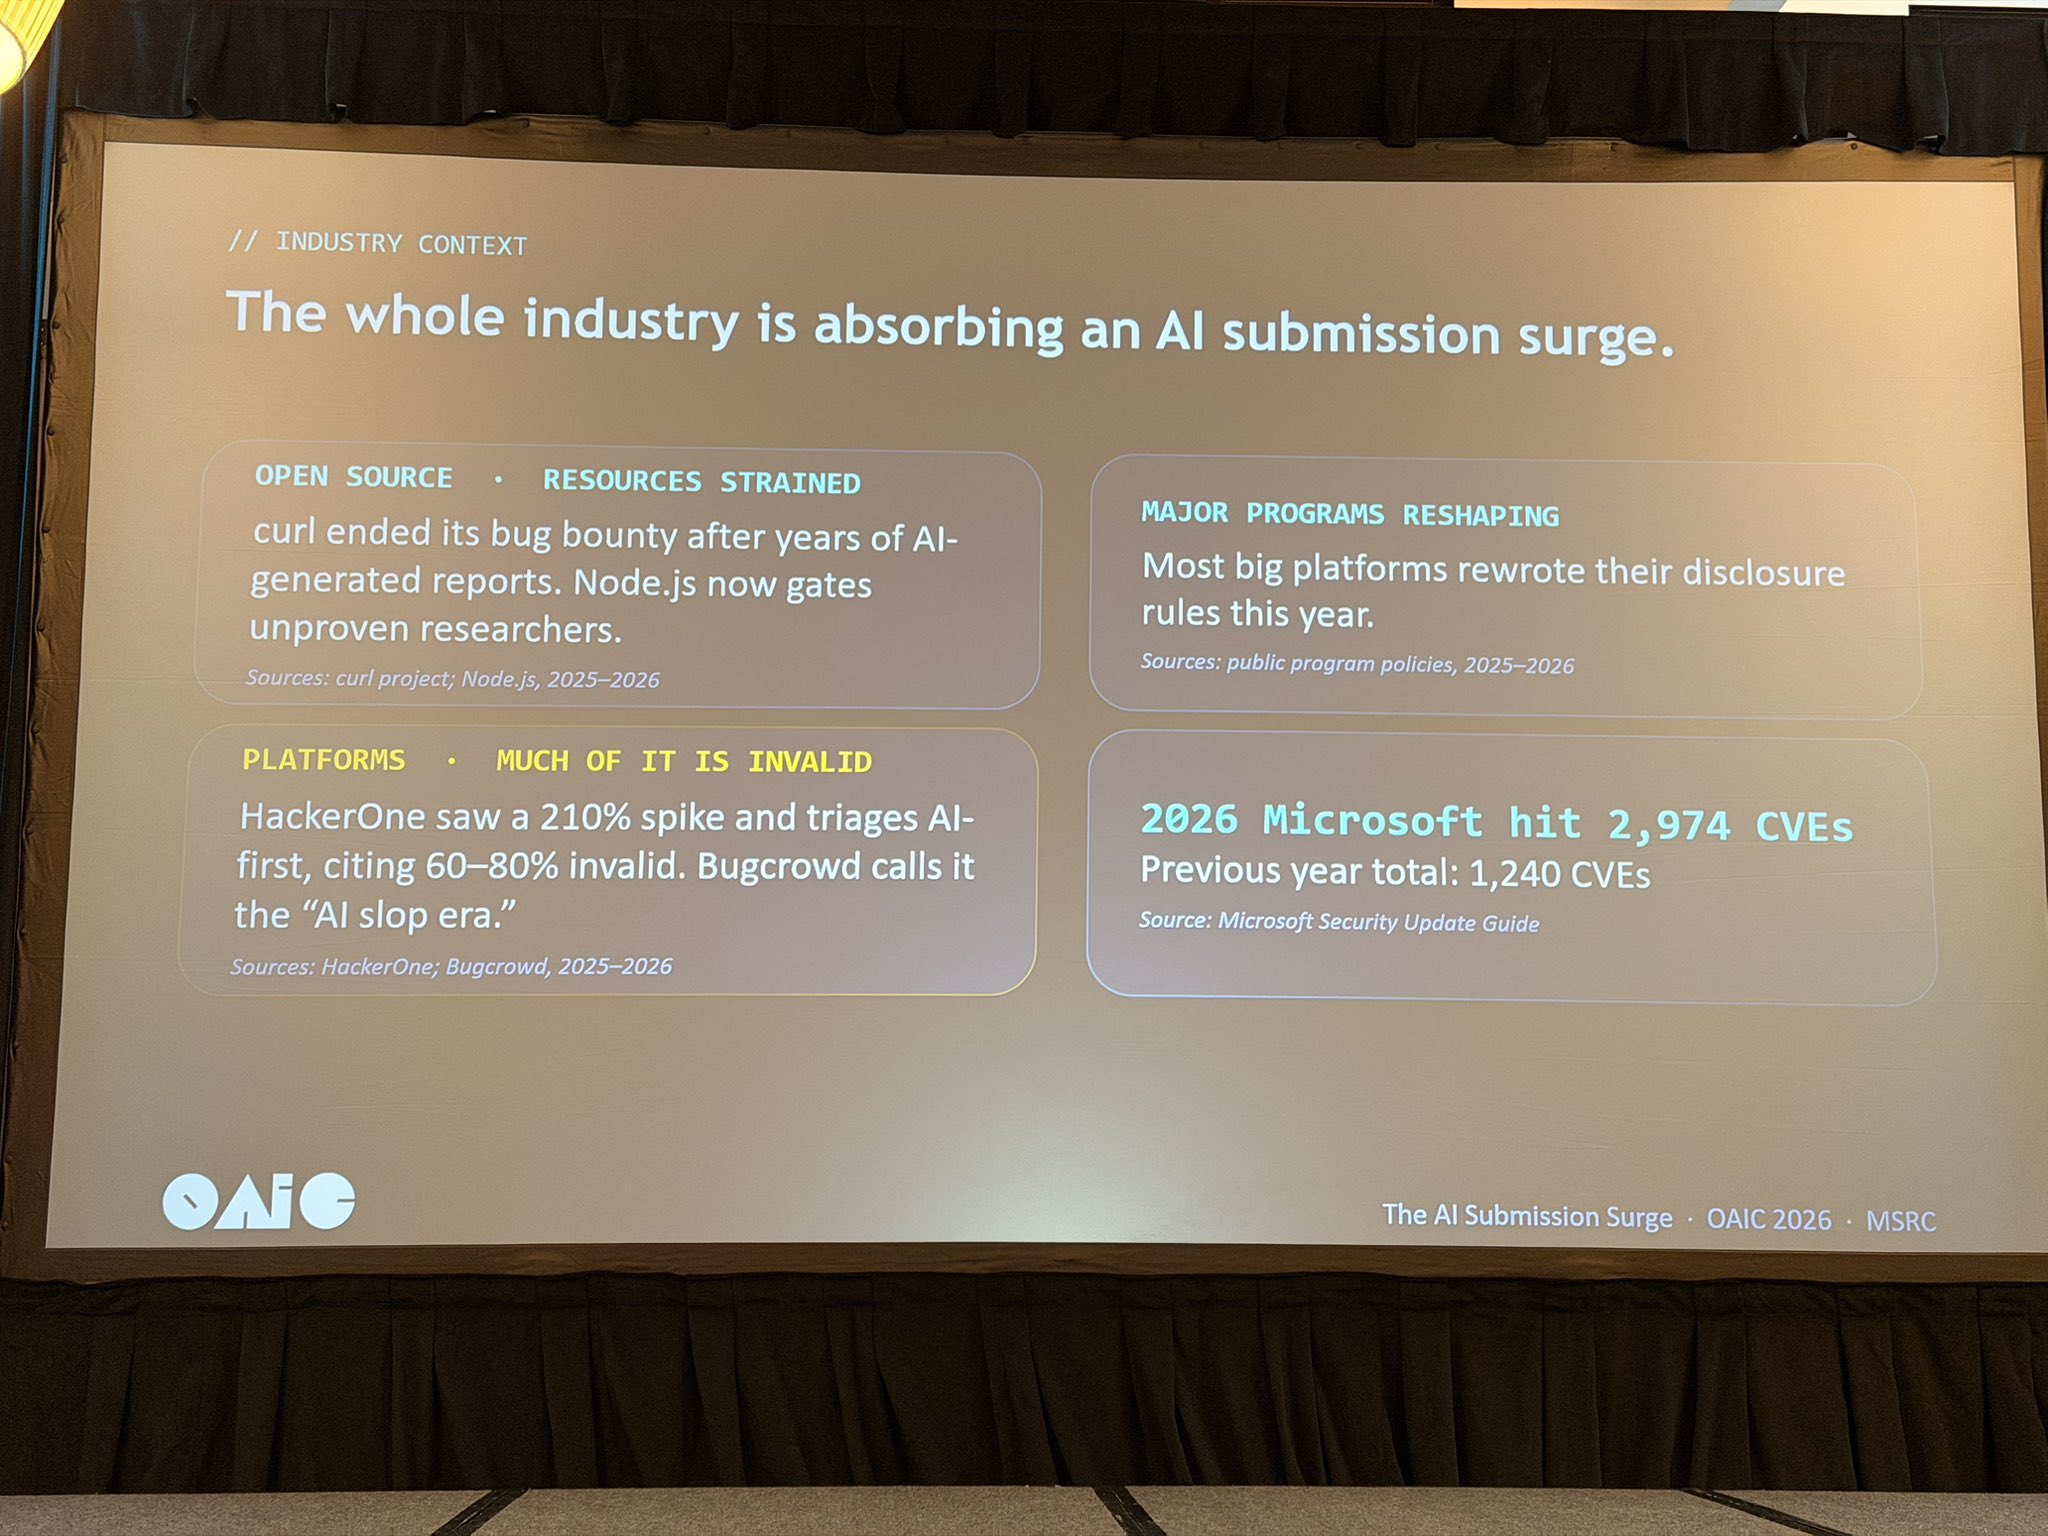
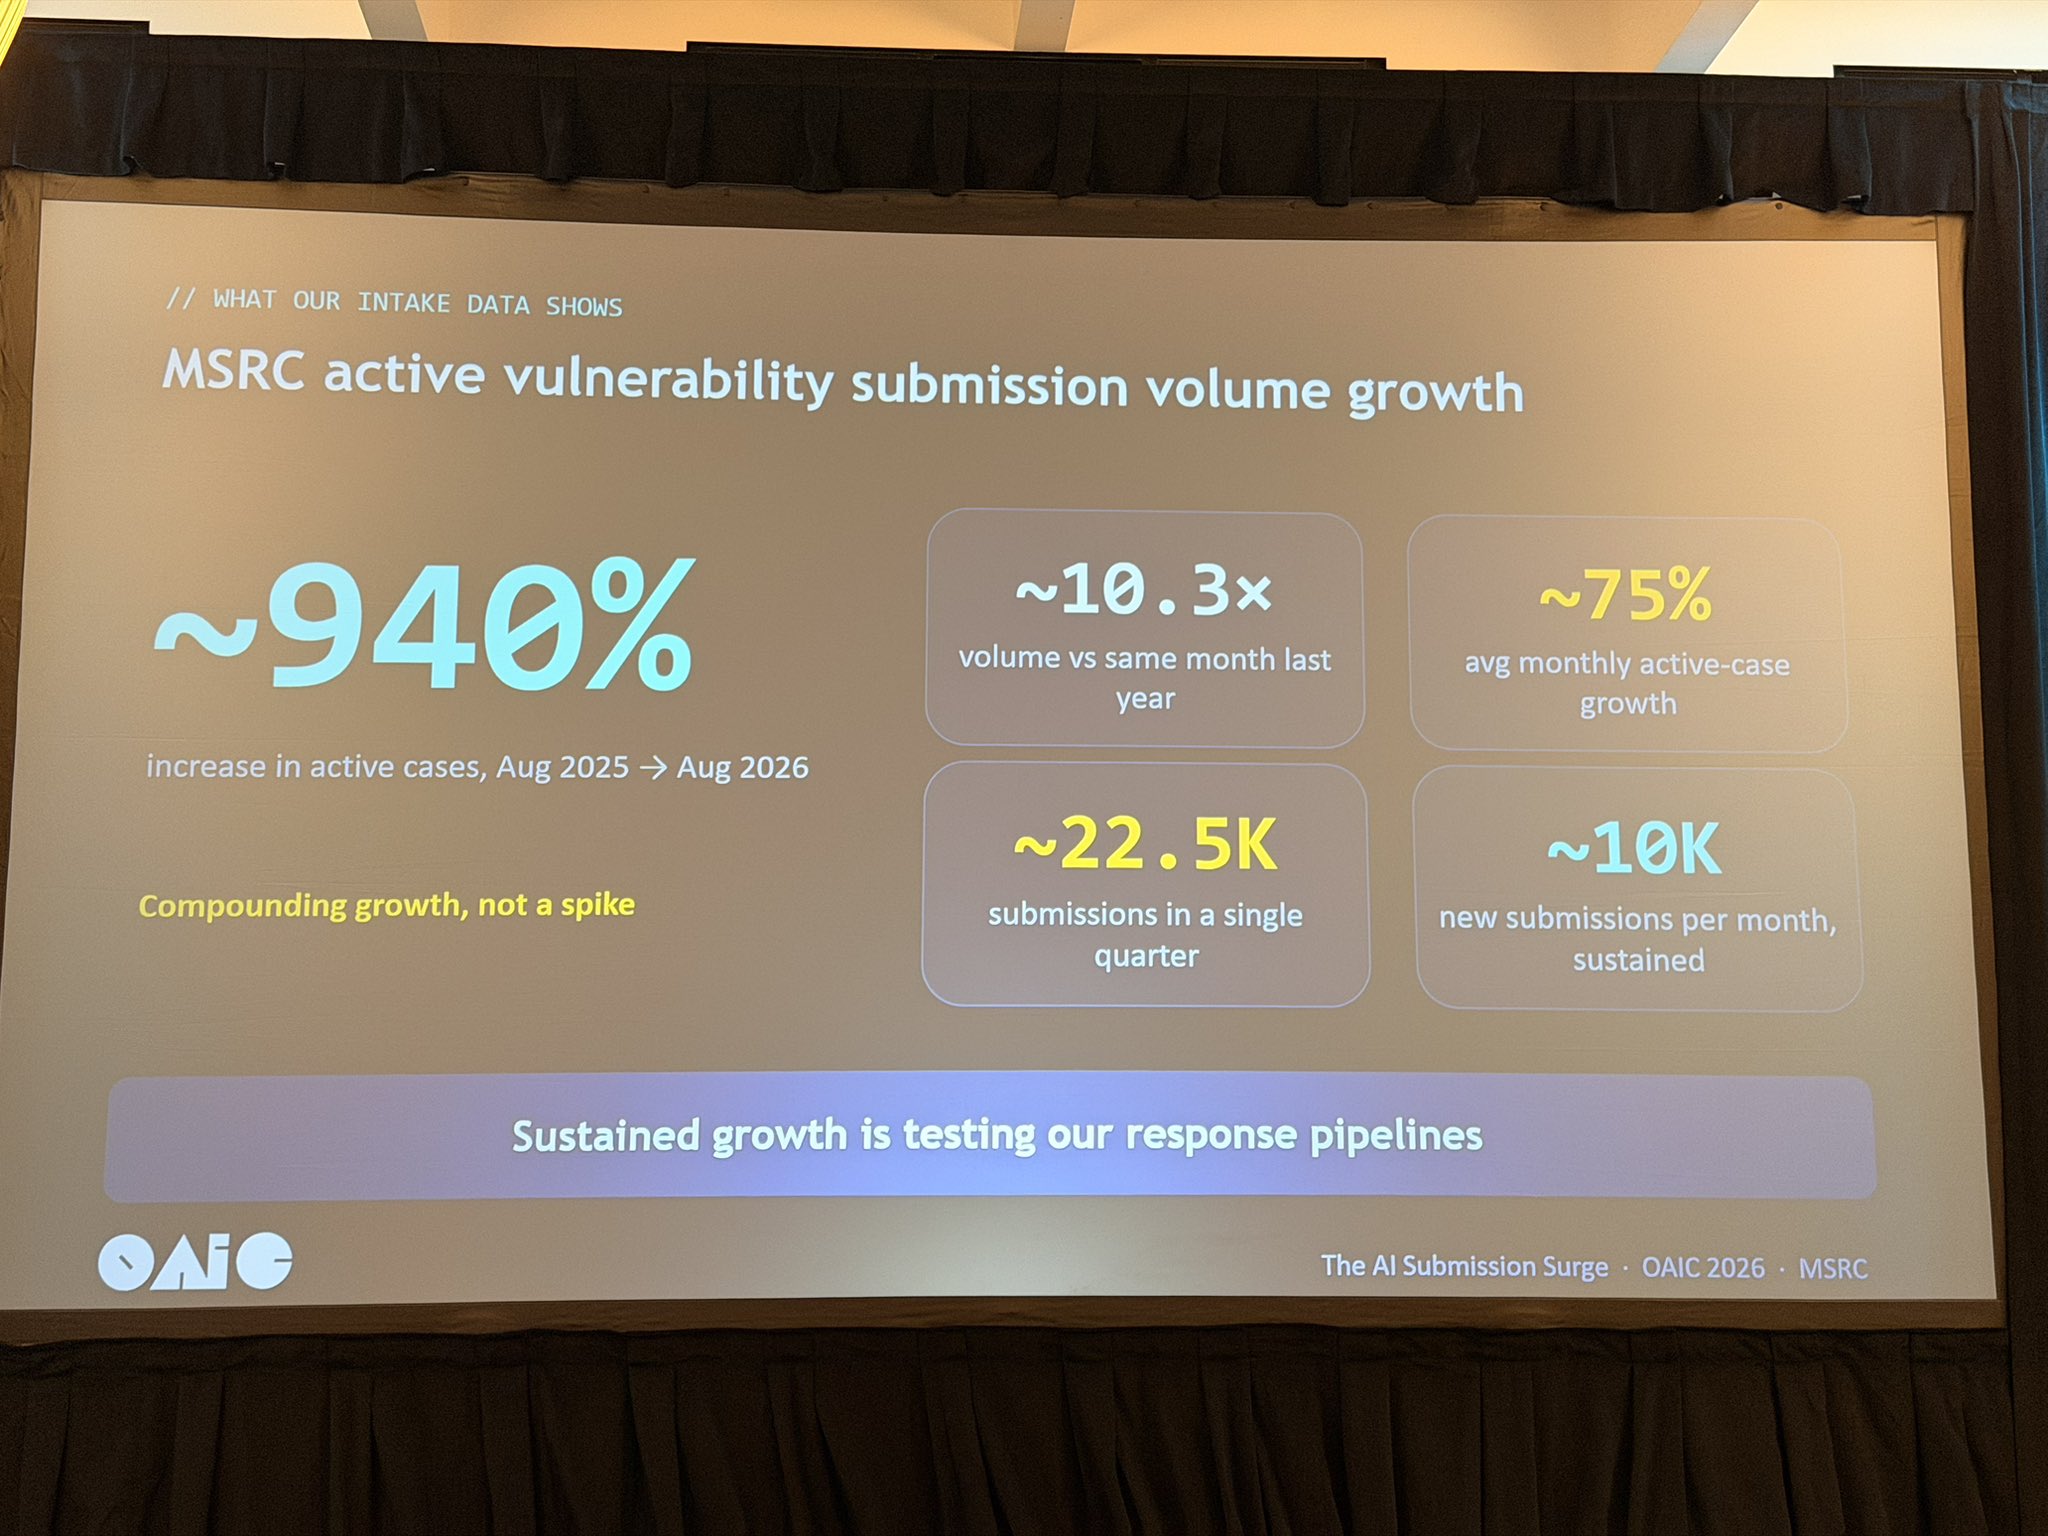
We just received a $250,000 Chrome Full Chain bonus! 🎉
We've claimed the second Full Chain bonus of 2026. Only two remain!
Under the rules, every vulnerability had to be a non-duplicate 0-day, and the entire exploit chain had to be completed before any of them were patched.
Huge thanks to @nebusecurity for discovering a V8 vulnerability in just a single day! Also, a big thank you to @_deayzl for collaborating with me on the V8 Heap Sandbox research.
P.S. KVM escapes have been getting a lot of attention. I actually captured the Full VM Escape flag in KVMCTF about three months ago. Hopefully, I'll be able to share that research soon, too!


Faav retweeted

Our research team discovered two vulnerabilities in Discourse: a pre-authentication cache poisoning to sitewide XSS (CVE-2026-55674), and an arbitrary file read (RCE) chaining a JPEG race condition with ImageMagick and Ghostscript (CVE-2026-55420). You can read more here:

ALT https://www.slcyber.io/research/a-jpeg-a-race-and-a-ghost-breaking-discourses-image-pipeline
Faav retweeted
A lot of speculation on if KVM bugs have gotten cheaper, and why id do it for 50k instead of a milly. I wasn't born yesterday. I know I couldve sold it for waayy more. I didnt want to. I did it for the love of the game. I wanted to know if I could do it, and now we know i can. Maybe I am a big dreamer?

Faav retweeted
Building on my research, my colleague @Alex_______C exfiltrated a 600-character hex token instantly using just background images and selectors. No recursive imports.