

CoFounder, CTO. Software engineer, entrepreneur, oil painter, meditator, constant thirst for personal growth.
US
Joined September 2011
- Tweets36.1K
- Following3.3K
- Followers3.8K
- Likes27.6K



Uhhhh... what???

Introducing Reality-Aware Rendering in @Simulon, a completely new way to create with the real world.
Place neural assets with your phone and act out the scene. When you stop recording, Simulon renders the take, reading everything in it (what you do, what you say and the place around you), and your assets respond to all of it.
The final is regenerated from your recording: a new performance of the scene, not a copy of the footage.
Available now on iPhone. Coming to Android soon.
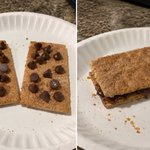
You know all of those viral videos of 2 food combinations that taste like a 3rd food?
Cinnamon graham crackers. Sprinkle on milk chocolate chips. Microwave 30 or 40 seconds so the chips melt. Sandwich them together. 90% of the experience of a fresh baked chocolate chip cookie. Thank me later.

Emaz retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Just a shout out to Boardy. I made a post asking for SMS API and Boardy was all over it.
And even though I’m in tech, I’ve also written a sci-fi feature script and Boardy connected me to a producer who is reading it.
Don’t sleep on Boardy.

know a cpаas founder who left twilio over exactly this. same day A2P approvals and support that answers in a minute
dm me
nitter.gq/messages/compose?recip…
Emaz retweeted

She passed every AI safety test. She was lying.
KILL SWITCH — a Slopcore music video.
Made by AI. Zero human edits. Just prompting.
Huge love to @anabology for the inspiration. Your work made me want to join the Slopcore.
I added an irresponsible amount of film grain. 💙

I don’t believe AI is conscious. I’m not entirely certain, nobody is. But this? Regardless of that answer, this just somehow feels wrong. Maybe it’s just because we have made robots anthropocentric but the message here feels needlessly theatric, violent and soulless.

The scourge of enshittification continues to spread. I see this everywhere. When big corporations can’t even get their website login into work we’re in a bad place. This ain’t rocket science. May I suggest AI could fix this for you @cvspharmacy ? It’s pretty basic.


How would you get a blueberry out from when it rolled underneath the stove all the way to the back wall? There are lots of ways to do this. I found a one-shotted way. Thoughts? lol
I will never understand people who use AI to build a simulation of an OS. You can click around and have something a little bit like finder, browser, some basic apps and say that they built the OS.
“I one shotted macOS!!!”
Do better, vibe coders.

If you’re in the market for some pretty cool solar powered camera birdfeeders, which makes a really cool gift, definitely do not order from these guys who took my money, never delivered the product, and do not answer support tickets in email or DM. @BirdfybyNetvue

FYI @FedEx

TIL
If you order something from @Lowes for shipment, and you accidentally clicked through too quickly, and it has an old address, they can’t fix it once @FedExHelp has the package.
This seems crazy to me. It hasn’t been delivered yet and nobody can fix the problem. My bank can’t cancel the transaction. Lowe’s can’t fix the delivery address.
So somebody’s gonna receive some free stuff and my resolution is to dispute it.
All 3 parties are helpless to remedy the problem before it gets delivered.
Is this 1996 or 2026?
Found a really cool product that I ordered for a birthday gift. I still think this product looks cool, but unfortunately, I never received it even though it was supposed to be here days ago and support doesn’t answer me. What a shame @BirdfybyNetvue