
Computer forensics, computer forensics tool validation, etc. https://xitter.cf/t.co/vlNuwLiLI7 https://xitter.cf/t.co/vYcKnqlN8Z @errno_fail@infosec.exchange 🕊
/
Joined November 2016
- Tweets959
- Following61
- Followers1.5K
- Likes7




Maxim Suhanov retweeted
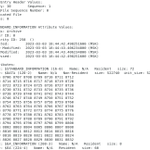
This registry key contains some values with LZNT1-compressed data. One example (raw value data + decompressed data) is shown on the screenshots attached. This key can't be opened on a live machine even by an administrator.


Maxim Suhanov retweeted
Thus, a question: is "HKLM\Software\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\CIT\System" a well-known artifact? 3/3
Maxim Suhanov retweeted
1. Live images of Ubuntu aren't forensically sound and your remastering scripts don't make these images forensically sound.
2. The dcfldd tool can't properly acquire drives with faulty sectors (also, it's deprecated).
3. I need to pay $$$ to Google to test this project.
Maxim Suhanov retweeted
This is crazy: "customers should be offered known good methods before anything else is considered". One of the most conservative ways to acquire digital evidence is to image a hard disk drive using a hardware write blocker. Still, there is no evidence that such a method is good.
Maxim Suhanov retweeted
The hive backups are disabled in the kernel by default. To override:
HKLM\SYSTEM\CurrentControlSet\Control\Session Manager\Configuration Manager, EnablePeriodicBackup -> 1 (type: DWORD)
#DFIR

Maxim Suhanov retweeted
All my Registry tools are now transaction log aware. Updated versions will be out Wednesday to coincide with webinar on Registry Explorer. Tools will either prompt you for LOG files (Registry Explorer) or expect them to be in the same directory as hives (everything else) #DFIR


Maxim Suhanov retweeted
They were one step away from discovering that it is possible to write to the source drive (the write blocker contains no write blocker).
Maxim Suhanov retweeted

About bam key (execution trace?) (2) & registry transaction log.
padawan-4n6.hatenablog.com/e…
#dfir
Maxim Suhanov retweeted
1. The 'blockdev --setro <device>' and 'hdparm -r1 <device>' commands do not write block a drive (you need a kernel patch for that to work as expected).
2. An operating system may write to a drive before you mark the block device as read-only (example: LVM activation).
Maxim Suhanov retweeted
Also:
- a code execution exploit for the LinEn CD ("let's apply KNOPPIX updates from a suspect drive automatically during the boot");
- an issue with the TD3 firmware: a write through a "write blocked" port when attaching an evidence drive (a bug + no write blocking component).
Maxim Suhanov retweeted

Maxim Suhanov @errno_fail DefensiveTrack:"In-depth forensic analysis of Windows registry files"
2017.zeronights.org/report/d…
#ZeroNights 2017