


Flysec Corp retweeted

We just launched @Vigolium a high-fidelity vuln scanner in Go, fully open source
Built it to stop drowning in false positives:
⚡ 250+ native scan modules, low-noise by design
🔍 AI agents that thoroughly audit traffic + source code
🛠️ CLI · Beautiful UI · traffic ingestor
Want your app to have proper security audit? Give it a try at github.com/vigolium/vigolium

ALT https://www.vigolium.com/

ALT https://docs.vigolium.com/

ALT Vigolium UI
Calling all 🇻🇳 BUG BOUNTY HUNTERS to participate in 🔥 VIETNAM LHE WARM UP 2026 – HACKERONE 🔥
🗓️Schedule:
- 05/01/2026: Kickoff
- 10/01/2026: Sharing & Collaboration
- 24/01/2026: Closing Ceremony & "Show & Tell"
Register: h1.community/e/m6r8cn/
Contact: @LamScun @haxor31337

Thrilled to welcome our Spanish friends - elite global bug bounty hunters to Flysec office ❤️🔥🇪🇸🇻🇳

1
31
2,224
The first-ever "Flysec Hack Trip" #FSHT49, has ended, and what an incredible 10 days it was! This #FSHT49 was just for Flysec members only and our members embarked on a journey to the beautiful city of Da Lat, Vietnam where they combined their passion for hacking with the serene landscapes and cool weather:
⚔️ This exclusive event brought together Flysec members to compete in teams, focusing their skills on a single, challenging target: a product from Zoom. Over the course of the trip, participants demonstrated incredible collaboration and ingenuity. Their hard work paid off with a remarkable total of 33 submissions, a testament to the high level of talent and dedication within our community.
❤️🔥 But it wasn't all just hacking. The trip was filled with joyful moments—from team outings to exploring the city's scenic spots.
In short, the Flysec Hack Trip is more than just a competition. It’s a chance to build a community, solve complex problems, and create lasting memories with other cybersecurity enthusiasts, all while traveling.
🚀 The next "Flysec Hack Trip" event will come soon and open for more hackers/bug bounty hunters. Waiting for our announcement!


Flysec member made a splash in Q2 @Hacker0x01 🔥💪

Q2 was a blast for me!
Somehow reached Top 5 in @Hacker0x01 Leaderboard 🤪
Reached Top 5 in Highest Critical Reputation 🪲
Reached Top 3 in Web Application Asset Types 😁
Worked & played hard with my teammate @flysec_corp ❤️🔥
Let's see how it goes in Q3! 🤓
#TogetherWeHitHarder


Flysec Team now has total more than 70k H1 reputation for members, we believe flysec will have total more than 100k reputation this year #Hackerone, #BugBounty 🔥😎

Happy to reach 15000 reputation checkpoint on @Hacker0x01
Thanks @Hacker0x01 for always be a best platform for Bug Bounty Hunters 🙌
And a big thanks to @flysec_corp . I never could have come this far without you ❤️🔥

26
1,992

🥳 I'm in the Top 10 on @yeswehack for May 2025!
This community makes hacking fun and meaningful — thank you all!
Let’s keep hacking happy 💻✨
yeswehack.com/ranking?year=2…

11
984
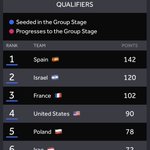
Our journey AWC2024 has ended in Quarter Finals against🇪🇸
Beyond all, Flysec & 🇻🇳 had amazing hack/chill moments together & w people from diff teams, especially our rivals 🇪🇸- our awesome new friends! Shoutout @Hacker0x01 for the great event in Prague, 🇨🇿!
We will rise again🔥💪


Congrats🇻🇳squad's good win with 2nd highest score in the 1/8 finals of the #AmbassadorWorldCup, secure a spot in the Elite Eight round at Prague, 🇨🇿!
🔥Flysec has a great hacking experience in AWC 1/8 finals being in Top 1 of Report Leaderboard!
Fighting for semi-final spot!


Flysec Corp retweeted

Thrilled to release my latest research on Apache HTTP Server, revealing several architectural issues! blog.orange.tw/2024/08/confu…
Highlights include:
⚡ Escaping from DocumentRoot to System Root
⚡ Bypassing built-in ACL/Auth with just a '?'
⚡ Turning XSS into RCE with legacy code from 1996
FlySec 1000 reports of effort & hard work, 40% reports rewarded.
We continue learn & improve essential skills to develop on bug bounty, increase the report ratio & enhance the severity.
Thanks all platforms
Thanks for following FlySec
❤️🔥FlySec try our best to save the internet


On this day 4 years ago, I was rewarded my first bounty ( for a Full path disclosure 😂 ). After that moment, everything changed dramatically. I really enjoy this journey 🥰.
To celebrate this, I get my first CVE CVE-2024-39693 recently.
github.com/vercel/next.js/se…
Happy hacking!

13
1,727
#FlySecCollab: FlySec & @ngocdh have just made a cool collaboration winning the total bounty of $11320. Cheers 🥂
Collaboration is 🔑 & ❤️🔥 #bugbountytips
❤️🔥 FlySec try our best to save the internet
🇻🇳 are trying our best and enjoy hacking at #AmbassadorWorldcup @Hacker0x01 !
Great to collaborate with all 🇻🇳 members !


#Flysec #TogetherWeHitHarder
❤️🔥FlySec try our best to save the internet
Just received a feedback with nice words from @scarybeasts @Hacker0x01 🤓 this is a big motivation for me and @flysec_corp to keep finding impactful bugs to make the Internet safer 🔥🔥


12
1,578
Flysec Corp retweeted

⚠️⚠️ CVE-2024-29269: TELESQUARE TLR-2005KSH Router vulnerable to unauthenticated OS command execution
🎯50K+ Results are found on the en.fofa.info nearly year.
FOFA Link🔗:en.fofa.info/result?qbase64=…
FOFA Query: app="TELESQUARE-TLR-2005KSH"
Refer🔖: github.com/wutalent/CVE-2024…
PoC🔖:gist.github.com/win3zz/c2604…
#OSINT #FOFA

Flysec Corp retweeted

🔎 A simple recon checklist I follow (not in order)
- Shodan/Google/Bing Dorking
- Check JS files
- Subdomain enumeration
- Wayback URLs
- Content Discovery
- Vhost Scan
- Port Scan
- GitHub Search
What more would you add to the list?
Flysec Corp retweeted

step1> echo "target.com" | waybackurls | gf xss | uro | httpx -silent | Gxss -c 100 -p Rxss -o xss.txt
step2> python3 knoxnl.py -i /root/xss.txt -A API-KEY
question- Am I following the correct steps?
@KN0X55 @lu3ky13 @Rohan_Lew @Jhaddix

Congrats our great member @LamScun on being selected as a new HackerOne Ambassador representing Vietnam 🇻🇳 along with @haxor31337
❤️🔥@LamScun and @flysec_corp try our best to hack/secure harder together with 🇻🇳 hackers!

The 2024 Brand Ambassadors are ready to kick off the year right! 🙌 Thank you to everyone who submitted their applications to the program this year.
Check out the thread below to see our newest ambassadors, and sign up on h1.community to join your local chapter! 🌎

Insecure Direct Object Reference (IDOR) with Unpredictable IDs - Effective April 2nd, 2024
Multiple Reports Highlighting Systemic Issues - Effective April 2nd, 2024
...
docs.hackerone.com/en/articl…
@Hacker0x01 #bugbountytips
