
building security at https://nitter.gq/t.co/mBie3u14lP
France
Joined April 2010
- Tweets435
- Following1.1K
- Followers549
- Likes4K
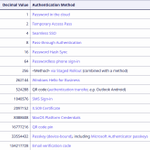

The #UserAuthenticationMethod field of the Microsoft 365 sign-in logs contains numeric values (16, 272, 33554432...) that were not documented anywhere.
I figured out that it's a bitfield, and recovered the meaning of most of the bits!


The results and methodology are detailed on the @sekoia_io blog:
blog.sekoia.io/userauthentic…
Several bits remain unmapped (bits 5, 7, 9-17, 22, 26). If you observe these values, please share your findings!

TIL about RequestType=WindowsAuthenticationController:usernamemixed in M365 UAL.
Looks like it's only used by credential testing campaigns/tools 👀
The technique was documented years ago by @DrAzureAD:
nitter.gq/DrAzureAD/status/14432…

The original @Secureworks's threat analysis report out now 🔥
secureworks.com/research/und…
I'm happy to answer to any questions regarding the technical details.
Shout-out to @SantasaloJoosua for finding the usernamemixed endpoint back in 2019!

Thank you Microsoft for that undocumented "Augmentation Loop" app using a cute "node-fetch/1.0" User-Agent.
That sure makes looking at the Sign-in logs more exciting!
(AppId: 4354e225-50c9-4423-9ece-2d5afd904870)
And actual thanks to @merill for maintaining his great Microsoft First Party App directory, my go-to reference for obscure AppIds.
github.com/merill/microsoft-…

2
283
Great blog post by Proofpoint's @threatinsight team on HTTP Client User-Agents associated with Account Takeover attacks!
I've also observed the following:
- python-httpx/*
- fasthttp
- python-urllib3/*
- GuzzleHttp/*
- and... no User-Agent at all!
proofpoint.com/us/blog/threa…

Many #AiTM phishing kits have User-Agent quirks that can be leveraged to detect compromised sign-ins.
#Sneaky2FA, an emerging PhaaS that @crep1x and I identified in December, is a good illustration of this detection method!

🔍 TDR analysts discovered a new Adversary-in-the-Middle (#AiTM) #phishing kit, specifically targeting Microsoft 365 accounts and circumventing 2-step verification: Sneaky 2FA
blog.sekoia.io/sneaky-2fa-ex…
#detection #sneaky2fa

We were scooped by @TRACLabs_ @RussianPanda9xx, who described the kit in December, as #WikiKit!
trac-labs.com/wikikit-aitm-p…
1
2
125
Cuckoo is back with another fake homebrew website
brewmacos[.]com
C2: 185.62.56[.]131
@birchb0y @AdamJKohler @L0Psec @IntegoSecurity
Great post by @rmceoin about #Adspect, the shady anti-bot service used by #Mamba2FA
rmceoin.github.io/malware-an…
151
If you work in a SOC, you have likely seen these M365 phishing pages since the beginning of the year 👇
At Sekoia.io, we have been detecting this phishing kit every week in customers environments for months!

It didn't match any of the AiTM kit we knew, so I decided to investigate in depth!
Turns out this is a new entrant on the #PhaaS market, that has been growing in popularity since November 2023.
The result of this investigation is my first article on @sekoia_io's blog 🎉
1
3
980
I am baffled.
Comparing Entra SignInLogs and M365 Audit log:
M365 logs say that device
- IsCompliant when it is managed, regardless of whether it is compliant
- IsCompliantAndManaged when it is compliant, regardless of whether it is managed
Am I misunderstanding?
@rucam365 @fabian_bader @NathanMcNulty sorry to bother you, have you observed this? Or am I making a mistake?
1
1
142
I had missed the fact that this guy was still around. That’s a shame.
Looks like his new service runs on a NakedPages fork.
abc.net.au/news/2024-08-01/a…

1
2
217
👀 The main cluster of Dadsec PhaaS pages (Storm-1575) is starting to use the .su TLD for their domains
56ovdl4w0z1a3q9.7504m8h[.]su/5l7v/
trj520p67yd9fqk.isfc10y[.]su/3xbu/
7h1vjaneo02rmql.cfbcbuf[.]su/buh9/
u7lqipyrkej40d5.5d7o289[.]su/dc09/
@josh_penny @Jane_0sint
Most of the major phishing-as-a-service platforms/kits rely on @Cloudflare services to hide their infrastructure:
- NakedPages (Storm-1101): Workers + Turnstile
- Caffeine (Storm-0867): CDN + Turnstile
- Dadsec OTT (Storm-1575): CDN + Turnstile
(notable exception is EvilProxy?)
I wish Cloudflare was more proactive in taking down this type of abuse.
Especially since they acquired @Area1Security and have now their own email security offering!
These platforms/kits can be tracked, each has unique characteristics.
The improved shell script used by the new version of #ESXiArgs has been shared by an user from the @BleepinComputer forums.
virustotal.com/gui/file/ae4b…
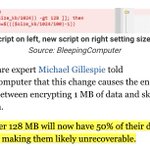
The change is small but prevents the recovery technique that worked with the first version.
@LawrenceAbrams has published a great explanation of the change:
bleepingcomputer.com/news/se…

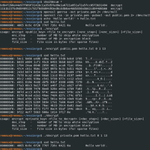
Looks like this file is the actual #ESXiArgs decryptor!
bdb4f2b6e44e97f989f3141bc1a35d5fed9e1a6721e851a72a5fcc05f3b31494
(You still need the private key!)
Demo:


Does anyone know what this “decryptor” is? Did anyone publish this?
It’s very similar to the #ESXiArgs binary but has a usage help text that indicates it can be used for decryption.
Turns out it's the decryptor!
nitter.gq/gregclermont/status/16…

Looks like this file is the actual #ESXiArgs decryptor!
bdb4f2b6e44e97f989f3141bc1a35d5fed9e1a6721e851a72a5fcc05f3b31494
(You still need the private key!)
Demo:
1
192
Alleged #ESXiArgs #ransomware samples
Encryption software binary:
virustotal.com/gui/file/11b1…
Shell script:
pastebin.com/y6wS2BXh