

House of Pentesters Join us: https://xitter.cf/t.co/Y6XOlSP7YA
Delhi
Joined September 2009
- Tweets21.1K
- Following489
- Followers312K
- Likes19.6K






🔥 Preparing for OSCP? Build practical pentesting skills with Ignite Technologies!
🔎 Enumeration & Recon
💻 Web & Network Exploitation
🔐 Privilege Escalation
🖥️ Active Directory Pentesting
🧩 Hands-on Labs & CTFs
🎓 Interested in a FREE Demo Session?
👉 Register here: forms.gle/bowpX9TGEs41GDG99
💬 Comment “OSCP” or DM us to learn more!
#OSCP #CyberSecurity #PenetrationTesting #EthicalHacking


Burp Suite for Pentester: Logger++
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
Logger++ is a powerful Burp Suite extension that captures and analyzes all HTTP requests and responses during web application testing. It helps pentesters filter, search, and analyze traffic efficiently to uncover hidden vulnerabilities.
⚡ Key Features of Logger++
📡 Capture complete HTTP traffic logs
🔎 Query-based filtering for precise analysis
🎨 Color-coded log highlighting
🧩 Regex-based search for sensitive data
📤 Export logs for reporting and analysis
🎯 Useful Detection Scenarios
🔐 Sensitive parameters (passwords, tokens)
📂 Exposed files or configuration leaks
🌐 Server information disclosure
🔄 URL redirection parameters
⚠️ CORS misconfiguration
📖 Article: hackingarticles.in/burpsuite…
#CyberSecurity #EthicalHacking #BurpSuite #Pentesting #BugBounty #InfoSec #WebSecurity


Burp Suite for Pentester: Autorize
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
Autorize is a Burp Suite extension that automates authorization testing by replaying requests with different user tokens to identify access control flaws in web applications.
📚 Vulnerabilities Detected with Autorize
🔐 Broken Access Control
🆔 Insecure Direct Object Reference (IDOR)
👥 Horizontal Privilege Escalation
⬆️ Vertical Privilege Escalation
📂 Forced Browsing
🧠 Business Logic Flaws
⚠️ Insufficient Authorization
📚 Topics Covered in This Guide
⚙️ Installation & Setup
🧩 Configuration & Filters
📡 Request/Response Analysis
🔄 Token & Cookie Replacement
🎯 Authorization Testing Workflow
📊 Interpreting Results (Bypassed / Enforced)
📖 Article:
hackingarticles.in/burpsuite…
#CyberSecurity #EthicalHacking #BurpSuite #Pentesting #BugBounty #WebSecurity


Web Application Docker Labs Cheat Sheet
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
Docker-based vulnerable web applications are widely used by pentesters and security learners to practice web exploitation techniques in an isolated environment. Docker makes it easy to deploy vulnerable labs without installing multiple dependencies.
⚡ Popular Web Application Docker Labs
🐛 DVWA (Damn Vulnerable Web Application)
🍹 OWASP Juice Shop
🐐 OWASP WebGoat
🐝 bWAPP (Buggy Web App)
🐞 OWASP Mutillidae II
⚡ DVNA (Damn Vulnerable Node Application)
🧩 Security Shepherd
🧠 Vulnerable Web Application Lab
🧠 Mindmap:
github.com/Ignitetechnologie…
#CyberSecurity #WebSecurity #Pentesting #Docker #EthicalHacking #BugBounty #InfoSec


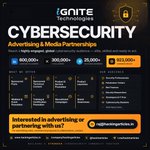
🔐 Reach 900,000+ Cybersecurity Professionals & Enthusiasts
Are you a Cybersecurity Vendor, SaaS Company, Security Product, or Technology Brand looking to reach a targeted cybersecurity audience?
HackingArticles offers advertising and media partnership opportunities to help brands connect with cybersecurity professionals, developers, security researchers, and enthusiasts.
📊 OUR COMMUNITY REACH
💼 LinkedIn: 600,000+ followers
🐦 X / Twitter: 300,000+ followers
📲 Telegram: 23,000+ members
🚀 ADVERTISING & PARTNERSHIP OPPORTUNITIES
We collaborate with brands on:
🔹 Cybersecurity Products & Security Tools
🔹 SaaS & Developer Security Solutions
🔹 Training Programs & Certifications
🔹 CTFs, Conferences & Security Events
🔹 Webinars & Technical Campaigns
🔹 Cybersecurity Recruitment & Job Campaigns
🔹 Product Launches & Brand Awareness
🔹 Sponsored Technical Articles
🔹 Long-Term Media Partnerships
🎯 REACH THE RIGHT AUDIENCE
Our community includes penetration testers, ethical hackers, Red Teamers, security researchers, SOC professionals, developers, IT professionals, and cybersecurity students.
If your brand serves the cybersecurity industry, let's explore a partnership that aligns with your audience and marketing goals.
📩 Advertising, Sponsorships & Media Partnerships
Email: [email protected]
🌐 hackingarticles.in/
🔗 LinkedIn: linkedin.com/company/hacking…
🐦 X: xitter.cf/hackinarticles/
📲 Telegram: t.me/hackinarticles/
🤝 Let's build a stronger cybersecurity community together.
#Cybersecurity #InfoSec #CyberSecurityMarketing #B2BMarketing #CybersecurityAdvertising #MediaPartnerships #SaaS #EthicalHacking #PenetrationTesting

🔥 Preparing for OSCP? Don't Just Study the Exam. Learn to Solve the Challenges.
🎓 Interested in a FREE Demo Session?
Register here:
forms.gle/bowpX9TGEs41GDG99
Knowing the tools is one thing. Knowing how to approach an unfamiliar machine, troubleshoot when you're stuck, and find a way forward is what makes practical penetration testing challenging.
At Ignite Technologies, our OSCP-Focused Training helps you strengthen your hands-on skills through:
🔎 Enumeration & Reconnaissance
💻 Web & Network Exploitation
🔐 Linux & Windows Privilege Escalation
🖥️ Active Directory Pentesting
🔴 Post-Exploitation & Pivoting
🧩 Hands-on CTFs & Practical Labs
🎯 OSCP-Focused Methodology
📝 Exam-Oriented Practice & Troubleshooting
The goal isn't just to memorize techniques. It's to develop the mindset to approach unfamiliar challenges systematically.
Before your OSCP exam, ask yourself:
👉 Can you enumerate a target methodically?
👉 Can you troubleshoot when your initial approach fails?
👉 Can you identify and exploit weaknesses independently?
If you want to strengthen these skills through practical training, explore our program.
🔗 Explore the OSCP-Focused Program:
ignitetechnologies.in/ctf-ad…
💬 WhatsApp:
wa.me/message/HIOPPNENLOX6F1
📧 Email: [email protected]
💬 What's the most challenging part of OSCP preparation for you—Enumeration, Privilege Escalation, or Active Directory?
Share your answer in the comments. If you'd like guidance on the training, comment “OSCP” or send us a DM.
#OSCP #OSCPPreparation #PenetrationTesting #EthicalHacking #CyberSecurity #ActiveDirectory #RedTeam


No CVE. No credential dump. One Windows privilege → Local Admin. 👀
🔥 SeTcbPrivilege: “Act as part of the operating system”
When this powerful privilege is assigned to the wrong user, it can create a serious Windows privilege escalation path. ⚠️
📚 In This Guide
🔍 Understand SeTcbPrivilege & Windows TCB
⚙️ Configure the Privilege via Group Policy
📋 Enumerate with whoami /priv
🌐 Validate Privileges over WinRM
🛠️ Explore the tcb-lpe Technique
🔑 Understand SYSTEM-Context Operations
🚀 Escalate a Domain User to Local Administrator
📊 Detect Event IDs 4672, 4673 & 7045
🛡️ Apply WDAC & Least Privilege Hardening
💡 One misconfigured Windows user right can completely change the security boundary of a system.
📖 Read the Full Guide:
hackingarticles.in/windows-p…
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
#SeTcbPrivilege #WindowsPrivilegeEscalation #ActiveDirectory #RedTeam #Pentesting #CyberSecurity #WindowsSecurity #EthicalHacking #InfoSec


🚨 One Windows Privilege. One Misconfiguration. SYSTEM Access. 🔥
SeRestorePrivilege is designed for backup & restore operations...
But when abused, it can become a powerful Windows Privilege Escalation vector.
In this hands-on lab you'll learn:
🔓 What SeRestorePrivilege is
⚡ Why it matters
🛠️ Practical exploitation
💥 Real-world privilege escalation
🛡️ Detection & Mitigation
📖 Read the complete walkthrough:
hackingarticles.in/windows-p…
🔥 Telegram: t.me/hackinarticles
✴️ Twitter: xitter.cf/hackinarticles
⭐ Bookmark it for your Windows PrivEsc notes.
♻️ Repost to help the cybersecurity community.
#Windows #PrivilegeEscalation #CyberSecurity #OSCP #RedTeam #Pentesting #EthicalHacking #ActiveDirectory


🔥 Arsenal-NG: The Ultimate Pentest Cheat Sheet
From enumeration to exploitation, Arsenal-NG generates commands on demand, helping security professionals save time during assessments. ⚠️
📚 In This Guide
🤖 Introduction to Arsenal-NG
⚙️ Installing Arsenal-NG
🔍 Generating Reconnaissance Commands
🌐 Network Enumeration Made Easy
🛠️ Web Application Testing Commands
🎯 Active Directory Assessment Workflows
🔑 Credential Attack Command Generation
📡 Service Enumeration Techniques
🐧 Linux & Windows Pentesting Commands
🚀 Red Team & Post-Exploitation Use Cases
🧠 AI-Assisted Command Generation
📋 Practical Pentesting Cheat Sheet Examples
💡 Why remember every Nmap, NetExec, CrackMapExec, Impacket, BloodHound, or Metasploit command when you can generate them instantly? Arsenal-NG acts as a smart command assistant, helping pentesters quickly find the right syntax and workflow during authorized security assessments.
📖 Read the Full Guide:
hackingarticles.in/arsenal-n…
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
#ArsenalNG #Pentesting #RedTeam #CyberSecurity #EthicalHacking #InfoSec #ActiveDirectory #Nmap #NetExec #AI


🔥 Preparing for OSCP? Don't Just Study the Exam. Learn to Solve the Challenges.
🎓 Interested in a FREE Demo Session?
Register here:
forms.gle/bowpX9TGEs41GDG99
Knowing the tools is one thing. Knowing how to approach an unfamiliar machine, troubleshoot when you're stuck, and find a way forward is what makes practical penetration testing challenging.
At Ignite Technologies, our OSCP-Focused Training helps you strengthen your hands-on skills through:
🔎 Enumeration & Reconnaissance
💻 Web & Network Exploitation
🔐 Linux & Windows Privilege Escalation
🖥️ Active Directory Pentesting
🔴 Post-Exploitation & Pivoting
🧩 Hands-on CTFs & Practical Labs
🎯 OSCP-Focused Methodology
📝 Exam-Oriented Practice & Troubleshooting
The goal isn't just to memorize techniques. It's to develop the mindset to approach unfamiliar challenges systematically.
Before your OSCP exam, ask yourself:
👉 Can you enumerate a target methodically?
👉 Can you troubleshoot when your initial approach fails?
👉 Can you identify and exploit weaknesses independently?
If you want to strengthen these skills through practical training, explore our program.
🔗 Explore the OSCP-Focused Program:
ignitetechnologies.in/ctf-ad…
💬 WhatsApp:
wa.me/message/HIOPPNENLOX6F1
📧 Email: [email protected]
💬 What's the most challenging part of OSCP preparation for you—Enumeration, Privilege Escalation, or Active Directory?
Share your answer in the comments. If you'd like guidance on the training, comment “OSCP” or send us a DM.
#OSCP #OSCPPreparation #PenetrationTesting #EthicalHacking #CyberSecurity #ActiveDirectory #RedTeam

🚨 Impacket = One of the Most Powerful Toolkits for AD Pentesters. 🔥
If you're learning Active Directory pentesting, you NEED to understand Impacket.
It provides a collection of Python classes and tools for working with Windows/Active Directory protocols and security assessments.
🧰 Tools you should know:
🔹 secretsdump
🔹 psexec
🔹 smbexec
🔹 wmiexec
🔹 dcomexec
🔹 atexec
🔹 reg
🔹 lookupsid
🔹 GetNPUsers
🔹 GetUserSPNs
🔹 ntlmrelayx
🔹 ticketConverter
…and more.
📚 Practical Impacket resources for Pentesters:
github.com/Ignitetechnologie…
Perfect for:
🔴 AD Pentesters
🔴 Red Teamers
🔴 OSCP Students
🔴 Security Researchers
⭐ Star & Bookmark
♻️ Repost for the cybersecurity community
🔥 Telegram: t.me/hackinarticles
✴️ Twitter: xitter.cf/hackinarticles
#Impacket #ActiveDirectory #Pentesting #RedTeam #CyberSecurity #OSCP #EthicalHacking #InfoSec

Credential Dumping: AD User Comment
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
AD User Comment Password Enumeration is a technique where attackers extract sensitive information stored in user account attributes (like description/comment fields) in Active Directory, which may contain plaintext passwords or hints due to poor security practices.
📚 Topic Covered
📖 Introduction
🧠 Understanding AD User Attributes
📂 Storing Passwords in Description Field
🔍 Enumeration using LDAP Queries
🛠 Enumeration using NetExec / CrackMapExec
📦 PowerView (Get-DomainUser)
🐍 Python Scripts (LDAP Enumeration)
🔐 Extracting Credentials from Comments
🚀 Privilege Escalation using Discovered Passwords
🛡 Detection & Mitigation Techniques
📖 Article:
hackingarticles.in/credentia…
#CyberSecurity #ActiveDirectory #RedTeam #Pentesting #EthicalHacking #CredentialDumping #InfoSec


Credential Dumping: DCSync Attack
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
DCSync attack is a powerful Active Directory credential dumping technique where an attacker mimics a Domain Controller to request password hashes and sensitive data from other controllers using replication protocols.
📚 Topic Covered
📖 Introduction
🧠 Understanding DCSync Attack
🏢 Active Directory Replication Concept
🔐 Required Privileges (Replicating Directory Changes)
🛠 Mimikatz (lsadump::dcsync)
📦 Impacket (secretsdump.py)
🧪 Extracting NTLM Hashes
👑 Dumping KRBTGT Account Hash
🎟 Golden Ticket Attack
🚀 Privilege Escalation & Domain Compromise
🛡 Detection & Mitigation Techniques
📖 Article:
hackingarticles.in/credentia…
#CyberSecurity #ActiveDirectory #RedTeam #Pentesting #EthicalHacking #CredentialDumping #InfoSec


Credential Dumping: Windows Autologon Password
🔥 Telegram: t.me/hackinarticles
✴ Twitter: xitter.cf/hackinarticles
Windows Autologon stores user credentials in the registry to enable automatic login. If misconfigured, these credentials can be extracted in plaintext, making them an easy target for attackers.
📚 Topic Covered
📖 Introduction
🧠 Understanding Windows Autologon
⚙️ AutoAdminLogon Registry Setting
📂 Registry Path (Winlogon)
🔑 DefaultUsername & DefaultPassword Storage
🔍 Enumerating Autologon Credentials
💻 Dumping Credentials via Registry Query
📦 Credential Extraction Techniques
🚀 Privilege Escalation using Extracted Credentials
🛡 Detection & Mitigation Techniques
📖 Article:
hackingarticles.in/credentia…
#CyberSecurity #RedTeam #Pentesting #EthicalHacking #CredentialDumping #WindowsSecurity #InfoSec


