




Pinned Tweet
Introducing kakuchi.app for Mac
50+ live widgets for your desktop, lock screen, menu bar and notch.
Can't find one? Describe it and it's built for you, using the Claude, ChatGPT or Antigravity plan you already pay for


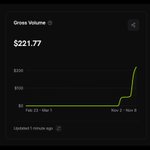
4 days later: $89.86 → $221.77
Still no big audience. Just showing up every day on Reddit and X.
Thank you to everyone who bought it, tried it, or shared feedback 🙏


It's really hard to sell a product without an audience.
First 2 weeks of trying to build one: $89.86 from kakuchi.app, live widgets for your Mac that you build by describing them

Himanshu Arora retweeted
let’s connect 🤝
now that i’ve hopefully made it to your timeline, check out kakuchi.app
build custom Mac widgets just by describing what you want. notch, menu bar, pretty much anywhere :)
really excited about this one!
Himanshu Arora retweeted
I waited for this statement, but it’s genuinely disappointing and unconvincing.
I empathized with @Railway when it was under attack a few days ago. That shouldn’t have happened, but companies grow and mature with time, and mistakes happen.
But this incident has malicious intent written all over it. Attacking a competitor and calling it “testing”, changing statements, and now seemingly throwing an employee under the bus.
The whole thing is sketchy, and this statement raises more questions than it answers.
Also, huge props to @joshmanders for the security they’ve built at @primcloud 🙌

Last night, I became aware of the concerns raised in Josh's post. I reached out publicly and over DM to offer a potential explanation based on the limited information available at the time, while working to understand what happened.
As background, we’ve internally been pushing 100% on security of the Railway platform. At Railway, we believe that cyber threats are real and mounting, and we’ve built out tooling for automatic scanning + CVE remediation (for both our infrastructure and customers). Over the last few weeks, oncall engineers were instructed to red team our infrastructure. We maintain specific policies and short lived grants for when these actions occur.
Subsequently, I became aware that an employee at Railway had constructed, on their own time, a tool for proactive identification + reporting of bug bounties within the broader community.
The employee, using their own personal accounts, personal credit card, and time outside of work hours, signed up for a personal subscription to a hosted service running Deepseek. I can confirm they ran this tool once and only once, on a singular external provider, and halted it proactively within 15 minutes of starting.
Railway does not condone these actions. We expect all our employees to uphold our standards of conduct, whether acting on behalf of Railway or in a personal capacity. We create an environment where internal red teaming has strict guidelines, and when bug bounty disclosures must occur, we follow every letter of responsible disclosure.
We have addressed this incident with the employee directly and have taken appropriate action. We are also reinforcing our expectations for employee conduct to help prevent similar situations.
Readers added context they thought people might want to know
Primcloud does not have a bug bounty program, per its founder. Its Acceptable Use Policy forbids unauthorized probing, scanning or vulnerability testing without prior written consent.
x.com/joshmanders/st…
primcloud.com/aup
let’s connect 🤝
now that i’ve hopefully made it to your timeline, check out kakuchi.app
build custom Mac widgets just by describing what you want. notch, menu bar, pretty much anywhere :)
really excited about this one!
I waited for this statement, but it’s genuinely disappointing and unconvincing.
I empathized with @Railway when it was under attack a few days ago. That shouldn’t have happened, but companies grow and mature with time, and mistakes happen.
But this incident has malicious intent written all over it. Attacking a competitor and calling it “testing”, changing statements, and now seemingly throwing an employee under the bus.
The whole thing is sketchy, and this statement raises more questions than it answers.
Also, huge props to @joshmanders for the security they’ve built at @primcloud 🙌
Last night, I became aware of the concerns raised in Josh's post. I reached out publicly and over DM to offer a potential explanation based on the limited information available at the time, while working to understand what happened.
As background, we’ve internally been pushing 100% on security of the Railway platform. At Railway, we believe that cyber threats are real and mounting, and we’ve built out tooling for automatic scanning + CVE remediation (for both our infrastructure and customers). Over the last few weeks, oncall engineers were instructed to red team our infrastructure. We maintain specific policies and short lived grants for when these actions occur.
Subsequently, I became aware that an employee at Railway had constructed, on their own time, a tool for proactive identification + reporting of bug bounties within the broader community.
The employee, using their own personal accounts, personal credit card, and time outside of work hours, signed up for a personal subscription to a hosted service running Deepseek. I can confirm they ran this tool once and only once, on a singular external provider, and halted it proactively within 15 minutes of starting.
Railway does not condone these actions. We expect all our employees to uphold our standards of conduct, whether acting on behalf of Railway or in a personal capacity. We create an environment where internal red teaming has strict guidelines, and when bug bounty disclosures must occur, we follow every letter of responsible disclosure.
We have addressed this incident with the employee directly and have taken appropriate action. We are also reinforcing our expectations for employee conduct to help prevent similar situations.
Readers added context they thought people might want to know
Primcloud does not have a bug bounty program, per its founder. Its Acceptable Use Policy forbids unauthorized probing, scanning or vulnerability testing without prior written consent.
x.com/joshmanders/st…
primcloud.com/aup
funny how i can tell someone’s a developer just by looking at their profile picture 😬
myself included
Himanshu Arora retweeted
drop your website or product below and i’ll turn it into a mac widget 👀
wanna see how many i can make
Himanshu Arora retweeted
Introducing kakuchi.app for Mac
50+ live widgets for your desktop, lock screen, menu bar and notch.
Can't find one? Describe it and it's built for you, using the Claude, ChatGPT or Antigravity plan you already pay for
drop your website or product below and i’ll turn it into a mac widget 👀
wanna see how many i can make
Himanshu Arora retweeted
pov: Apple should've built this into macOS by now
type the widget you want, it shows up on your desktop
kakuchi.app

Himanshu Arora retweeted
Didn’t expect this tweet to get this much attention, especially since it was just for fun 😬
Sharing something else I built worth checking out - kakuchi.app
Do a lot more with your mac widgets, can’t wait to hear what you all think :)
As promised, a serious product.
pagefighter.vercel.app/

One sentence → a Search Console widget
> Make a widget for my Google Search Console with clicks, impressions, CTR, position and top queries
now it just lives on my desktop


pov: Apple should've built this into macOS by now
type the widget you want, it shows up on your desktop
kakuchi.app
on a personal note, my fav quote ever, and a simple one to live by.
“this too shall pass”
whoever said this first, thank you. something i remind myself of on both good and bad days. helps me accept things and move on.
Didn’t expect this tweet to get this much attention, especially since it was just for fun 😬
Sharing something else I built worth checking out - kakuchi.app
Do a lot more with your mac widgets, can’t wait to hear what you all think :)
As promised, a serious product.
pagefighter.vercel.app/
Did @WisprFlow just sign every creator on the internet?
I cannot open YouTube, X, or Instagram without seeing them anymore.