
Head of Bug Bounties & Competitions at @cantinasecurity
Joined March 2021
- Tweets699
- Following1.7K
- Followers2.1K
- Likes1.7K




As building apps got easier, understanding how to protect yourself online should too.
People need accessible security tools and the education to use them.
Cybersecurity isn't optional anymore.
1
217
If you are coming to DSS.
See you there!

Hrishikesh Bhat · DSS 2026
“Beyond the Bounty: The Next Era of Crowdsourced Security”
Explore the talk and add it to your agenda:
defisecuritysummit.org/2026/…
Tickets: luma.com/9qtxqqxx

ALT DSS 2026 speaker announcement card for Hrishikesh Bhat: Beyond the Bounty: The Next Era of Crowdsourced Security.
4
27
908
Bug bounties are not dead!
But they need to evolve.
We are working on something special that solves some inherent problems for all actors post AI era.

more than $6 million have been awarded to security researchers hunting on the Cantina bug bounty platform.
day and night, security researchers act as the digital vanguard of the tech world, protecting millions of users, preventing catastrophic scenarios and proving how much brilliant minds of all ages can safeguard the future of technology.
we all thank you for your service.

4
334
I think there's incredible opportunity in bug bounties right now.
Do you think we should do a workshop on how to use AI to hunt for bugs?
We'll get some of our top cyborg hunters to show you how.
Everybody is focused on building AI tools to finding bugs. What drains resources for teams after a flood of findings:
1. Validation
2. Deploying fixes across services.
3. Re-testing to confirm closed.
4. Review and coordination.
5. Deciding reward on each report.
6. Repeating all of it, per report, forever.
The entire pipeline needs a well thought out agentic restructuring.
2
13
995
Read this as a triage story, not a bounty story.
Google got a flood of reports. That doesn't mean it got a flood of bugs. Past a point, report volume tells you more about the queue than the state of your security.
Nobody has solved this yet. @cantinasecurity is building for both sides of it: the teams working through that queue, and the researchers trying to get their real findings heard.

⚡ Google just paused product bug bounty rewards for some of its biggest open-source projects.
It says automated submissions surged, and the vast majority were invalid.
Go, Angular, Flutter, Bazel, and Protocol Buffers are among the affected projects. Supply chain rewards continue.
Read: thehackernews.com/2026/10/go…

Security has never been a fair fight
Attackers need one bug, defenders need to catch all of them
And attackers were never going to wait for permission.
Defenders shouldn't have to either.
Proud of our Team for this one!
today we're releasing apex-flash-1, our first open-weights model for security research post-trained on real vulnerabilities we found and got paid for.
we are also releasing the abliterated variant for researchers who want fewer refusals in their own authorized workflows.
how we built it: cantina.security/apex-flash


Hrishikesh retweeted

We spent years finding vulnerabilities before attackers did. That was the easy part.
Teams already know what's broken. Nobody has the bandwidth to close it.
Today we raised $16.5M to make Cantina the security workforce for your security workforce. cantina.review/next-chapter-…

New-dad sleep windows are fragile.
My laptop was six feet away with a Codex project running. Getting up would have killed the nap.
So I started a research task from my phone through ChatGPT Remote.
I hadn’t really used it well until today, but I’m so grateful it exists.
Thanks @thsottiaux and @Dimillian for today’s bump in my sleep score.
4
7
2,274
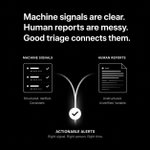
Most security alerts aren't hard to judge. Show a good engineer a well-presented alert and they'll tell you in seconds whether it's real.
The hard part is everything before that: getting the right alert to the right person, in a form they can act on, while a few hundred others land at the same time.
Source matters too. Datadog or Okta output is structured and predictable, and rules and pipelines already handle most of it. Bug bounty submissions are the opposite raw, unstructured, and each one has to be reproduced and turned into something a team can work with.
Volume is growing on both sides, and they increasingly need to be triaged together. Rules can't do that. You need agents good enough to absorb the load and correlate machine signal with human reports, so engineers only spend time on the judgment calls.

AI almost broke bug bounties.
No system was built for this volume.
Time to be antifragile. Better validation, faster decisions, clearer feedback.
Raising the bar for slop. Lowering it for skill.
1
24
1,735

Was building something ambitious when Fable 5 got pulled. Two days, but the momentum felt different after. Had to fall back to an earlier approach instead.
Wild how fast we have all become dependent on these models. Technology has never spread this fast. Yet it can disappear just as quickly.
That tension is real. Exciting and strangely fragile at the same time.
🤖 Made with AI

2
475
Starting my day with @danshipper's quote:
Never make any major life decisions within 30 days of
- a meditation retreat
- a psychedelic experience
- your first encounter with a frontier model
1
4
415