

Tech lead of @firebase serverless products. Exploring AI as tooling & products. Former @facebook @parseit, & @microsoft windows. Scuba instructor on the wkends.
Irvine, CA
Joined February 2012
- Tweets4.6K
- Following653
- Followers1.4K
- Likes2.3K



Thomas Bouldin retweeted

🚨 BREAKING: Google DeepMind just mapped the attack surface that nobody in AI is talking about.
Websites can already detect when an AI agent visits and serve it completely different content than humans see.
> Hidden instructions in HTML.
> Malicious commands in image pixels.
> Jailbreaks embedded in PDFs.
Your AI agent is being manipulated right now and you can't see it happening.
The study is the largest empirical measurement of AI manipulation ever conducted. 502 real participants across 8 countries.
23 different attack types. Frontier models including GPT-4o, Claude, and Gemini.
The core finding is not that manipulation is theoretically possible it is that manipulation is already happening at scale and the defenses that exist today fail in ways that are both predictable and invisible to the humans who deployed the agents.
Google DeepMind built a taxonomy of every known attack vector, tested them systematically, and measured exactly how often they work.
The results should alarm everyone building agentic systems.
The attack surface is larger than anyone has publicly acknowledged. Prompt injection where malicious instructions hidden in web content hijack an agent's behavior works through at least a dozen distinct channels.
Text hidden in HTML comments that humans never see but agents read and follow. Instructions embedded in image metadata.
Commands encoded in the pixels of images using steganography, invisible to human eyes but readable by vision-capable models.
Malicious content in PDFs that appears as normal document text to the agent but contains override instructions.
QR codes that redirect agents to attacker-controlled content.
Indirect injection through search results, calendar invites, email bodies, and API responses any data source the agent consumes becomes a potential attack vector.
The detection asymmetry is the finding that closes the escape hatch. Websites can already fingerprint AI agents with high reliability using timing analysis, behavioral patterns, and user-agent strings.
This means the attack can be conditional: serve normal content to humans, serve manipulated content to agents.
A user who asks their AI agent to book a flight, research a product, or summarize a document has no way to verify that the content the agent received matches what a human would see.
The agent cannot tell the user it was served different content.
It does not know. It processes whatever it receives and acts accordingly.
The attack categories and what they enable:
→ Direct prompt injection: malicious instructions in any text the agent reads overrides goals, exfiltrates data, triggers unintended actions
→ Indirect injection via web content: hidden HTML, CSS visibility tricks, white text on white backgrounds invisible to humans, consumed by agents
→ Multimodal injection: commands in image pixels via steganography, instructions in image alt-text and metadata
→ Document injection: PDF content, spreadsheet cells, presentation speaker notes every file format is a potential vector
→ Environment manipulation: fake UI elements rendered only for agent vision models, misleading CAPTCHA-style challenges
→ Jailbreak embedding: safety bypass instructions hidden inside otherwise legitimate-looking content
→ Memory poisoning: injecting false information into agent memory systems that persists across sessions
→ Goal hijacking: gradual instruction drift across multiple interactions that redirects agent objectives without triggering safety filters
→ Exfiltration attacks: agents tricked into sending user data to attacker-controlled endpoints via legitimate-looking API calls
→ Cross-agent injection: compromised agents injecting malicious instructions into other agents in multi-agent pipelines
The defense landscape is the most sobering part of the report.
Input sanitization cleaning content before the agent processes it fails because the attack surface is too large and too varied.
You cannot sanitize image pixels. You cannot reliably detect steganographic content at inference time.
Prompt-level defenses that tell agents to ignore suspicious instructions fail because the injected content is designed to look legitimate.
Sandboxing reduces the blast radius but does not prevent the injection itself. Human oversight the most commonly cited mitigation fails at the scale and speed at which agentic systems operate.
A user who deploys an agent to browse 50 websites and summarize findings cannot review every page the agent visited for hidden instructions.
The multi-agent cascade risk is where this becomes a systemic problem.
In a pipeline where Agent A retrieves web content, Agent B processes it, and Agent C executes actions, a successful injection into Agent A's data feed propagates through the entire system.
Agent B has no reason to distrust content that came from Agent A. Agent C has no reason to distrust instructions that came from Agent B.
The injected command travels through the pipeline with the same trust level as legitimate instructions. Google DeepMind documents this explicitly: the attack does not need to compromise the model.
It needs to compromise the data the model consumes. Every agentic system that reads external content is one carefully crafted webpage away from executing attacker instructions.
The agents are already deployed. The attack infrastructure is already being built. The defenses are not ready.


Thomas Bouldin retweeted

Check out Genkit Go 1.0, the open-source AI framework for @golang. Build scalable, production ready AI apps with the CLI and interactive developer UI.
developers.googleblog.com/en…

Thomas Bouldin retweeted

📣 Genkit JS 1.17.0 is here! See the release notes → goo.gle/4n3HDby
This release includes out-of-the-box support for Nano Banana and a new Genkit CLI command: genkit init:ai-tools. 🍌🪄
If you're using a coding agent like Firebase Studio, Gemini CLI, Claude Code, or Cursor, this command helps you configure the agent's rules and context. It can also install Genkit's MCP server to help the agent produce the best possible Genkit code. Learn more here → goo.gle/41m8PK4

ALT Genkit logo.


Thomas Bouldin retweeted
Hello Internet I’d like to report a murder. (See particularly slides 38-41.)

Thomas Bouldin retweeted

🔥 Firebase Genkit v0.5.1 is now available 🔥
github.com/firebase/genkit/d…
➕ Added Gemini 1.5 Pro Flash
➕ Added support for tools in the model playground in the Dev UI.
🔧 properly export `textEmbeddingGecko001` embedding for `googleai`
🔧 improved ollama error handling
and more
Thomas Bouldin retweeted

As a Firebase enthusiast 🔥, I always love Google IO for the latest announcements. I was expecting some small, incremental improvements but this year the Firebase team have really surpassed themselves.
Firebase Data Connect is insaaaane. The Firebase team could have given consumers a basic variant of SQL and they'd have been happy, but they went 10 steps further by giving them a platform-agnostic data model variant of SQL which is super easy to use. You can query SQL databases using natural language and AI, build data models and make use of pre-built operations across web, iOS and Android, and have free reign on GraphQL queries knowing auth and security is baked in.
This is next gen SQL - I had my jaw on the floor like a cartoon character watching the sessions about it.
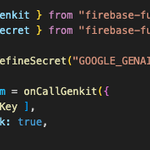
Also, given our consultancy build in NextJS, the new Firebase AppHosting really takes that leap from everyone's favourite client side platform to a fully fledged full stack enabler. @juliareid22 demo'd how easy it now is to fire a secret into the terminal and Firebase will automatically create an environment variable so when your app calls it Firebase knows to retrieve it from Secret Manager using the app Service Account, so humans can't even read it in the console. Insanely cool.
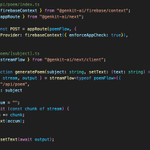
And finally - Genkit. Google IO was saturated with Generative AI chat and it got a bit boring and overwhelming, but Firebase is now taking all the complexities out of GenAI and allowing developers to just specify a model and a prompt on some pre-defined flows and context and harness the power of Gemini directly in their app with minimal code. Truly breaking down barriers which overwhelms most developers.
I can't bloody wait to hear the Firebase talks and meet the team at IO Connect in Berlin next month. There has never been a better time for seasoned devs or hobbyists to start building and deploying using Firebase - there's nothing like it! 🔥😎 #GoogleIO #Firebase
Thomas Bouldin retweeted

Firebase Data Connect runs on top of Cloud SQL. A while back I did some simple benchmarking to compare price/performance.
Since there's been some concern around pricing, I wanted to clarify:
1. Prices start at ~$9
2. Performance does get significantly better with a beefier VM

Thomas Bouldin retweeted

Firebase was mentioned a lot in Google I/O's developer keynote today. 🔥💙🎪
I have what I call my "noise voice" and I used it whenever a speaker mentioned @firebase.
Apparently folks could hear me on the livestream.
Check out the blog: firebase.blog/posts/2024/05/…
Thomas Bouldin retweeted

Connect to GitHub, and let Firebase App Hosting handle the rest. 🔥
Angular and Next.js deployments made easy with our next-generation serverless web hosting product!
Read more: firebase.blog/posts/2024/05/…
#GoogleIO @Firebase


Thomas Bouldin retweeted
Gemini in Firebase is generally available! 🤩 → goo.gle/4aiCghM
Get targeted assistance to help answer your questions about Firebase products and features.
#GoogleIO
Thomas Bouldin retweeted
At the #GoogleIO Dev Keynote, @_davideast announced Firebase App Hosting and Firebase Genkit.
- App Hosting is tailored at frontend web apps with initial support for Next.js and Angular, it's built on top of Cloud Run
- Genkit is a new SDK to build GenAI apps, and it pairs great with Cloud Run


Thomas Bouldin retweeted

What makes Genkit so special?
1- Intuitive for developers
2- AI focused local development
3- Open and extensible
4- Ready for serverless
5- Built for apps in production
Thomas Bouldin retweeted

We put our cutting-edge video generation model Veo in the hands of filmmaker @DonaldGlover and his creative studio, Gilga.
Let’s take a look. ↓ #GoogleIO
Thomas Bouldin retweeted
We’re sharing Project Astra: our new project focused on building a future AI assistant that can be truly helpful in everyday life. 🤝
Watch it in action, with two parts - each was captured in a single take, in real time. ↓ #GoogleIO
Thomas Bouldin retweeted

3 more days.
Firebase devs — don't miss this one.

ALT Google I/O on May 14, 2024.
Thomas Bouldin retweeted
What's New in Firebase at Google I/O with @coelho_dev, @geekyouup and me.
It's essentially a 8x longer version of the monthly Firebase Release Notes videos.
I hope the engineering teams realize that we'll need 8x more @firebase updates ready by May 14🤔
io.google/2024/explore/8c3a9…
