
product @unchained, wrote @primalcutsheet, passionate about bitcoin, food sourcing and health.
MPLS
Joined November 2008
- Tweets11.7K
- Following1.5K
- Followers3.7K
- Likes42.1K





Jevi retweeted

At this point, if you aren't under attack, you just haven't been found yet. We made @TryMapleAI to be the security tool that's as easy as Claude.
It has encrypted DeepSeek Uncensored that will scan your setup and work for you.
Get Maple now and add it to your toolkit.


Jevi retweeted

🚨Security Vulnerability 🚨
All nodes are affected. Patch coming later today to add mitigations and fixes where available.
Swapping to Tor-only via the settings page may help mitigate this. The better mitigation is to remove remote access to your node or temporarily shut down.
Looks like there may not be a kernel update for Raspberry Pi quite yet.
More info will be coming.

Jevi retweeted

Guy who devotes 15 hours a day to optimizing his diet and lifestyle: crippling headache in a first class lounge
Guy who’s 5 martinis deep at 8 am when he hears the last call for his flight: able to sprint a quarter mile to make it in time while holding his McDonald’s happy meal

If they can shut off withdrawals for 48 hours, what's stopping them from shutting it off for 48 days? Or 48 weeks?
Binance is a single point of failure, treat it accordingly.

**Service Update**
Deposits remain unaffected and continue to operate as normal.
Our team is currently working on enhancements to the withdrawal service and related address controls. We expect to begin resume withdrawal services in the next 48 hours.
We will continue to share updates through official Binance channels as progress is made.
Binance can cover the gap for two reasons:
1. They led retailers into degeneracy for a decade, siphoning billions in the process.
2. Many centralized shitcoins are freezing funds, highlighting that they weren't decentralized to begin with.
Don't let the PR spin fool you.

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

Jevi retweeted

"It’s called a mouse. It lets you control your computer without getting your greasy fingerprints all over the screen."

Jevi retweeted

Been working on post training models and got some cool results.
Was able to train Qwen3.8:27b to be significantly better at working with bitcoin scripts.

Jevi retweeted

Every time an AI agent asks for your files, part of you hesitates.
Maple Work is the one you don't have to second-guess. Private by design, and you can verify it.
Invites rolling out now. Get on the list. 👇


Jevi retweeted
the agent works on desktop. it has shell access, MCP, skills, ACP and more. with that, it can handle any file type.
if you want to get the beta, sign up at maple.ai/work
we’re flooding invites soon.


Jevi retweeted

appreciate you guys being upfront.


New on Maple Max and Team: DeepSeek V4.1 Flash, abliterated.
Refusals removed from the model itself, so it works through security questions instead of declining them.
- 1M context
- Runs in the same attested enclaves as every Maple model
- Built for security research, code audits and red-teaming
Attackers already run uncensored models. Defenders shouldn't be stuck with "I can't help with that."

Jevi retweeted

I built an iOS jhana app this week. Access the full Burbea recordings, a timer + journal feature to track experiments. Enjoy!!
→ jhanaretreat.com/app (free forever)


just made some updates to the Rob Burbea jhana retreat app, and I'll be going through myself for the next 20 days (or until our baby arrives!)
→ jhanaretreat.com/


Jevi retweeted

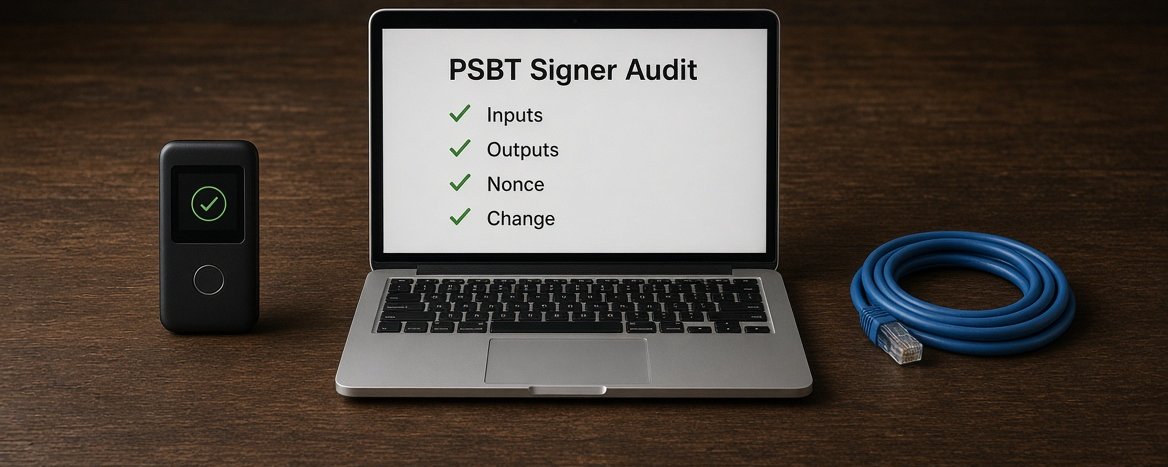
This is specifically about multi-vendor hardware wallets. Not about multisig in general.
If your threat model is “what if this hardware wallet is lying to me,” buying a second brand and running them in a multisig does not inspect the first one. It just gives you another device to trust. Now that you can actually check what the signer did with the PSBT, that particular reason for multi-vendor hardware multisig is weaker.
Collaborative custody is different. A service that holds one or two keys, handles inheritance, or takes the operational burden off someone who does not want full responsibility still has a real job. Those businesses exist for a reason and they are still useful. That is not the same thing as stacking three different hardware wallets because someone said different vendors are safer.
The article is about the first case. Not the second.

Every home needs hot water. Energy is already consumed to achieve this. This solution lets that energy served an additional purpose, which means the net utilization of the individual units of energy go further.
I would love to hear a legitimate counterargument to this.

Things are only going to get weirder from here.
Anyway, catch the game last night?

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Jevi retweeted

Being 45 is such a strange experience.
One minute, you want to make more money, get ridiculously fit, reinvent your entire life, and become the healthiest version of yourself.
The next minute, you want to disappear into the mountains for three weeks, turn your phone off, avoid everyone, and remember what peace feels like.
You want adventure, but you also want your own bed.
You want to be productive, but you also want to cancel every plan you’ve made.
You want to build wealth, travel the world, and accomplish big things, but you also consider 8:30 p.m. a perfectly reasonable bedtime.
And honestly? A mug of hot chocolate, a cozy blanket, and absolutely nobody asking you for anything sounds like the ultimate luxury.
Is this what getting older feels like, or have I just reached the age where peace and quiet are the real definition of success? 😂