






Pinned Tweet
Getting away from Twitter. You can find me on BlueSky while I rebuild followers and figure it out:
malwareforme.bsky.social
2
289
interesting google/doubleclick open URL redirection (often observed in phish) used in an LNK to retrieve payload
b42474e1198f00cbacb7d79f82daba71

4
347


new role opened for someone who loves crafting detections, threat intel, and all the goodness of smashing bad in email: jobs.careers.microsoft.com/g…
happy to answer any questions

wrapped up a basic privacy and security workshop for a local non profit that supports people experiencing IPV, sexual assault, and other forms of abuse. it’s a really cool way to give back to your community and create actionable impact. education is power!
9
499


Our work is never done 🙃

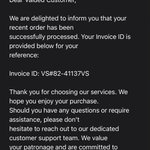
Microsoft has identified new Qakbot phishing campaigns following the August 2023 law enforcement disruption operation. The campaign began on December 11, was low in volume, and targeted the hospitality industry. Targets received a PDF from a user masquerading as an IRS employee.

ALT Screenshot of email from a user masquerading as an IRS employee
15
1,443
do you HATE miscreants? do you LOVE writing detections, hunting thru INSANE amounts of data, and protecting a LOT of orgs?
@Microsoft is hiring Detection Engineering/Threat Hunting roles for email security. work with some of the smartest folks in the game: jobs.careers.microsoft.com/g…
Some more #infosec #jobs Very curious who has experience using ML at scale to influence detections, but also understands the threat landscape/attack techniques in use— not just the models

Two more roles just dropped. Looking for security researchers who have an ML background or skills to assist in driving ML detection. #infosec #hiring #MachineLearning
jobs.careers.microsoft.com/g…
jobs.careers.microsoft.com/g…
3
541
Really incredible team and mission
We've posted a few roles for positions on my team. #infosec #hiring
Email Security Researcher
jobs.careers.microsoft.com/g…
Senior Email Security Researcher
jobs.careers.microsoft.com/g…
Principal Email Security Researcher
jobs.careers.microsoft.com/g…
3
515

you can teach anyone how to use the tools, understand the data, and integrate into workflows. the hardest thing is that you can't teach passion. that comes embedded with the person and is one of the biggest factors in candidate selection
This quoted post is unavailable.
1
639
If you’re not doing ssl decryption in sandboxes you’re goofin. Nice one @anyrun_app

🧙♀️Did you know that network rules from ANY.RUN contain some magic?✨For example, Telegram exfiltration is now not a simple certificate detection🔏Adding a little potion, allowed the spell with the number 8000167 to work with TLS packets🪄I hope you like my magic💫


Dedicating the chapter I wrote in Bluenomicon to @malwareforme - He's the Jack in the story and a true defender of the internet. <3

1
5
1,070
